Reported Documents (810 total)
Documents published alongside news reporting on the Snowden disclosures.
Sort: Title
Documents
-
EP-3E Collision: Cryptologic Damage Assessment and Incident Review [pdf]
A joint US Navy and NSA report from July 2001, prepared three months after a US spy plane was forced to land in China, assessing how far surveillance sources and methods were compromised and reviewing the emergency destruction that failed to prevent it. Damage to tactical SIGINT against the PRC is rated medium and overall SIGINT damage low, with the greatest loss the LUNCHBOX PROFORMA processor and MARTES signals analysis tools; COMSEC damage is rated low because keying material was superseded within 15 hours.
Programs: LUNCHBOX · MARTES · NICKELBACK · SENSOR PACER · PROFORMA · HULTEC · STRUM · TEXTA · RASIN · CRITIC · KLIEGLIGHT · XBIT · BLACKMAGIC · NOIWON · ZIRCON · MIDB · EOB-LITE · NIMROD · ARIEL · COBRA BALL · COMBAT SENT · RIVET JOINT · SEABOOT · SETTEE · KAMPUS · DRUID · RORIPA · MARKHAM · FOREJUDGE · SAM HEARTBURN · NOVELETTE · RSBN · BEGGAR HAWK · BEGGAR SHADOW · CAPSULE JACK · DISTANT WIND · DISTANT SENT · CHILING · RIBBED · UNACCENTED · SLIPSTICK · SIERRA ONEPeople: Meals, Charlie -
ESOC: Report on the experiences of one NSA worker [pdf]
A NSA intelligence analysis intern details their 2007 temporary assignment to the European Security Operations Center (ESOC), where they successfully established a new signals intelligence (SIGINT) mission targeting Angola's energy sector. The author describes the end-to-end process from initial research and target development to successful collection and the first intelligence product.
-
Event (SIGINT) [pdf]
5 p.This document explains that within GCHQ and NSA SIGINT operations, an “Event” refers to metadata about observable communications or user actions rather than message content, categorized into types like Communications, Presence, Social, and Geo-reference Events. These events are collected, stored in various databases, and analyzed through convergence and correlation processes, with standardized formats defined by Interface Control Documents such as INTERSTELLAR DUST (IDUST) and Actor Action (AA).
Programs: INTERSTELLAR DUST · HAUSTORIUM · SOCIAL ANTHROPOID · ACTOR-ACTION · SAMREF · GEOFUSION · HARD ASSOC · SALAMANCA · ASSOCIATION · BANYAN · MAINWAY · FASCIA · CULTWEAVE II · VOICESAIL · TEEDALE · PILBEAM · MUTANTBROTH · AUTOASSOC · MARBLEDGECKO · KARMAPOLICE · HRMAP · MEMORYHOLE · INFINITEMONKEYS · SOCIALANIMAL · AUTOTDI · SAMUELPEPYS · Mobile Applications Project · NGE · PPF · SLR -
Event RARE weekly summaries [pdf]
This document outlines GCHQ's ongoing surveillance efforts in Libya, focusing on intercepting and analyzing communications from the Libyan regime, including military command and control via mobile satellite phones and other communication channels. It details the use of advanced SIGINT tools and close cooperation with the NSA, US, and Canadian intelligence agencies to monitor key military targets and opposition forces, supporting both tactical military operations and strategic intelligence objectives.
People: Gaddafi, Muammar -
Events Analysis [pdf]
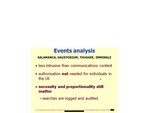
This GCHQ document explains authorization policies for querying metadata databases (SALAMANCA, HAUSTORIUM, THUGGEE, IMMINGLE), stating that metadata is "less intrusive than communications content" and that authorization is "not needed for individuals in the UK," though searches are logged and audited with necessity and proportionality considerations still applying.
-
Exceptionally Controlled Information Compartments (January 2013) [pdf]
This document, dated January 2013, provides a list of Exceptionally Controlled Information (ECI) compartments utilized by the NSA and its Five Eyes partners. This document categorizes highly sensitive intelligence programs by their codenames, three-letter trigraphs, and the specific organizations responsible for them. The primary organizations listed include TAO, NCSC, and CES. These compartments represent the highest level of information security, designed to restrict access to sensitive technical data and specific intelligence sources even among individuals with high-level security clearances.
Programs: AMBULANT · APERIODIC · AUNTIE · BLACKANT · BLACKAXE · BLACKBALL · BLACKCLOUD · BLACKHOLE · BLACKJACK · BLACKTIE · BLACKVULTURE · BLACKWIDOW · BOXWOOD · CELESTIALGLOBE · CHIEFDOM · CLICKUMBER · CRIMSONREGENT · CRIMSTONSTEAL · CRUMPET · DECKSTOP · DEVILFISH · DIXIESPRING · DOMINATE · FASTIDIOUS · FIRESCREEN · FIRSTDOWN · FISSURESALUTE · FLYLEAF · FORBIDDEN · FORBORNE · FOXHEAT · FREELUNCH · FROTHYTWOPACK · FURTIVERELIANCE · GOLDENCALF · HELLFIRE · HISTORY · HYSSOP · INVEIGH · KESSELRUN · LIGHTNINGTHIEF · LITTLECROWN · LONGSERPENT · MAGICSTROKE · MERCURYTAO · MUSICBOX · NITEHAWK · OCELLUS · PAINTEDEAGLE · PAWLEYS · PAWNSHOP · PENDLETON · PENDRAGON · PERKYAUTUMN · PHENYLDOUR · PICARESQUE · PICAROON · PIEDMONT · PITCHFORD · PLACEBO · POMPANO · PRESSURETWIN · REDHARVEST · REEFPOINT · REFRACTOR · REVELRY · RIVERROAD · RUBIOUS · SAILWINDS · SCABBARD · SILVERCLOUD · SINKGOAL · STAIRWELL · STARCHART · SUITESWIVEL · TRICKSHOT · WAXOFF · WHIPGENIE -
Excerpt from Hpc Overview 1011 [pdf]
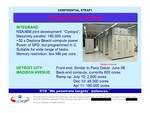
This document outlines the development of a highly advanced, massively parallel computing system, referred to as "Cyclops", a joint project between NSA and IBM. It is designed to perform complex tasks related to signals intelligence and code-breaking, with significant computing power, ramping up to 180,000 cores, and is referenced as a critical tool in penetrating target defenses.
-
Excerpt of May 2008 NSA Afghanistan Dataflow Analysis [pdf]
The document outlines how the NSA’s Real Time Regional Gateway (RT-RG) in Afghanistan progressively expanded from late 2007 through 2008 to ingest massive amounts of GSM, VHF, HF, and telephony metadata from dozens of locations across Afghanistan, supplemented by third-party “dirtbox” collection from allied nations such as the Netherlands, Denmark, Norway, Germany, and Spain. It details the specific collection sites, data types, and timelines (SPIN 9, 10, 11, etc.), illustrating how partner contributions and multiple signals sources fed into the RT-RG system to enable real-time intelligence.
Programs: FOURCORNERS · FORTRESS · WARRIOR · ECHIDNA · CASSIEOPIA · KARUS · SOUNDER · SNICK · TEMPOWOLFE · CALYPSO · TATTERAN · AIRBORNE · LEAVEBEHIND · UDEAUS · NELEUS · CROSSHAIR · SSO · DRT · RIVET JOINT · VOICESAIL“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
Expanding PRISM Sharing With FBI and CIA [pdf]
An SSO item describing two projects that widened PRISM sharing with the FBI and CIA: PRINTAURA software that compiles the tasked-selector list every two weeks for both agencies, and weekly operational PRISM news and guidance from the mission programme manager.
-
Expeditionary Access Operations: NSA’s Close Access Network Exploitation Program [pdf]
The document describes NSA/TAO’s Expeditionary Access Operations (EAO, S3283), a deployable arm that conducts human-enabled Close Access Network Exploitation (CNE) worldwide—using techniques from physical implants and gifted/compromised laptops to wireless injection tools (e.g., BLINDDATE, NITESTAND) and Wi-Fi geolocation—to support tactical customers like SOCOM, DIA, and task forces in Afghanistan, Iraq, and elsewhere. It details organization, tools, operational theaters (Bagram, Kabul, Kandahar, Stuttgart, Texas, etc.), specific operations (IRONPERSISTENCE, CLIMBINGSHIRT), and plans to formalize partnerships with USCYBERCOM and expand expeditionary CANO capabilities.
Programs: NITESTAND · HAPPY HOUR · BADDECISION · MASTERSHAKE · IRONPERSISTENCE · CLIMBINGSHIRT · BLINDDATE -
Exploiting Facebook traffic in the passive environment to obtain specific information [pdf]
A GCHQ Global Telecommunications Exploitation presentation on extracting information about Facebook users from passively collected traffic: why online social networks are a rich source, how Facebook's use of the Akamai content delivery network exposes a user's ID inside image URLs, and how profile and album images are then obtained through SPRING BISHOP, GODFATHER and JTRIG.
-
Exploiting Foreign Lawful Intercept (LI) Roundtable [pdf]
Top-secret PowerPoint presentation, "Exploiting Foreign Lawful Intercept Roundtable," highlights the agency’s strategy to exploit vulnerabilities in lawful intercept systems from telecom companies, such as Ericsson, Motorola, and Nokia, in countries like Mexico, Indonesia, and Egypt. The presentation also discusses NSA's use of various "Fingerprints" for identifying data and its collaboration with industry players and foreign lawful intercept systems.
“A Death in Athens” - The Intercept ↗ (2015-09-28) · “Americans and Greeks started the 2004 wiretaps together” - Kathimerini ↗ (2015-09-29) · Bamford, James · Petropoulos, Aggelos -
FAA Certification Renewals with Caveats [pdf]
This NSA document shows that after the FISA Court found NSA’s upstream internet collection unconstitutional and illegal, the agency’s response was less about reform and more about finding technical and procedural workarounds to keep surveillance running as usual. While the court ordered changes within 30 days, NSA officials planned to sequester and filter “higher-risk” data to appease the judge—not halt collection—revealing a mindset focused on preserving operations rather than addressing legal violations.
-
FAA702 comms memo [pdf]
This document details NSA's response to concerns raised by the FISA Court over the collection of non-targeted data in FAA-702 upstream collection. To mitigate the risk of continued acquisition, NSA is implementing temporary measures, including cautionary banners and updated processes, to prevent misuse of data that may not be directly related to tasked selectors.
People: Shea, Teresa H. -
FAA702 Glossary - Section 702 of the Fisa Amendments Act (FAA) [pdf]
This document outlines NSA rules under Section 702 of the FISA Amendments Act, which prohibit directly targeting U.S. persons or individuals inside the U.S., but quietly note a 2011 rule change allowing analysts to use U.S. person identifiers to query data already collected under 702—pending internal oversight. This effectively establishes a “backdoor search” capability enabling warrantless searches of Americans’ communications stored in NSA databases. Section 702 also gives the NSA authority to target without warrant the communications of foreign targets.
-
FAD FY 12 CCP Funding of Partners [pdf]
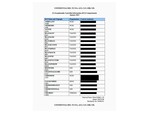
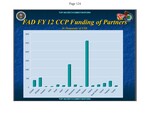
A Foreign Affairs Directorate slide showing Combined Cryptologic Program funding of foreign partners in fiscal year 2012, in thousands of dollars, across fifteen countries including Canada, Israel, Japan, Jordan, Pakistan, Taiwan and Thailand.
-
FAIRVIEW - Corp partner since 1985 [pdf]
1 p.A note describing FAIRVIEW as a corporate partnership dating to 1985 that gives access to international cables, routers and switches through a US company which is also “aggressively involved in shaping traffic to run signals of interest past our monitors”.
Programs: FAIRVIEW -
FAIRVIEW brief overview [pdf]
This document outlines the FAIRVIEW program, established in 1985, which leverages a corporate partner to exploit international communications through cables, switches, and routers. It is one of the NSA's top sources for metadata and serialized intelligence, supporting a wide range of targets including counter-terrorism, crime, and international security issues.
Programs: FAIRVIEW -
FAIRVIEW dataflow charts April 2012 [pdf]
This document outlines data flow diagrams that show how various types of sensitive communication, including voice, fax, and modem traffic, are handled through systems operated by the NSA and its partners. These partners include corporations, telecommunications companies, ISPs, and other entities involved in processing and managing the data through secure and classified channels. The document covers processing flows for various data types, metadata, and communications systems under NSA's control, detailing how data is routed, stored, and analyzed across different platforms and sites.
Programs: FAIRVIEW · SAGUARO · TURNSTILE · MESA · TITANPOINT · RIMROCK · MAILORDER · PINECONE · BLARNEY · STONEGATE · TINSEL · CONVEYANCE · FISHWAY · NUCLEON · PINWALE · SCISSORS · COURIERSKILL · DRIFTWOOD · ASDF · FALLOUT · MARINA · LOPERS · WEALTHYCLUSTER · PUPR · CLEARSIGHT · MIDFIELD · CADENCE · BUGCATCHER · WAYLAND · DESOTO · GATEKEEP · HIGHDECIBEL · XKEYSCORE · YANKEE · TOPROCK · FASCIA · DISHFIRE · SEAGULL · BIGDIPPER · CORPORATE · LILDIPPER · HAVASU · WEALTHYCLUSTER2 · RAGTIME · TUMULT · TATTOO · DARKTHUNDER · ICYTWINS · TML-STATUS · WATERFRONT · VULCANDEATHGRIP · STEELFLAUTA · UNITY · KEYCARD · UTT · BTUBE · ISLANDTRANSPORT · SSO · MAINWAY · SSDM · TUBE · TITANPOINTE · TURMOIL · VPCS“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “Titanpointe: The NSA’s Spy Hub in New York, Hidden in Plain Sight” - The Intercept ↗ (2016-11-16) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan -
FAIRVIEW site book [pdf]
The Fairview TDY Handbook provides essential guidelines for NSA employees travelling in support of the FAIRVIEW Program, detailing required training, security protocols, and travel procedures for both CONUS and OCONUS missions. It covers travel authorization, necessary courses, cover travel considerations, vehicle usage, and operational security (OPSEC) instructions for visits to partner and collection sites. The handbook emphasizes security, confidentiality, and appropriate conduct while interacting with partner organizations and traveling to sensitive locations.
Programs: FAIRVIEW · EAGLE · EDEN · TITANPOINT · PINECONE · TITANPOINTE · BLARNEY · STORMBREW · OAKSTAR · SILVER COLLAM · SSO · LITHIUM