Tag: satellite interception 17 documents
Search documents matching “satellite interception” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
AFRICAN INBOUND DVB-S2 CARRIER [pdf]
2009 GCHQ report documents the survey and tasking of an African inbound satellite data carrier (DVB-S2) carrying internet traffic from Nigerian, Kenyan, and Zambian ISPs, intercepted via the TERRAIN collection suite. Among the identified targets were Israeli diplomatic and defense-related selectors — including the Israeli Prime Minister, an Israeli UAV/drone entity, and the Israeli embassies in Abuja (Nigeria) and Nairobi (Kenya) — as well as the Palestinian Authority embassy to Belgium.
-
"Anarchist" Image Index [pdf]
Images collected through ANARCHIST, the GCHQ covername for a joint GCHQ/NSA SIGINT collection site on Mt. Troodos, Cyprus, drawn from imagery and pages in GCHQ's internal GCWiki.
Programs: ANARCHIST -
Bude Sigint Development Report [pdf]
GCHQ Bude SIGINT Development report fragment listing four "hits" from a satellite communication path, naming EU Commissioner Joaquin Almunia, French energy company Total (Total E and P), French defense contractor Thales (Thales Freight and Logistics), and the UN Institute for Disarmament Research (UNIDIR) as targets flagged in the agency's target database.
Programs: DRUMROLL -
Ghosthunter and the geolocating of internet cafes [pdf]
This document announces an NSA “R Spotlight” webcast introducing GHOSTHUNTER, a multi-agency geolocation program designed to locate Time Division Multiple Access (TDMA) VSAT Internet access points, particularly internet cafés across the Middle East and North Africa in support of U.S. military operations. By mid-2009, GHOSTHUNTER had successfully geolocated over 5,000 VSAT terminals across Middle East demonstrating its operational effectiveness and integration with broader intelligence efforts.
Programs: GHOSTHUNTER -
INTOLERANT – Who Else Is Targeting Your Target? Collecting Data Stolen by Hackers – SIDtoday SIDtoday [pdf]
A TOP SECRET SIDToday article from Menwith Hill Station describing how NSA and CSEC discovered and began exploiting INTOLERANT — a sophisticated email-stealing hacking operation targeting Indian diplomats, Central Asian diplomats, Chinese human rights defenders, Tibetan pro-democracy activists, Uighur activists and European officials — by intercepting the stolen emails as they transited satellite links, a technique internally called "fourth party collection" or "outsourcing SIGINT."
Programs: INTOLERANT -
JORDAN-BELGIUM [pdf]
2008 GCHQ report documenting the interception of a Jordan–Belgium satellite telecommunications link, through which British intelligence monitored call traffic and identified tasked surveillance targets including the Turkish foreign ministry, Palestinian Authority figures and Israeli MK Ahmad Tibi, along with other hits on Kurdish leadership, diplomats, and Jordanian government offices such as the Royal Protocol Office. The published copies redact different entries. Der Spiegel's and The Intercept's show the Turkish and Kurdish ones, Le Monde's (version 8BBAC) the Palestinian and Jordanian ones.
People: Tibi, Ahmad“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · “L’Autorité palestinienne et la Jordanie espionnées par les services américains et britanniques” - Le Monde ↗ (2016-12-07) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger · Follorou, Jacques -
-
JSA Restrictions [pdf]
This internal GCHQ wiki page outlines the specific operational restrictions imposed on the "Joint SIGINT Activity" (JSA), a collaborative US-German satellite surveillance site, explicitly forbidding the targeting of German citizens, "5 Eyes" nationals, and European economic interests. It includes a specific "blocklist" of domains (like .de and .at) and over 30 major entities—ranging from Airbus parent company EADS and Mercedes-Benz to the Bundeswehr and specialized defense contractors—that are off-limits because they are German companies using international top-level domains like .com or .net.
-
NWP NSA [pdf]
A January 2011 internal NSA newsletter from Yakima Research Station (YRS) covering the station's early history as the West Coast ECHELON/FROSTING satellite interception facility established in 1966 to collect INTELSAT communications, and its more recent expansion into cloud-based cyber threat discovery using FORNSAT and Special Source Operations data.
Programs: EARLYBIRD · FROSTING · TRANSIENT · ECHELON · JACKKNIFE · SAFEGUARD · STEAMS · CYBERQUEST · GINPENNANT · RUMBUCKET · CROSSBONES · SSO -
NWP2 NSA [pdf]
The July 2012 issue of the Yakima Research Station's internal newsletter, covering the station's upcoming 40th anniversary celebrations, its origins under the ECHELON programme for INTELSAT collection during the Cold War, and a Norwegian partner enablement operation, alongside routine staff and community content.
Programs: ECHELON -
PRIMARY FORNSAT COLLECTION OPERATIONS [pdf]
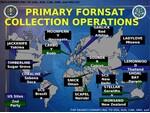
This document is a TOP SECRET NSA/CSS slide mapping the global locations of primary FORNSAT (foreign satellite) collection operations, showing U.S. and second-party ground stations used to intercept satellite communications worldwide. It illustrates the geographic spread and allied integration of NSA satellite surveillance infrastructure rather than specific technical capabilities.
-
SIERRA LEONE - BELGIUM [pdf]
May 2009 GCHQ report documents the interception of two satellite carriers linking Sierra Leone and Belgium (via INTELSAT 9F3), surveyed using the TERRAIN collection suite, which identified numerous email selectors of interest carried over the link. Among the hits was the email address of “Oles” — Octave Klaba, founder and CEO of OVH, Europe’s largest internet hosting company — flagged as a target alongside diplomatic and political addresses, though his presence on the list reflects metadata collection rather than proof his message contents were intercepted.
Programs: TERRAINPeople: Klaba, Octave -
SKIDROWE [pdf]
This document reveals the extensive surveillance capabilities of the NSA's SKIDROWE program at TITANPOINTE, specifically designed to intercept and analyze satellite communications and internet data. It highlights how intercepted data is processed and filtered through advanced systems like XKEYSCORE, which enables real-time intelligence gathering by sifting through massive amounts of digital content, including emails, calls, and internet activity.
Programs: SKIDROWE · WEALTHYCLUSTER2 · WEALTHYCLUSTER · TURNWEALTHY · VPCS · XKEYSCORE · GENESIS · CONTROLAND · ATM · FITBOY · DARKTHUNDER · FIP · METTLESOME · SKYFRAME · PVOICE · XXPY0012 · AGITATOR · STARPROC · SPELLBINDER · BLACKPEARL · BLACKALCHEMY · BLACKGOLD · BLACKFIRE · MONKEYMIND · BCD · EVVIPER · QUANTUM · MISTYPEAK · VALIANTSURF · GALLANTWAVE · SWINE · BLUESNORT · TOSSSWUNG · GNOMEVISION · GNOMEGOGGLES · HIDDENSALAMANDER · TURMOIL · PSC -
Special Collection Service - Pacific SIGDEV Conference March 2011 [pdf]
This document is a TOP SECRET briefing describing the Special Collection Service (SCS)—its organizational structure, global posture and strategic partnerships—and how SCS leverages advanced SIGINT and cyber capabilities (microwave, cellular, satellite, VPN/Internet exploitation, tools like INTERQUAKE/Einstein/Castanet/Birdwatcher) from embassy/PoP sites to collect, analyze and support intelligence and covert operations. It also outlines SCS modernization goals (unified IT core, cloud/virtualization, expanded cyber presence), operational authorities and mission advantages for enabling both SIGINT and HUMINT activities. See also Spiegel's 2013 reporting based on the same presentation (back then they only published two slides from this presentation): https://www.spiegel.de/international/germany/cover-story-how-nsa-spied-on-merkel-cell-phone-from-berlin-embassy-a-930205.html
-
TURBULENCE - APEX - Active/passive Exfiltration [pdf]
This 2009 NSA presentation details APEX (Active/Passive Exfiltration), a TURBULENCE program component that combines passive collection infrastructure with active TAO implants to exfiltrate VPN and VoIP traffic from deep within target networks back to NSA collection systems. The system uses the FASHIONCLEFT protocol to tunnel captured packets through compromised routers and network devices, enabling decryption of VPN tunnels and collection of voice communications that would otherwise be invisible to passive surveillance.
Programs: TURBULENCE · TURMOIL · HAMMERSTEIN · HAMMERCHANT · FASHIONCLEFT · TUTELAGE · TURBINE · TRAFFICTHIEF · XKEYSCORE · ANALYTICS · PRESSUREWAVE · TOYGRIPPE · POISONNUT · FLAXENPRECEPT · FOGYNULL · FUNNELAPS · SHELLGREY · METROTUBE · VINYLSEAT · OLYMPUS · UNITEDRAKE · FIGBUILD · SURPASSPIN · ROOTKNOT · OPTICPINCH · SEAGULFARO · TREBLECLEF · CONVEY · PINWALE · SWEEPFORWARD · QUANTUM · KEYCARD · ASDF · TUBE · PUZZLECUBE · WEALTHYCLUSTER2 · COALSHOVEL · HAMMERMILL · ISLANDTRANSPORT · FASCIA · TURBINIE · APEX · PPF · AEG · FIP · SSO · PICARESQUE · PSP · IVE · PSC · CHIMNEYPOOL · CORESSC · FLASHHANDLE · IBRIDGE · CORALREEF · VAO · NUCLEON · PIQBLADE“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
VALIANTSURF [pdf]
An NSA WikiInfo page for VALIANTSURF — the coverterm for NSA's IPSec VPN decryption capability within the TURMOIL collection platform — describing the four data flow types for intercepting and breaking encrypted VPN traffic, the full deployment roster across collection sites including Menwith Hill, SMOKYSINK, MUSCULAR, CROSSCUT and others, and the architectural taxonomy of the VALIANTSURF programme including its MALIBU and WAIMEA processing architectures and their relationship to LONGHAUL, POISONNUT and GALLANTWAVE.
Programs: VALIANTSURF · TURMOIL · TURBULENCE · HOOKED · HOOKEDHAND · CINDER · CINDERASH · CINDERTRACK · SCARLETFEVER · LONGHAUL · FALLOUT · TOYGRIPPE · PICARESQUE · XKEYSCORE · PRESSUREWAVE · ASDF · MAILORDER · TUBE · KEYCARD · POISONNUT · ISLANDHIDEAWAY · ISLANDTRANSPORT · EXOPUMP · CORALREEF · PINWALE · TUSCARORA · ONEROOF · CONVEYANCE · TURTLEPOWER · WDM · CADENCE · UTT · SCISSORS · FISHWAY · BTUBE · DNCA · ROMULANALE · GALLANTWAVE · ROMULANGAWK · ROMULANGOWL · MALIBU · WAIMEA · WAIMEAVISAGE · ROMULANVISAGE · WAIMEAVISE · ROMULANVISE · APEX · METROTUBE · MADFORGE · JSORCERER · CROSSCUT · CIET · LATTICE · STARQUAKE · SARATOGA · MUSCULAR · SMOKYSINK · SLACKKEY · TUMMS · PURGE · SURGE · NUCLEON · SPAGIC · PPF · SOAP · TUMULT · FIP · PIQBLADE · DEEPDIVE · IBRIDGE -
ZAIN INTRANET NETWORK ENGINEERING [pdf]
2009 GCHQ report documents the sampling and tasking of a satellite data carrier linking Gabon and Belgium that carried the internal corporate intranet of telecom operator Zain (formerly MTC Vodafone), through which engineers exchanged technical data via SMTP email. The intercept surfaced email selectors belonging to staff across multiple telecom operators — including Zain subsidiaries, Orange Mali, Saudi Telecom, MTC Touch (Lebanon), Tunisie Telecom, and Celtel entities in Niger and Nigeria — reflecting the agency’s systematic targeting of telecom employees as a potential entry point into operators’ internal networks.