Tag: diplomatic surveillance 30 documents
Search documents matching “diplomatic surveillance” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
3G: impact and update - SDF Nov 09 [pdf]
This 2009 top-secret presentation from Australia’s Defence Signals Directorate (DSD) detailing 3G mobile network rollouts in Southeast Asia and identifying Indonesian President Susilo Bambang Yudhoyono, his wife, and senior officials as surveillance targets. It includes handset information, call data records, intercepted call attempts, and outlines plans for continued interception of Indonesian leadership communications.
-
'4th Party Collection': Taking Advantage of Non-Partner Computer Network Exploitation Activity SIDtoday [pdf]
This January 2008 SIDtoday article from Menwith Hill Station describes "4th Party Collection"—an NSA technique exploiting non-Five Eyes nations' computer network operations by passively intercepting their stolen data—with the example of NSA monitoring Kurdistan Democratic Party's deployment of Perfect Keylogger commercial spyware against targets in Iran and Iraq, including people with links to the Kurdistan Regional Government and Iraqi Ministry of Foreign Affairs computers, capturing keystrokes, passwords, chat logs, and documents that traditional signals intelligence would never collect. The operation reveals KDP intelligence services systematically compromised internet cafés and Iraqi Ministry of Foreign Affairs computers, with exfiltrated data routing to email addresses in Erbil registered to terminals associated with Kurdish intelligence, which NSA then intercepts and repurposes for its own intelligence production.
-
BLARNEY Team Provides Outstanding Support to Enable UN Security Council Collection [pdf]
An SSO item describing how the BLARNEY team, NSA lawyers and the FBI obtained four FISA court orders in days — for Gabon, Uganda, Nigeria and Bosnia — after Ambassador Susan Rice asked for SIGINT on undecided countries ahead of the June 2010 UN Security Council vote on sanctions against Iran.
Programs: BLARNEYPeople: Rice, Susan -
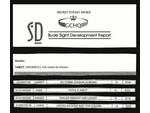
Bude Sigint Development Report [pdf]
GCHQ Bude SIGINT Development report fragment listing four "hits" from a satellite communication path, naming EU Commissioner Joaquin Almunia, French energy company Total (Total E and P), French defense contractor Thales (Thales Freight and Logistics), and the UN Institute for Disarmament Research (UNIDIR) as targets flagged in the agency's target database.
Programs: DRUMROLL -
Center for Content Extraction - Content Extraction Analytics, SIGDEV End-to-End Demo [pdf]
This document is a technical showcase demonstrating the capabilities of an NSA content‑extraction program, using political leaders and diplomatic figures (such as Angela Merkel) as illustrative examples. It presents how automated language technology can extract, organize, and scale intelligence data from intercepted material.
Programs: MARINA · CYBERTRANS · PAINTBALL · SYNAPSE · NYMROD · THUNDERCLOUD · JOURNEYMAN · GOLDENRETRIEVER · SOCIOPATH · LEXHOUND · HERESYITCH · HLT · TKB · EKS -
Classification Guide Title/Number: Cuban Missile Crisis, 10-18 [pdf]
A 2008 NSA classification guide governing what may be disclosed about the agency's SIGINT activity during the Cuban Missile Crisis, showing that elements of 1960s collection against Cuba and the USSR were still controlled decades later.
-
Close Access SIGADS [pdf]
A 10 September 2010 NSA reference list of Close Access SIGADs revealing the codenames, locations and collection methods used to bug the embassies and UN missions of 38 targets — including US allies France, Italy, Greece, Japan, India, Mexico, South Korea and the EU — through implants, computer-screen capture, hard-drive imaging and electromagnetic emanation collection, most conducted against diplomatic facilities in Washington DC and New York.
Programs: KATEEL · POCOMOKE · MERCED · BANISTER · PERDIDO · MAGOTHY · BLACKFOOT · WABASH · NAVARRO · POWELL · KLONDIKE · NASHUA · OSAGE · OSWAYO · BRUNEAU · HEMLOCK · MULBERRY · ALAMITO · FLEMING · DOBIE · SULPHUR · REQUETTE · YUKON · WESTPORT · NAVAJO · PANTHER · LIFESAVER · HIGHLANDS · VAGRANT · MINERALIZ · DROPMIRE · PBX · MAGNETIC · OCEAN · GENIE · BLACKHEART · CRYPTOENABLED · CUSTOMS · DEWSWEEPER · RADON · MINERALIZE · COOP · STARRUBY · TRASHINT“No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Espionnage de la NSA : la diplomatie française était sur écoute aux Etats-Unis” - Le Monde ↗ (2013-10-22) · “Da qui ci spiano gli americani” - L'Espresso ↗ (2013-12-05) · Greenwald, Glenn · Follorou, Jacques · Maurizi, Stefania -
Customers Can Help SID Obtain Targetable Phone Numbers SIDtoday [pdf]
US officials sometimes supply SID with their rolodexes. Although some of these numbers are public and others are not used to discuss sensitive information, they have lead the NSA to other useful numbers.
Marking: CONFIDENTIALPrograms: OCTAVEThe Intercept ↗ (2019-05-29) · “NSA monitored calls of 35 world leaders after US official handed over contacts” - The Guardian ↗ (2013-10-24) · Ball, James -
DROPMIRE on the Cryptofax at the EU Embassy D.C. [pdf]
This document reveals that the NSA secretly targeted EU diplomatic communications through a program called DROPMIRE, which involved placing surveillance implants on encrypted fax machines at the EU Embassy in Washington, D.C. This operation was part of a broader effort to spy on 38 foreign embassies and missions—including allies such as France, Italy, and Greece—to gain inside knowledge of policy debates and diplomatic positions.
Programs: DROPMIRE -
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
GCSB has identified an MFA data link [pdf]
A short extract from an April 2013 NSA document recording that GCSB had identified a Chinese Ministry of Foreign Affairs data link between the Chinese Consulate and the Chinese Visa Office in Auckland, and that NSA and GCSB had verbally agreed to mount a joint passive and active operation against it.
“Leaked papers reveal NZ plan to spy on China for US” - The New Zealand Herald ↗ (2015-04-19) · “New Zealand Plotted Hack on China With NSA” - The Intercept ↗ (2015-04-18) · Fisher, David · Gallagher, Ryan · Hager, Nicky -
Guidelines for the classification of NSA SIGINT details (1945-1967) [pdf]
This document is an NSA classification guide that defines how and why historical SIGINT material from 1945–1967 remains classified, in many cases for 75 years. It systematically explains which intelligence activities, targets, partnerships, and technical methods must stay protected because they still reveal sensitive sources, methods, and diplomatic equities.
-
How do we do SIGDEV or private networks? [pdf]
Top Secret SIGINT Development (SIGDEV) briefing explains how analysts conduct reconnaissance on private networks, noting that many targets rely on them and that 30–40% of traffic surveyed in BLACKPEARL has at least one private endpoint. It demonstrates the ROYALNET tool and its analytics for identifying network features, NetStrings, and links likely to carry a target’s traffic, with named targets and feature sets including Google’s infrastructure, the SWIFT banking network, the French Ministry of Foreign Affairs, Brazil’s Petrobras, and Huawei.
People: Higgins, Jean -
Intelligently filtering your data: Brazil and Mexico case studies [pdf]
These documents reveal that the NSA conducted targeted surveillance operations against high-profile Brazilian and Mexican figures, including President Dilma Rousseff and presidential candidate Enrique Peña Nieto, using advanced contact-graph filtering and data analysis techniques to extract relevant intelligence from intercepted communications. These documents show how NSA analysts systematically developed intelligence on foreign leaders during election periods and diplomatic activities, framing it as “target development,” but in practice enabling deep political espionage under the guise of analytical innovation.
“Veja os documentos ultrassecretos que comprovam espionagem a Dilma” - O Globo ↗ (2013-09-02) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn -
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
List of foreign governments and organizations authorized for surveillance [pdf]
This exhibit lists the 193 foreign governments as well as foreign factions, political organizations and other entities that were part of a 2010 certification approved by the Foreign Intelligence Surveillance Court. These are the entities about which the NSA may conduct surveillance, for the purpose of gathering foreign intelligence. Each year a new certification must be approved by the court to permit such surveillance under Section 702 of the FISA Amendments Act.
-
NSA Telegraph: SIGDEV Efforts in Support of the United Nations Framework for Climate Change Conference, Bali, Indonesia [pdf]
This NSA document from Joint Defence Facility Pine Gap reveals that the agency conducted surveillance operations during the 2007 UN Climate Change Conference in Bali, monitoring communications of Indonesian security forces, locating satellite uplinks including video feeds from the conference facility, and compromising the mobile phone number of Bali's Chief of Police. The operation, conducted in coordination with Australia's Defence Signals Directorate (DSD), was framed as a "self-initiated network development effort" to prepare for potential "emergency" collection, but effectively demonstrates intelligence agencies spying on a major international environmental and diplomatic gathering attended by 10,000 participants from 190 countries.
Programs: RAINFALL -
NSA's Offensive and Defensive Missions: The Twain Have Met SIDtoday [pdf]
The document outlines a case where NSA’s defensive malware analysis enabled offensive SIGINT teams to gain sustained access to a Chinese command-and-control server, allowing NSA to intercept intelligence China had stolen from the United Nations through a method known as fourth-party collection.
-
NSA/CSS EXCEPTIONALLY CONTROLLED INFORMATION (ECI) 2003 [pdf]
This document acts as the definitive "master list" of the NSA’s Exceptionally Controlled Information (ECI) compartments as of September 2003. While standard Top Secret information is shared among those with the appropriate clearance and a "need to know," ECIs are even more restricted—they are "silos" of information where access is granted only by the Director of the NSA (DIRNSA). This list provides a rare architectural view of the NSA's most sensitive secrets, ranging from illegal money laundering stings to the subversion of global encryption standards.
Programs: PAWLEYS · ABEYANT · APERIODIC · AUNTIE · AMBULANT · FIRSTDOWN · BOATMEN · BOXWOOD · BULLET · CHILLY · CLERIC · CONQUERER · KLAMATH · DECKSTOP · DICHOTOMY · DILEMMA · RAMPART-M · DOMINATE · FLEXURE · ENSIGN · STAIRWELL · ESCAPEE · STATEROOM · EVADEYIELD · FORBIDDEN · FORBORNE · GRAYSCALE · HELLFIRE · HISTORY · INVEIGH · INVENT · LYSERGIC · MISCHIEF · RAGTIME · BLARNEY · OPALESCE · TAREX · PENDLETON · PIEDMONT · PITCHFORD · REFRACTOR · RUBIOUS · STEREO · STRESSFUl · TAXONOMY · VISITOR · WASHBURN -
PROFILING SSL AND ATTRIBUTING PRIVATE NETWORKS [pdf]
A TOP SECRET GCHQ presentation introducing two prototype cloud analytics — FLYING PIG, a knowledge base for investigating TLS/SSL traffic at scale across approximately 20 billion events per week, and HUSH PUPPY, a tool for attributing private network traffic to identifiable organisations — with live interface screenshots demonstrating queries against mail.ru infrastructure and operational successes including identification of the Afghan Ministry of Defence network and a foreign Ministry of Foreign Affairs VSAT network.
Programs: FLYINGPIG · HUSHPUPPY · QUICKANT · GEOFUSION · LEGIONJADE · LEGIONRUBY · MAKERSMARK · XKEYSCORE · NOSEYPARKER“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Greenwald, Glenn · Kaz, Roberto · Casado, José