Tag: Google 30 documents
Search documents matching “Google” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
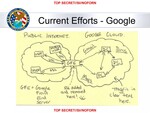
Current Efforts - Google [pdf]
The famous NSA slide from the MUSCULAR program showing where Google's encryption is stripped away — a hand-drawn diagram of Google's cloud architecture annotated with "SSL Added and removed here!" beside a smiley face, marking the exact point where NSA and GCHQ intercepted Google user data flowing unencrypted between Google's data centers.
-
Automated NOC detection [pdf]
This slide deck lays out how GCHQ and Canada’s CSEC systematically identified and penetrated Network Operations Centers—most notably Belgacom—by automating NOC discovery and weaponizing that mapping for QUANTUM INSERT attacks. It reads like a blueprint for turning router configs, metadata, and bulk scans into cookie-based targeting against telecom engineers inside core networks.
Programs: SURGE · NOCTURNALSURGE · RT · NACSHACK · CHAINGUARD · TIDALSURGE · GLOBALSURGE · PENTAHO · OLYMPIA · HYPERION · TERMINALSURGE · HACIENDA · QUANTUMINSERT · MUTANTBROTH · OPSOCIALIST · SAMUEL PEPYS · GEOFUSION · FIVEALIVE · NRTA · RADIUS“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
BLACK HOLE ANALYTICS, ADD/SD briefing, September 2009 [pdf]
This September 2009 GCHQ briefing describes the BLACK HOLE analytics infrastructure and Next Generation Events (NGE) project, which planned to scale from ~8 10-gigabit connections to ~200 10Gs by March 2011, storing intercepted data in massive flat-file repositories at Benhall and Bude before loading it into "Question Focused Dataset" (QFD) databases that power surveillance tools like MUTANT BROTH, KARMA POLICE, INFINITE MONKEYS, and others. The document outlines how "probes" extract Target Detection Identifiers (TDIs) from intercepted data feeds, store them in BLACK HOLE repositories, then enable analysts to profile targets' online activities, create social networks, investigate websites and forums, track web searches and Google Earth usage, and perform large-scale data mining across internet and telephony data.
Programs: BLACKHOLE · MUTANTBROTH · AUTOASSOC · INFINITEMONKEYS · KARMAPOLICE · SOCIALANIMAL · HRMAP · MEMORYHOLE · MARBLEDGECKO · HARDASSOC · SAMUELPEPYS · BLAZINGSADDLES · TELLURIAN · BUFFER · DISTILLERY · LOOKINGGLASS · NGEPeople: bin Laden, Osama -
BOUNDLESSINFORMANT – Frequently Asked Questions [pdf]
This document outlines the NSA’s internal metadata analysis tool, designed to provide real-time visualizations and statistics on global SIGINT collection by country, organization, and site. It explains the tool’s purpose, data sources, technical architecture, views, data limitations, and the process for requesting feature enhancements, highlighting its role in cataloging surveillance activity without human intervention.
Programs: BOUNDLESSINFORMANT · ASDF · GAO · RAMPART-A · SPINNERET · GM-PLACE · FALLOUT · TUSKATTIRE · FASCIA · MUSCULAR · Terrestrial RF · MachineShop · TurkeyTower · CloudBase · GXT · ExtGWT · JUGGERNAUT · LOPER · FLAWMILL · SSO · MAPREDUCE“Boundless Informant: the NSA's secret tool to track global surveillance data” - The Guardian ↗ (2013-06-08) · “NSA-files repeatedly show collection of data «against countries» - not «from»” - Dagbladet ↗ (2013-11-22) · “New NSA Revelations: Inside Snowden's Germany File” - Der Spiegel ↗ (2014-06-18) · Greenwald, Glenn · MacAskill, Ewen · Becker, Sven · Gude, Hubert · Horchert, Judith · Müller-Maguhn, Andy · Poitras, Laura · Reißmann, Ole · Rosenbach, Marcel · Schindler, Jörg · Schmid, Fidelius · Sontheimer, Michael · Stark, Holger -
Converged Analysis of Smartphone Devices [pdf]
This 2010 document outlines NSA methods for identifying, processing, and exploiting data from smartphones by targeting both telephony and digital network intelligence (DNI). It details how analysts use tools like XKEYSCORE and metadata extraction to collect geolocation, app data, call logs, unique identifiers, and user activity from popular mobile apps and services (e.g., Google Maps, Facebook, Flickr), emphasizing the intelligence potential of smartphones as rich surveillance targets.
People: Kuruc, Paula -
Discovery SIGINT Targeting Scenarios and Compliance [pdf]
This document is a top-secret NSA guidance manual detailing SIGINT targeting scenarios, compliance procedures, and legal guidance for querying foreign actors, malware, and potentially U.S.-linked systems, including considerations for minimizing incidental collection of U.S. persons’ communications. It outlines specific rules, approvals, and exceptions for using SIGINT tools, foreign intelligence tasks, and cases involving ambiguous or dual-use selectors like WikiLeaks, The Pirate Bay, and foreign actors operating through U.S. infrastructure.
-
DNI101 [pdf]
This TOP SECRET training guide, "DNI 101," provides a workflow for Digital Network Intelligence analysts on how to investigate a target's email address, detailing the specific tools, databases, and methodology used, and stressing the critical difference between initial open-source/classified research and the active "targeting" of raw SIGINT repositories like XKEYSCORE, PINWALE, and MARINA.
Programs: NKB · FOXTRAIL · FOREMAN · PINWALE · LIONHEART · XKEYSCORE · DISHFIRE · MARINA · MECWEB · MAINWAY · TRAFFICTHIEF · MAUI · ANCHORY · M3 · INTELLINK · HOMEBASE · PROTON · UTT · CADENCE · SPEEDBUMP · TUNINGFORK · MASTERSHAKE · BLACKPEARL · JACKSPARROW · ROADBED · STORYDUTY · LIONROAR · DOPHONE · UIS -
Email from GCHQ to NSA about targeting realms in MONKEY PUZZLE [pdf]
Email from GCHQ's MONKEY PUZZLE development team to NSA clarifying that the system only supports deploying targeting for four specific selector realms: emailAddr, google, msnpassport, and yahoo, while still accepting other realms into the system pool.
Marking: SECRET -
FAA Certification Renewals with Caveats [pdf]
This NSA document shows that after the FISA Court found NSA’s upstream internet collection unconstitutional and illegal, the agency’s response was less about reform and more about finding technical and procedural workarounds to keep surveillance running as usual. While the court ordered changes within 30 days, NSA officials planned to sequester and filter “higher-risk” data to appease the judge—not halt collection—revealing a mindset focused on preserving operations rather than addressing legal violations.
-
FISA Amendments Act Certifications and Operations [pdf]
This document exposes how, after the FISA Court found flaws in NSA’s upstream surveillance in 2011, the agency pushed through new certifications on schedule the following year and quietly used taxpayer money to cover millions in compliance costs for PRISM companies like Google and Yahoo. Rather than scaling back unconstitutional collection, the NSA treated the ruling as a logistical hurdle to manage with corporate partners, underscoring its deep financial and operational entanglement with major tech firms. Check also the document "FAA Certification Renewals with Caveats"
Programs: PRISM -
How do we do SIGDEV or private networks? [pdf]
Top Secret SIGINT Development (SIGDEV) briefing explains how analysts conduct reconnaissance on private networks, noting that many targets rely on them and that 30–40% of traffic surveyed in BLACKPEARL has at least one private endpoint. It demonstrates the ROYALNET tool and its analytics for identifying network features, NetStrings, and links likely to carry a target’s traffic, with named targets and feature sets including Google’s infrastructure, the SWIFT banking network, the French Ministry of Foreign Affairs, Brazil’s Petrobras, and Huawei.
People: Higgins, Jean -
How the NSA Accesses Smartphone Data [pdf]
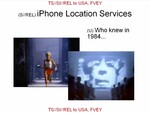
This document reveals how the NSA and its Five Eyes partners developed sophisticated methods to exploit iPhone location services and BlackBerry communications, framing smartphone users as “zombies” willingly sharing data. It includes examples of intercepted geolocation data and decrypted BlackBerry emails, illustrating targeted surveillance capabilities against both consumer and government communications.
-
Location Cookies [pdf]
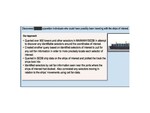
These slides contain excerpts from an April 2013 National Security Agency presentation detailing signal surveillance techniques and successes. They reveal that the NSA and its British counterpart, Government Communications Headquarters (GCHQ), use a Google-specific tracking cookie to pinpoint targets for hacking.
-
Mobile Apps Checkpoint Meeting Archives [pdf]
This GCHQ document tracks project checkpoints from December 2009 to July 2010, focusing on the rollout and operationalization of mobile apps, TERRAIN system upgrades, GTP/GRX access, and converged event processing. Key themes include coordinating multi-team dependencies, addressing technical gaps in handset and app data characterization, and ensuring timely delivery of milestones like MIP-1.
Programs: TERRAIN · PRESTON · XKEYSCORE · BEGAL · TAMING PASTRIES · MILKWHITE · MVR · SOCIAL ANTHROPOID · INTEGER SPIN · MUTANT BROTH · GEO FUSION · MARBLED GEKO · BLACKHOLE · ACTOR ACTION · TRAFFICMASTER · HARD ASSOC · MIRTF · HEARTBEAT · SILVER LINING · GREENHEART · EREPO · MAGLITE · POKERFACE · BOSTROM · MIDDLESEX GREEN · ENCHANTERSS · HAUSTORIUM · SALAMANCA · BROADOAK · MONKEY PUZZLE · TACHO · EREPO GAMMA · NINJA · PEBBLE BED · GOLDEN EYE · STRAPROC · STARPROC · LOOKING GLASS · SORCERER · SOCIAL ANIMAL · GTE · NGE · PPF · IIB · UDAQ · MES · TERRAINS · CCDF · SINO · GDR · OSDS · LECKWITH -
Mobile Networks in My NOC World [pdf]
This TOP SECRET STRAP 2 GCHQ document outlines the “MyNOC” operations, a specialized Network Operations Centre used by the UK’s GCHQ to coordinate cyber exploitation of international mobile and telecom infrastructure, with a particular focus on Belgacom’s GRX network under “Operation Socialist” (OP SOCIALIST). It details operational planning, toolsets, personnel roles, network mapping, QUANTUM INSERT targeting, and successful infiltration strategies that enabled CNE (Computer Network Exploitation) access to key Belgacom systems and staff infrastructure.
Programs: HIGHNOTE · COPPERHEAD · NEXUS · CADDIS · BRENT · RUSSETT PHONE · CERBERUS · E-BEAM · PIA · JEDI · WYLEKEY · INTERACTION · EREPO · QUANTUM · WOODCUTTER · MUTANT BROTH · QUANTUM INSERT · NRTA · MERION ZETA · JTRIG · A-SPACE · GEOFUSION“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · “Britain's GCHQ Hacked Belgian Telecoms Firm” - Der Spiegel ↗ (2013-09-20) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Mobile Theme Briefing (May 28, 2010) [pdf]
This 2010 GCHQ briefing document outlines the “Mobile Applications Project,” which aims to expand intelligence capabilities to exploit the growing shift from fixed to mobile internet usage. It details objectives for targeting mobile apps and roaming network traffic (GRX), enabling converged analysis of voice, text, command-and-control, and geolocation data across multiple mobile platforms such as iPhone, Symbian, Android, and Windows Mobile. See also: EFF_-_20140128-guard-leaky_phone_apps_0 (includes other slides from the same slideset)
Programs: Mobile Applications Project -
PRISM planning slide (PRISM briefing 1) [pdf]
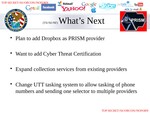
A PRISM slide headed 'What's Next': plans to add Dropbox as a PRISM provider, add a cyber threat certification, expand collection from existing providers, and change the UTT tasking system to allow phone-number tasking.
-
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
Private Networks are Important [pdf]
A slide arguing that many targets use private networks — Google's infrastructure, the SWIFT network, Gazprom, Aeroflot, the French foreign ministry, Warid Telecom and Petrobras — with a survey finding that 30 to 40 percent of BLACKPEARL traffic has at least one private endpoint.
Programs: BLACKPEARL -
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark