Tag: GPRS 17 documents
Search documents matching “GPRS” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Real Life Stats from GPRS work [pdf]
GCHQ’s TOP SECRET briefing touts real-time interception of diplomats’ smartphone traffic at the 2009 G20—especially BlackBerry—feeding live messages and newly discovered selectors to analysts and UK ministers to shape summit outcomes. It’s a snapshot of summit espionage turned into a policy tool: exploit the smartphone dependence of foreign delegations, deliver actionable SIGINT on demand.
“GCHQ intercepted foreign politicians' communications at G20 summits” - The Guardian ↗ (2013-06-16) · “For the NSA, espionage was a means to strengthen the US position in climate negotiations” - Dagbladet Information ↗ (2014-01-30) · MacAskill, Ewen · Davies, Nick · Hopkins, Nick · Borger, Julian · Ball, James · Gjerding, Sebastian · Geist, Anton · Moltke, Henrik · Poitras, Laura -
THIEVING MAGPIE: Using on-board GSM/GPRS services to track targets [pdf]
A GCHQ capability-development presentation on THIEVING MAGPIE, which uses the on-board GSM/GPRS services airlines offer to track targets in flight: comms backhauled over Inmarsat BGAN and collected via SOUTHWINDS, registration events tied to a flight number or callsign in near real time, events for BlackBerry handsets with their PINs and associated e-mail addresses, and content tasked into datastores with unselected traffic to XKEYSCORE.
“US and Britain refine their ability to tap into airline passenger’s mobile phones while they are in the air” - Le Monde ↗ (2016-12-07) · “American and British Spy Agencies Targeted In-Flight Mobile Phone Use” - The Intercept ↗ (2016-12-07) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Follorou, Jacques · Greenwald, Glenn -
Analyzing Mobile/Cellular DNI in XKEYSCORE, May 2009 [pdf]
The XKEYSCORE document explains how the agency analyzes mobile/cellular device internet usage by collecting and processing both converged DNI/DNR data within cellular networks and traditional internet traffic, using various tools and indicators to identify mobile users even when their device type isn't immediately evident. The document demonstrates how the system can track mobile internet activity across applications like Yahoo Mail and identifies devices through various technical "hints" including MSISDN codes, browser fingerprints, and user agent strings.
-
AURORAGOLD Working Group [pdf]
The "AURORAGOLD Working Group" briefing is a highly classified SIGINT development presentation from June 2012 that outlines the NSA's progress in mapping the global mobile landscape (GSM/UMTS/LTE). It focuses on the project's "value proposition": providing an exhaustive database of network identifiers and technical configurations—often obtained by intercepting internal company documents—to support tactical military operations and long-term surveillance forecasting.
Programs: AURORAGOLD · UTT · XKEYSCORE · CADENCE · JUBILEECORONA · RONIN · NKB · GLOBALTIPPER · PINWALE -
Automated NOC detection [pdf]
This slide deck lays out how GCHQ and Canada’s CSEC systematically identified and penetrated Network Operations Centers—most notably Belgacom—by automating NOC discovery and weaponizing that mapping for QUANTUM INSERT attacks. It reads like a blueprint for turning router configs, metadata, and bulk scans into cookie-based targeting against telecom engineers inside core networks.
Programs: SURGE · NOCTURNALSURGE · RT · NACSHACK · CHAINGUARD · TIDALSURGE · GLOBALSURGE · PENTAHO · OLYMPIA · HYPERION · TERMINALSURGE · HACIENDA · QUANTUMINSERT · MUTANTBROTH · OPSOCIALIST · SAMUEL PEPYS · GEOFUSION · FIVEALIVE · NRTA · RADIUS“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Belgacom connections [pdf]
A "Belgacom connections" map lays out the carrier’s sprawling roaming and backbone interconnects, precisely the arteries GCHQ wanted to get access into. Under Operation Socialist GCHQ successfully gained access to Belgacom’s infrastructure, including internal employee computers and encrypted and unencrypted streams of private communications handled by the company.
Programs: CARBONROD“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Converged Analysis of Smartphone Devices [pdf]
This 2010 document outlines NSA methods for identifying, processing, and exploiting data from smartphones by targeting both telephony and digital network intelligence (DNI). It details how analysts use tools like XKEYSCORE and metadata extraction to collect geolocation, app data, call logs, unique identifiers, and user activity from popular mobile apps and services (e.g., Google Maps, Facebook, Flickr), emphasizing the intelligence potential of smartphones as rich surveillance targets.
People: Kuruc, Paula -
In-Flight GSM [pdf]
This NSA presentation outlines how the agency is reacting to the growth of mobile phone services on board commercial aircraft.
-
Mobile Networks in My NOC World [pdf]
This TOP SECRET STRAP 2 GCHQ document outlines the “MyNOC” operations, a specialized Network Operations Centre used by the UK’s GCHQ to coordinate cyber exploitation of international mobile and telecom infrastructure, with a particular focus on Belgacom’s GRX network under “Operation Socialist” (OP SOCIALIST). It details operational planning, toolsets, personnel roles, network mapping, QUANTUM INSERT targeting, and successful infiltration strategies that enabled CNE (Computer Network Exploitation) access to key Belgacom systems and staff infrastructure.
Programs: HIGHNOTE · COPPERHEAD · NEXUS · CADDIS · BRENT · RUSSETT PHONE · CERBERUS · E-BEAM · PIA · JEDI · WYLEKEY · INTERACTION · EREPO · QUANTUM · WOODCUTTER · MUTANT BROTH · QUANTUM INSERT · NRTA · MERION ZETA · JTRIG · A-SPACE · GEOFUSION“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · “Britain's GCHQ Hacked Belgian Telecoms Firm” - Der Spiegel ↗ (2013-09-20) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
New Technology Making Waves: MMS SIDtoday [pdf]
At the time of writing, Multimedia Messaging Service, was a new technology that allowed cell phone users to send text, sound, pictures, and videos. "No doubt you've seen advertisements of MMS-capable phones, some of which are called camera phones." Because the technology is so new, SID is not yet able to collect SIGINT from MMS. But not for long. They're taking steps to build automated systems to spy on MMS.
Programs: DISHFIREThe Intercept ↗ (2017-04-24) -
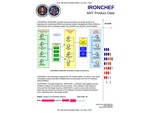
NSA ANT Catalog [pdf]
The NSA ANT catalog is a leaked confidential collection of sophisticated surveillance and hacking tools developed by the agency’s Tailored Access Operations unit (TAO), detailing hardware and software implants capable of covertly infiltrating computers, networks, and mobile devices. It revealed the NSA’s ability to conduct remote surveillance, implant malware, and maintain persistent access to targeted systems without users’ knowledge.
Programs: IRONCHEF · PROTOSS · STRONGMITE · GECKO II · STRAITBIZARRE · WAGONBED · UNITEDRAKE · DEITYBOUNCE · ARKSTREAM · TUNING FORK · GODSURGE · FLUXBABBITT · JETPLOW · BANANAGLEE · HALLUXWATER · TURBOPANDA · FEEDTROUGH · ZESTYLEAK · GOURMETTROUGH · SOUFFLETROUGH · HEADWATER · HAMMERMILL · HIT · SIERRAMONTANA · VALIDATOR · SCHOOLMONTANA · STUCCOMONTANA · CTX4000 · PHOTOANGLO · LOUDAUTO · ANGRYNEIGHBOR · NIGHTWATCHER · VIEWPLATE · LFS-2 · TAWDRYYARD · RAGEMASTER · CROSSBEAM · CHIMNEYPOOL · ROCKYKNOB · CANDYGRAM · CYCLONE Hx9 · TYPHON · EBSR · LANDSHARK · ENTOURAGE · HOLLOWPOINT · GALAXY · GENESIS · NEBULA · TYPHON HX · WATERWITCH · NIGHTSTAND · SPARROW II · BLINDDATE · DROPOUTJEEP · ARTEMIS · DROPMIRE · STRAITBIZZARE · FREEFLOW · TURBULENCE · GOPHERSET · MONKEYCALENDAR · TOTECHASER · TOTEGHOSTLY · PICASSO · TOTEGHOSTLY 2.0 · FRIEZERAMP · GENIE · VAGRANT · GOTHAM · SURLYSPAWN · GINSU · BULLDOZER · KONGUR · OMNIGAT · IRATEMONK · SERUM · SLICKERVICAR · RETURNSPRING · WISTFULTOLL · JIMSQ · SEAGULLFARO · SWAP · SNEAKERNET · TWISTEDKILT · HOWLERMONKEY · SUTURESAILOR · YELLOWPIN · CONJECTURE · SPECULATION · JUNIORMINT · MAESTRO · MAESTRO-II · SOMBERKNAVE · OLYMPUS · TRINITY · COTTONMOUTH-I · COTTONMOUTH-II · TURBINE · COTTONMOUTH-III · FIREWALK · DANDERSPRITZ -
Operational Engineering November 2010 [pdf]
This internal GCHQ briefing from late 2010 documents the Events Product Centre's suite of bulk internet and communications surveillance tools — including IMMINGLE, SALAMANCA, SOCIAL ANTHROPOID, MUTANT BROTH, KARMA POLICE, SAMUEL PEPYS and GUIDING LIGHT — covering scaling targets, new data sources, and operational capabilities across telephony, webmail, instant messaging, social media, GPRS and VoIP collection.
Programs: EVENTS · IMMINGLE · SALAMANCA · GUIDINGLIGHT · B3M · HARDASSOC · MAINWAY · THUGGEE · FASCIA · HAUSTORIUM · FIRESTORM · TERRAIN · SHAREOWN · ESCHAR · BRIO · INFINITEMONKEY · KARMAPOLICE · MARBLEDGECKO · MEMORYHOLE · MUTANTBROTH · SAMUELPEPYS · SOCIALANIMAL · SOCIALANTHROPOID · HEARTBEAT · SANTHROPOID · LEAKYGATEWAYS · GTPTUNNEL · LUSTRE · GLASSBACK · COLLATERAL · HRMAP · SWORDPLAY · BROADOAK · REFORMER · ARTEMIS · MERLOT · CONTRAOCTAVE · CRYINGFOWL · CULTWEAVE · SAMDYCE · GCQUERY · BLAZZINGSADDLES · EREPO · JTRIG · SOUNDER -
Phone Number Extractor [pdf]
A top secret XKEYSCORE training document from October 2009 describing the Phone Number Extractor capability, which automatically identifies and extracts telephone numbers from intercepted internet traffic including website content, email signature blocks, HTTP GET requests from mobile devices, HTTP POST submissions, and converged DNR/DNI collection — with operational examples targeting Iran, Lebanon, and Pakistan.
-
-
SOCIAL ANTHROPOID [pdf]
A SECRET STRAP1 GCHQ internal training and rollout presentation for SOCIAL ANTHROPOID — a new converged communications database replacing SALAMANCA, SOCIAL ANIMAL and HAUSTORIUM — demonstrating its query interface, data types, filtering capabilities and operational examples including telephony, webmail, instant messaging, BlackBerry, GPRS tunnels and leaky gateway events, with rollout planned across GCHQ analyst divisions in tranches during January-February 2011.
Programs: SOCIALANTHROPOID · SOCIALANIMAL · REFORMER · HAUSTORIUM · SALAMANCA · BROADOAK · DISCOVER · BLACKHOLE · HARDASSOCIATION · CHORDAL -
Stealthy Techniques Can Crack Some of SIGINT's Hardest Targets SIDtoday [pdf]
A SIDToday article from June 2010 describing TAO's supply chain interdiction operations — where shipments of network devices are covertly intercepted, implanted with beacon implants at a secret load station, and repackaged for delivery — illustrated by a specific operation against the Syrian Telecommunications Establishment whose implanted backbone devices unexpectedly provided access to Syria's previously unexploited GSM network, enabling automatic exfiltration of call detail records and voice content.
“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Greenwald, Glenn -
Tailored Access Operations 2007 [pdf]
This NSA document describes the Tailored Access Operations (TAO) division, which conducts sophisticated cyber operations to penetrate and maintain persistent access to target networks globally through both remote exploits and physical interdiction methods. The presentation outlines TAO's organizational structure, mission capabilities across telecommunications and data networks, development of hardware/software implants for devices ranging from servers to SCADA systems, collaboration with HUMINT partners for physical access operations, and specialized divisions focused on exploiting telephony systems, computer networks, and developing tools for computer network attack and exploitation.