Publication year: 2014 265 documents
Search documents matching “2014” →When a publisher first published each document. If a document is published multiple times, only the oldest one is used here.
Graphs
By document date (12 years)
By published date (4 years)
Sort: Title
Documents
-
NSA/GCHQ/CSEC Network Tradecraft Advancement Team [pdf]
The "NSA/GCHQ/CSEC Network Tradecraft Advancement Team (NTAT) 2010" document describes a collaborative mission between the US, UK, and Canada to synchronize and advance SIGINT techniques. The NTAT focused on "Network Analysis Tradecraft," specifically integrating analysis tools such as IRASCIABLE RABBIT and TOYGRIPPE into CSEC's OLYMPIA and developing standardized "use cases" for tracking mobile networks and virtual private networks (VPNs).
-
Offsensive Session: the Boundaries and Against Hacktivism [pdf]
GCHQ slides on “effects” operations against hacktivists: disruption in place of traditional law enforcement, denial-of-service attacks on key communications outlets during Op WEALTH in summer 2011, and a disruption playbook of infiltration, ruse, set-piece, false-flag, false-rescue, disruption and sting operations.
-
One-Year Anniversary for SUSLAG [pdf]
The document commemorates the one-year anniversary of the Special US Liaison Activity Germany (SUSLAG) at its new facility in Mangfall Kaserne, Bad Aibling, highlighting its transition from Bad Aibling Station. It discusses SUSLAG's ongoing role as a SIGINT liaison with the German intelligence service BND and showcases its collaborations, such as the Joint Analysis Center (JAC) and the Joint SIGINT Activity (JSA).
-
OPULENT PUP Encryption Attack [pdf]
"OPULENT PUP encryption attack (GCHQ)" is a 2009 technical planning document from the British intelligence agency GCHQ. It outlines a "proof-of-concept demonstrator" for a new capability to intercept and decrypt GSM communications protected by the A5/3 algorithm, requiring a complete overhaul of the existing processing chain used for the older A5/1 standard.
Programs: OPULENTPUP -
ORANGECRUSH, part of the OAKSTAR program [pdf]
An SSO item reporting that ORANGECRUSH — the OAKSTAR access at a third-party partner site in Poland, known to the Poles only as BUFFALOGREEN — began forwarding metadata to NSA on 3 March and content on 25 March, with collection shared to Second Parties through TICKETWINDOW.
-
OTR encrypted messages can't be decrypted by the NSA [pdf]
Three intercepted chat sessions from 16 March 2012 collected under PRISM, showing a target switching mid-conversation from unencrypted to OTR-encrypted messaging — with NSA able to collect the session metadata and unencrypted portions but unable to decrypt the OTR messages, each annotated "No decrypt available for this OTR encrypted message."
Programs: PRISM -
Partner Cables [pdf]
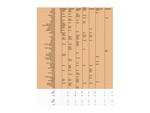
A classified table mapping which GCHQ cable interception programs had access to specific undersea fiber optic cables worldwide, revealing the codenames and access types — either Direct Cable Order or Indefeasible Right of Use/Landing Capacity — of seven surveillance programs across dozens of international cable systems, with Cable & Wireless (GERONTIC) providing access to the largest number.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
PGP encrypted email can't be decrypted by the NSA [pdf]
Two intercepted Yahoo email messages collected under FAA counterterrorism authority through PRISM (SIGAD US-984XN), both containing PGP-encrypted content that NSA was unable to decrypt — published by Der Spiegel as direct evidence that PGP encryption defeated NSA collection at the time of interception in January 2012.
Programs: PRISM -
POISONNUT [pdf]
NSA Wiki page describing POISONNUT — also known as the VPN Attack Orchestrator (VAO) — a LONGHAUL cryptologic exploitation service for IPSec VPN decryption that has existed in various forms since 2003, serving clients including TURMOIL, WEALTHYCLUSTER and the Transform Engine emulator via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: POISONNUT · TURMOIL · WEALTHYCLUSTER · ISLANDTRANSPORT · ISLANDHIDEAWAY · LONGHAUL · OAKLEY · SCARLETFEVER · PICARESQUE · VALIANTSURF -
PRISM (US-984XN) expanded its impact [pdf]
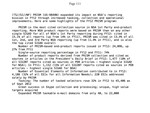
FY2012 figures for PRISM: 24,096 end-product reports (up 27 percent), the most-cited SIGAD in first-party reporting at 15.1 percent, 1,477 reports cited in the President's Daily Brief, tasked selectors up 32 percent to 45,406, and taskable e-mail domains expanded from 40 to 22,000.
Programs: PRISM -
PRISM Olympic Option [pdf]
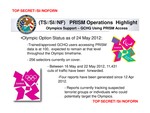
A May 2012 NSA operational highlight revealing that Britain's GCHQ was given access to the NSA's PRISM surveillance system during the London Olympics, with 100 trained British operatives secretly monitoring 256 targets and intercepting over 11,000 communications in a single week.
-
Private Networks are Important [pdf]
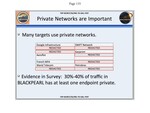
A slide arguing that many targets use private networks — Google's infrastructure, the SWIFT network, Gazprom, Aeroflot, the French foreign ministry, Warid Telecom and Petrobras — with a survey finding that 30 to 40 percent of BLACKPEARL traffic has at least one private endpoint.
Programs: BLACKPEARL -
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
PTC Glossary [pdf]
This GCWiki PTC Glossary excerpt defines SIGINT-related telecom terms—IMEI, IMSI, INMARSAT—and documents internal collection systems (e.g., INCENSER at Bude) and targeting notes (which identifiers are useful for targeting and which are not). It’s a technical reference for signals analysts describing selectors, collection sources, and operational caveats.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Quadrennial Intelligence Review Final Report, 2009 [pdf]
This 2009 strategic review from the Director of National Intelligence outlines potential future operating concepts for the US Intelligence Community, including "safe bets" like mass data analysis (Sentient Enterprise) and controversial "strategic hedges" such as using clandestine cyber operations to acquire proprietary technology from foreign corporations to benefit US industry (Technology Acquisition by All Means).
People: Shedd, David R. -
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
QUANTUMINSERT [pdf]
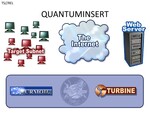
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
RAMPART-A Project Overview [pdf]
This document is a 2010 project overview of RAMPART-A, a highly unconventional NSA special access program dedicated to tapping high-capacity international fiber-optic cables at global "congestion points." Through clandestine bilateral partnerships, the NSA installs U.S. equipment on foreign soil to intercept massive volumes of transit data, providing the agency with a unique vantage point that covers virtually every country in the world.
Programs: RAMPART-A · RAMPART-T · SMOKYSINK · AZUREPHOENIX · SPINNERET · TRANQUIL · MOONLIGHTPATH · FIREBIRD · FALCONSTRIKE · DULCIMER · REDHARVEST · FLASHMARK · CONDORSPEAK · TURMOIL · SSO“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura · Jensen, Kristian -
RAMPART-A Sites [pdf]
This document specifies the data throughput and operational constraints of five key RAMPART-A interception sites, including the implementation of the "DNI Throttle" to manage data volume. It also defines the "Support Hub" model for managing signals tasking and explains the role of the REDHARVEST compartment in restricting which analysts can view specific digital network categories.
Programs: RAMPART-A · AZUREPHOENIX · MOONLIGHTPATH · SPINNERET · SMOKYSINK · FIREBIRD · XKEYSCORE · PINWALE · REDHARVEST · CADENCE“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura