Program: SSO 123 documents
Search documents matching “SSO” →Codenames and programs recorded for each document.
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
SSO news relevant entries [pdf]
This document provides updates on multiple operational advancements within the FAIRVIEW program under Special Source Operations (SSO).
Programs: SSO · FAIRVIEW · OVERHILL · EVILOLIVE · TURMOIL · FREEWAY · LEGIONJADE · NASSAUSHORE · PINECONE · ETML · VANGUARD · NETFLOW · FRIAR · MAINWAY · CLIFFSIDE · TWISTEDPATH · E-TML · COURIERSKILL · UTT · CADENCE · PINWALEPeople: Wertheimer, Michael“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “The Wiretap Rooms: The NSA’s Hidden Spy Hubs in Eight U.S. Cities” - The Intercept ↗ (2018-06-25) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan -
SSO Weekly Brief 25 April 2013: Excerpt [pdf]
This document highlights a PRISM FAA report from 10 April 2013, detailing U.S.-based Uzbek refugee Fazliddin Kurbanov’s communications with Adnan, an official from the Pakistan-based Islamic Movement of Uzbekistan (IMU). Kurbanov expressed his continued intention to attack the U.S., involving explosives and potentially raising money for the IMU, despite believing he was under surveillance by the FBI.
-
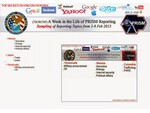
A Week in the Life of PRISM Reporting [pdf]
A slide from the "PRISM/US-984XN Overview" deck, showing different reporting topics from one week in the early February 2013.
“EUA espionaram milhões de e-mails e ligações de brasileiros” - O Globo ↗ (2013-07-12) · “NSA targets Indian politics, space & n-programmes” - The Hindu ↗ (2013-09-24) · Greenwald, Glenn · Kaz, Roberto · Casado, José · Saxena, Shobhan -
Analysts: A New Tool for Researching Telecommunications Infrastructure is Now Available SIDtoday [pdf]
QUARRYGEM is an application created by the Environmental Analysis Branch to give analysts and other users enhanced access to NSA's data on telecommunications infrastructure systems. It currently only contains data on undersea cable systems but was designed to handle other telecommunications infrastructure data, potentially including satellite, microwave and terrestrial data sources.
The Intercept ↗ (2019-05-29) -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA presentation examines metadata attribution challenges arising when active TAO implants exfiltrate traffic through passive TURMOIL collection infrastructure, creating conflicts where intercepted data carries dual classification markings, case notations, and legal authorities from both collection systems. The briefing highlights how existing databases and analytic tools were not designed to handle traffic with two simultaneous sets of metadata parameters, requiring enterprise-wide solutions to consistently attribute and track actively-shaped intelligence collection.
Programs: BRAVENICKEL · HAMMERMILL · APEX · MARINA · TURMOIL · PRESSUREWAVE · METROTUBE · TOYGRIPPE · HAMMERSTEIN · HAMMERSTONE · METAWAVE · TURBULENCE · SSO -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA briefing addresses the technical and administrative friction caused by "shaping" operations. Shaping occurs when an active malware implant, typically situated on network infrastructure like a router, copies specific data streams and redirects them past a passive surveillance sensor such as TURMOIL. While this ensures the capture of data that might otherwise be missed, it creates a "double metadata" conflict where a single piece of intelligence carries two competing sets of identifiers: one from the active Tailored Access Operations (TAO) implant and another from the passive collection site. The document tasks analysts with finding a way to reconcile these source notations to ensure the data remains searchable and legally compliant within legacy databases.
Programs: BRAVENICKEL · HAMMERMILL · APEX · TURMOIL · HAMMERSTONE · PRESSUREWAVE · METROTUBE · TOYGRIPPE · TURBULENCE · METAWAVE · MARINA · SSO · CONVEYANCE · NUCLEON · FASCIA · HAMMERCHANT -
Analyzing Mobile/Cellular DNI in XKEYSCORE, May 2009 [pdf]
The XKEYSCORE document explains how the agency analyzes mobile/cellular device internet usage by collecting and processing both converged DNI/DNR data within cellular networks and traditional internet traffic, using various tools and indicators to identify mobile users even when their device type isn't immediately evident. The document demonstrates how the system can track mobile internet activity across applications like Yahoo Mail and identifies devices through various technical "hints" including MSISDN codes, browser fingerprints, and user agent strings.
-
Another Successful Olympics Story SIDtoday [pdf]
SID spent more than a year planning for the 2004 Summer Olympics in Athens, collaborating across different areas of SID and with other intelligence agencies to gain access to communications systems and providers in Greece.
“A Death in Athens” - The Intercept ↗ (2015-09-28) · “Americans and Greeks started the 2004 wiretaps together” - Kathimerini ↗ (2015-09-29) · The Intercept ↗ (2017-04-24) · Bamford, James · Petropoulos, Aggelos -
Attention, SIGINT Analysts: E.O. 12333 Transit Communications -- What Are They? SIDtoday [pdf]
This SIDtoday article clarifies the difference between NSA's longstanding authority to collect "transit communications" and FISA Amendment Act (FAA) Section 702 authorizations. The Office of Special Source Operations (SSO) manages these transit communications under various programs like US-990, US-983, and US-3273.
Programs: SSO -
Black Budget: Special Source Access - Foreign Partner Access [pdf]
This document provides a detailed financial and operational breakdown from the NSA’s FY 2013 Congressional Budget Justification for the SSO's Foreign Partner Access project. It outlines the strategic funding for the RAMPART-A and WINDSTOP programs, which leverage international partnerships to intercept massive volumes of global communications traffic from long-haul fiber-optic cables and integrated 2nd Party architectures.
“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura · Jensen, Kristian -
BLARNEY Exploits the Social Network via Expanded Facebook Collection [pdf]
An SSO highlight of 14 March 2011 announcing substantially expanded Facebook collection under FISA and FAA authorities — chat, private messages, profile information, subscriber videos and geolocation from IP addresses — built with the FBI over six months, with PRINTAURA writing the new software.
-
BLARNEY program overview [pdf]
The document is an NSA Special Source Operations (SSO) portal page screenshot for the BLARNEY program, describing it as a top-secret collection initiative established in the 1970s that leverages government and commercial partnerships to intercept foreign intelligence under FISA authority. It highlights BLARNEY’s major intelligence value—contributing heavily to counterterrorism reporting and the President’s Daily Brief—and lists its primary targets as diplomatic, economic, foreign government, and counterterrorism communications.
-
BLARNEY site book [pdf]
2011 BLARNEY Program TDY Handbook outlining procedures for NSA personnel traveling in support of the program, including cover protocols, required training, site visit guidelines (e.g., FBI HQ, Quantico, Titan Pointe), and rules for transporting classified materials. It emphasizes the use of cover stories, special vehicles, and strict coordination with program directors to maintain operational security.
-
BOUNDLESSINFORMANT – Frequently Asked Questions [pdf]
This document outlines the NSA’s internal metadata analysis tool, designed to provide real-time visualizations and statistics on global SIGINT collection by country, organization, and site. It explains the tool’s purpose, data sources, technical architecture, views, data limitations, and the process for requesting feature enhancements, highlighting its role in cataloging surveillance activity without human intervention.
Programs: BOUNDLESSINFORMANT · ASDF · GAO · RAMPART-A · SPINNERET · GM-PLACE · FALLOUT · TUSKATTIRE · FASCIA · MUSCULAR · Terrestrial RF · MachineShop · TurkeyTower · CloudBase · GXT · ExtGWT · JUGGERNAUT · LOPER · FLAWMILL · SSO · MAPREDUCE“Boundless Informant: the NSA's secret tool to track global surveillance data” - The Guardian ↗ (2013-06-08) · “NSA-files repeatedly show collection of data «against countries» - not «from»” - Dagbladet ↗ (2013-11-22) · “New NSA Revelations: Inside Snowden's Germany File” - Der Spiegel ↗ (2014-06-18) · Greenwald, Glenn · MacAskill, Ewen · Becker, Sven · Gude, Hubert · Horchert, Judith · Müller-Maguhn, Andy · Poitras, Laura · Reißmann, Ole · Rosenbach, Marcel · Schindler, Jörg · Schmid, Fidelius · Sontheimer, Michael · Stark, Holger -
Bulk collection of webmail address books and emerging protocols [pdf]
TOP SECRET NSA document details the large-scale collection of email address books and contact lists from major webmail and social media providers, emphasizing their metadata value despite low attribution rates to known targets. It also highlights ongoing efforts to identify and analyze emerging communication protocols, such as those used by Hotmail Messenger.
-
CASCADE - Joint Cyber Sensor Architecture [pdf]
This presentation outlines the Communications Security Establishment’s (CSE) plans to unify and expand its cyber sensor networks (ITS and SIGINT) to create a comprehensive, multi-layered national cyber defense system, enabling threat detection, intelligence collection, and defensive operations across Canadian and foreign networks. It emphasizes standardizing sensor deployments, integrating analytic capabilities, and preparing for “Effects” operations to mitigate cyber threats by 2015. The presentation is duplicated from page 33 onwards - three slides of the duplicated slides have internal CSE comments.
Programs: CASCADE · PHOTONICPRISM · EONBLUE · INDUCTION · THIRDEYE · CRUCIBLE · CHOKEPOINT · SUNWHEEL · CASSIOPEIA · SCNET · JAZZFLUTE · GAZEBO · SEEDSPHERE · TEXPRO · SSO -
Collection Accesses 30 Nov - 06 Dec 2009 [pdf]
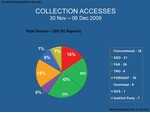
This National Security Agency chart shows the varied sources of 103 “accesses” to communications or computers collected in a single week in 2009 at the N.S.A.’s big station in San Antonio, Texas.
Programs: SSO -
Content Acquisition Optimization PowerPoint Slides [pdf]
An NSA presentation on content acquisition optimisation — describing how incidental bulk collection from Yahoo Webmessenger, email address books, buddy lists and webmail inboxes was generating massive unintended collection volumes.
-
CSEC Cyber Threat Capabilities [pdf]
This document details CSEC’s full-spectrum cyber operations architecture, integrating SIGINT and IT Security to conduct both defensive and offensive activities under the guise of “information superiority.” While early sections emphasize detection, anomaly analysis, and collaboration with Five Eyes partners, later portions reveal active measures including network infiltration (implant deployment), command-and-control tracking, traffic manipulation and redirection, DNS interference, and potential disruption or deception operations—illustrating CSEC’s capacity not only to defend Canadian networks but also to surveil, exploit, and influence foreign and domestic digital infrastructure.
Programs: EONBLUE · CYBERDMZ · SEEDSPHERE · PHOTONICPRISM · SPECIALSOURCE · SUPERDRAKE · DARKSPACE · QUANTUM · MANDATE · STREAMING SENTRY · SSO · TKB · COVENANT -
CSEC SIGINT Cyber Discovery: Summary of the current effort [pdf]
This document provides a overview of the Communications Security Establishment Canada (CSEC) cyber operations, detailing its SIGINT, CNE (Computer Network Exploitation), and cyber counterintelligence programs, including tools like WARRIORPRIDE, REPLICANTFARM, and EONBLUE for threat detection, anomaly discovery, and metadata production. It outlines operational procedures, analytic methodologies, and collaborative frameworks with domestic and Five Eyes partners for sharing intelligence, tipping/cueing, and integrating cyber and traditional counterintelligence efforts.
Programs: REPLICANTFARM · SLIPSTREAM · WARRIORPRIDE · DAREDEVIL · CHORDFLIER · NAMEDROPPER · WORMWOOD · OBELIX · SHEPHERD · CARBON · REGBACKUP · DOGHOUSE · WALKER · ALOOFNESS · BLAZINGANGEL · TINYWEB · QUIVERINGSQUAB · WINDO · DIESELRATTLE · WIDOWKEY · CIVETCAT · WINBEE · SSLINST · PULLEDPORK · EONBLUE · SNIFFLE · QUANTUM · XKEYSCORE · HALTERHITCH · FASTFLUX · DEADSEA · NSPACES · PPF · SSO · TKB“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan