Dissemination control: REL TO USA, FVEY 107 documents
Search documents matching “REL TO USA, FVEY” →Handling controls assessed for each document, as component values. If a document contains multiple disseminations, the most restrictive is used here.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
GCSB Update - 22 April 2010 [pdf]
This GCSB briefing from April 2010 provides an internal update on the operational status and development pathway for the Waihopai satellite surveillance station (codenamed IRONSAND). It reports near-perfect system availability statistics for numerous NSA/GCSB systems like LEGALREPTILE and JUGGERNAUT, details collaboration on virtualization and collection initiatives, and notes consequences arising from external court decisions.
Programs: IRONSAND · CALIX · COMMONGROUND · DUALTIRE · FLUTE · FRESNELEFFECT · JACKHAMMER · JUGGERNAUT · KILOMISER · KRAUSS · LATENTHEAT · LEGALREPTILE · LOPERS · MOONSCAPE · SEMITONE · SSA · STONEGATE · SURFBOARD · VENUSAFFECT · VINEYARD · VINTAGE · WEALTHYCLUSTER · VQUEST · TORUS · SHAREDQUEST -
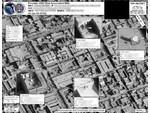
GHOSTHUNTER aerial image (2009) [pdf]
This imagery showcases a real-world application of the GHOSTHUNTER program operated out of Menwith Hill Station in the UK. The document features an aerial satellite photograph used to pinpoint the precise physical location of VSAT (Very Small Aperture Terminal) satellite dishes. By linking a target's digital footprint—specifically their MAC address and IP address—to a specific set of geographic coordinates, the NSA and GCHQ can identify the exact building or compound where a person is using the internet. This capability is a cornerstone of the "find, fix, finish" cycle used to support "covert operations" and targeted killing missions in conflict zones like Yemen, Somalia, and Afghanistan.
Programs: GHOSTHUNTER -
GSM tower mapping made easier and more accurate with new tool SIDtoday [pdf]
This document details DYMO, a prototype developed at the NSA’s Menwith Hill Station—the agency’s large British base operated in close cooperation with GCHQ—for highly accurate GSM tower geolocation. It highlights DYMO’s superior performance in mapping accuracy and metadata integrity, its extensive operational use across regions such as Iraq, Iran, and Somalia, and its integration with tools like GOLDENEYE and the Integrated COMINT System (ICS) to streamline analysis and intelligence fusion.
-
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
HOMING PIGEON [pdf]
Slides on a query-focused dataset that would correlate GSM handsets seen on two or more aircraft flights with their subscribers.
“US and Britain refine their ability to tap into airline passenger’s mobile phones while they are in the air” - Le Monde ↗ (2016-12-07) · “American and British Spy Agencies Targeted In-Flight Mobile Phone Use” - The Intercept ↗ (2016-12-07) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Follorou, Jacques · Greenwald, Glenn -
How do we do SIGDEV or private networks? [pdf]
Top Secret SIGINT Development (SIGDEV) briefing explains how analysts conduct reconnaissance on private networks, noting that many targets rely on them and that 30–40% of traffic surveyed in BLACKPEARL has at least one private endpoint. It demonstrates the ROYALNET tool and its analytics for identifying network features, NetStrings, and links likely to carry a target’s traffic, with named targets and feature sets including Google’s infrastructure, the SWIFT banking network, the French Ministry of Foreign Affairs, Brazil’s Petrobras, and Huawei.
People: Higgins, Jean -
How the NSA Accesses Smartphone Data [pdf]
This document reveals how the NSA and its Five Eyes partners developed sophisticated methods to exploit iPhone location services and BlackBerry communications, framing smartphone users as “zombies” willingly sharing data. It includes examples of intercepted geolocation data and decrypted BlackBerry emails, illustrating targeted surveillance capabilities against both consumer and government communications.
-
I hunt sys admins [pdf]
These internal documents outline the NSA’s strategy for identifying and targeting foreign system administrators to gain "keys to the kingdom" access to global network infrastructure. By correlating disparate datasets—such as passive telnet/SSH metadata and personal social media/webmail logins—the agency identifies personal accounts to facilitate QUANTUM-based hacking operations and network "pwnage."
-
ICREACH Black Budget Extracts [pdf]
This document provides fiscal and strategic justifications for the continued expansion of ICREACH, detailing its role as a primary vehicle for disseminating both telephony and Digital Network Intelligence (DNI) metadata across the Intelligence Community. It outlines the platform's transition to the NSA/CSS cloud architecture, a move intended to enhance data enrichment services and ensure the system remains responsive to the evolving requirements of the National Intelligence Priorities Framework (NIPF).
Programs: ICREACH -
In-Flight GSM [pdf]
This NSA presentation outlines how the agency is reacting to the growth of mobile phone services on board commercial aircraft.
-
India: Support to Terrorist Attacks in Mumbai [pdf]
A top secret NSA intelligence report on GCHQ's surveillance of Lashkar-e-Taiba technology chief Zarrar Shah before and during the November 2008 Mumbai attacks, documenting how analysis of his internet browsing and viewing habits revealed reconnaissance activity and operational planning against Mumbai targets including the Taj Hotel.
People: Shah, Zarrar“In 2008 Mumbai Attacks, Piles of Spy Data, but an Uncompleted Puzzle” - The New York Times ↗ (2014-12-21) · “In 2008 Mumbai Attacks, Piles of Spy Data, But an Uncompleted Puzzle” - ProPublica ↗ (2014-12-21) · “In 2008 Mumbai Attacks, Piles of Spy Data, but an Uncompleted Puzzle” - PBS ↗ (2014-12-21) · Glanz, James · Rotella, Sebastian · Sanger, David E. · Jennings, Tom · Peevey, Anna Belle · Nieling, Michael -
Industrial-Scale Exploitation [pdf]
This top-secret NSA document details the operational philosophy behind the TURBINE system's transition to "industrial-scale exploitation." By integrating with both active and passive sensors, TURBINE automates the delivery of malware and the maintenance of network implants, specifically targeting routers and server-side code execution.
-
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
IR.21 – A Technology Warning Mechanism [pdf]
This 2010 TOP SECRET NSA briefing defines the IR.21 roaming document as a critical tool for "horizon scanning" and "forecasting" global telecommunications shifts. The document outlines how the NSA uses these technical files to proactively identify emerging 3G and 4G technologies, pinpointing vulnerabilities for exploitation before new systems are even fully deployed.
-
Is It the End of the SIGINT World as We Have Come to Know It? [pdf]
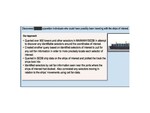
Two excerpts from a 2012 NSA presentation titled "Is It the End of the SIGINT World as We Have Come to Know It?" prepared by a member of the Large-Access Exploitation Group. The table excerpt lists MAINWAY among the systems at highest risk of being overwhelmed by the volume of data the agency was ingesting. The diagram excerpt shows MAINWAY feeding into the Graph-in-Memory (alongside WESTERNSTAR), illustrating how MAINWAY's continuous contact-chaining pushed its precomputed results into the in-memory graph database that analysts actually queried.
Programs: FALLOUT · METADNI · MARINA · MAINWAY · FASCIA · GMHALO · DPS · EKS · WESTERNSTAR · GRAPH-IN-MEMORY -
Is there "fifth party" collection? [pdf]
This NSA internal Q&A forum discussion reveals "fifth party collection"—where the NSA passively intercepts data from one intelligence service (South Korea) that has compromised another service's (North Korea) computer network exploitation operations, creating a three-layer chain where NSA exploits Actor One's access to Actor Two's CNE activities against shared targets. The thread provides concrete examples including NSA leveraging South Korean implants on North Korean officials' computers (who themselves were conducting CNE operations) and stealing zero-day exploits from unidentified foreign intelligence services by passively monitoring their successful attacks.
-
Japan provided with XKEYSCORE [pdf]
This document outlines a request for approval to provide training to the Japanese Directorate for SIGINT (DFS) on using advanced SIGINT systems, including XKEYSCORE, to enhance Japan's cyber network defense capabilities. This training, scheduled for April 2013, aligns with U.S. strategic goals to bolster the cyber defense abilities of allied nations, highlighting ongoing NSA collaboration with Japan on surveillance and cybersecurity.
“Japan Made Secret Deals With the NSA That Expanded Global Surveillance” - The Intercept ↗ (2017-04-24) · “アメリカに監視される日本 ~スノーデン“未公開ファイル”の衝撃” - NHK ↗ (2017-04-24) · Gallagher, Ryan · Ikegami, Akira -
Location Cookies [pdf]
These slides contain excerpts from an April 2013 National Security Agency presentation detailing signal surveillance techniques and successes. They reveal that the NSA and its British counterpart, Government Communications Headquarters (GCHQ), use a Google-specific tracking cookie to pinpoint targets for hacking.
-
LONGHAUL [pdf]
An NSA WikiInfo page for LONGHAUL — the centralised end-to-end attack orchestration and key recovery service that sits at the heart of NSA's capability to break encrypted internet traffic, receiving cryptanalytic data from field collection systems, coordinating attacks against VPN and SSL/TLS encryption through child projects POISONNUT and SCARLETFEVER, and returning recovered keys to deployed CA Servers at collection sites worldwide.
Programs: LONGHAUL · MAILORDER · CASPORT · GECC · VIVIDDREAM · TURMOIL · WEALTHYCLUSTER · TUTELAGE · EINSTEIN · ISLANDTRANSPORT · HADOOP · NINJACOVE · JST · CST · VMM · VDG · ORDC · SCB · ISLANDHIDEAWAY · TURBULENCE · POISONNUT · SCARLETFEVER · HEROICSAND · PLATINUMRING · GALLANTWAVE · JEDIMINDTRICK · CHAOTICSTORMTROOPER · CORALREEF · SCUBADIVER2 · TERRACOTTA · HBASE · SCALA · MAPREDUCE · COALCAR · STOCKCAR · BEACHHEAD · MIDRIFT · WOLVERINESTAKE · NSP · PURGE · SURGE · C2DP · DOORS · HUDSON