Dissemination control: REL TO USA, FVEY 107 documents
Search documents matching “REL TO USA, FVEY” →Handling controls assessed for each document, as component values. If a document contains multiple disseminations, the most restrictive is used here.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Afghanistan Coalition Dissemination Brief to Senior Leadership Forum [pdf]
This document ooutlines the structure, goals, and challenges of multinational signals intelligence (SIGINT) collaboration in Afghanistan as of 2009. It reveals how the U.S. and its intelligence-sharing allies (notably the 5 Eyes, 9 Eyes, and 14 Eyes) coordinated SIGINT collection, decryption, analysis, and dissemination across NATO and coalition forces.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
"Anarchist" Image Index [pdf]
Images collected through ANARCHIST, the GCHQ covername for a joint GCHQ/NSA SIGINT collection site on Mt. Troodos, Cyprus, drawn from imagery and pages in GCHQ's internal GCWiki.
Programs: ANARCHIST -
AURORAGOLD – Target Technology Trends Center support to WPMO [pdf]
This briefing details the technical architecture and data pipeline used to process global cellular network information. It specifically highlights the synergy between data gathering on GSM/UMTS networks and the implementation of "Auto-Minimization" to ensure the resulting SIGINT reporting complies with NSA legal and policy requirements.
-
AZTECTOMB32 DMW Install and ESH Package [pdf]
This document is a top-secret NSA internal project log detailing restrictions on installing new implants on machines running Kaspersky 2010+ due to the software’s cloud functionality, which prevents safe deployment of NSA malware. It records the suspension and eventual closure of a project (AZTECTOMB32/DEMENTIAWHEEL) that would have targeted such systems.
-
Bad guys are everywhere, good guys are somewhere! [pdf]
A classified NSA NTOC presentation describing TREASURE MAP — the agency's near real-time global internet mapping platform — which combines open source, commercial, covert, and SIGINT data to chart every device, router, and autonomous system on the internet, including through 13 covert servers secretly planted in unwitting data centers across 18 countries spanning Asia, Europe, Russia, Africa, and South America, with networks marked in red indicating active SIGINT collection access points across at least 20 major telecommunications providers on three continents including allied nations' state-owned carriers.
Programs: TREASUREMAP · PACKAGEDGOODS · SOCIALSTAMP · SEASIDEFERRY · ARK · CAIDA · RUSTICBAGGAGE · PACKAGEDGOODS-GTR · PACKAGEDGOODS-SERVER · BLACKPEARL · LEAKYFAUCET · HYDROCASTLE · MASTERSHAKE · S-TRICKLER · TOYGRIPPE · DISCOROUTE · VITALAIR2 · IPGEOTRAP · JOLLYROGER · TUTELAGE · BYZANTINEHADES · XKEYSCORE · RADIUS · TACACS -
BLARNEY report April 2013 [pdf]
This NSA document describes the deployment of surveillance systems (RINGBILL, TURTLEPOWER, SKIDROWE) at "TITAN POINTE" to process bulk communications data including VoIP and video teleconferencing traffic. The systems are designed to intercept, filter, and analyze high-volume network traffic using legacy architecture initially, with plans to transfer to newer processing solutions for long-term mass surveillance capabilities.
Programs: BLARNEY · RINGBILL · WEALTHYCLUSTER2 · XKEYSCORE · TRIREME · SKIDROWE · PINWALE · TITANPOINTE · VISIONQUEST · TURTLEPOWER · SKINNY -
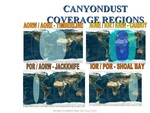
Canyondust coverage regions [pdf]
This document describes NSA's capabilities for exploiting commercial satellite communications (VSAT), including systems from Hughes, ViaSat, iDirect, and others. It details programs such as FALLOWHAUNT and CORRALCLOUD for targeting and analyzing satellite communications technologies, including TDMA and PCMA systems.
Programs: CANYONDUST · TIMBERLINE · CARBOY · JACKKNIFE · SHOAL BAY · FALLOWHAUNT · CORRALCLOUD · DOUBLETALK -
Chinese Exfiltrate Sensitive Military Technology [pdf]
This TOP SECRET NSA SIGINT development briefing describes large-scale Chinese cyber espionage that exfiltrated sensitive U.S. military technologies and inflicted extensive operational, financial, and strategic damage on Department of Defense systems. The document emphasizes both the scale of losses and the role of SIGINT in detecting, understanding, and mitigating adversary malware.
Programs: BYZANTINEHADES -
CISCO bug [pdf]
An engineering change proposal dated 11 April 2013 to update the software on every Cisco ONS optical switch at the corporate access sites — APPLE1, CLEVERDEVICE, HOMEMAKER, DOGHUT, QUARTERPOUNDER, QUEENSLAND, SCALLION, SPORTCOAT, SUBSTRATUM, TITANPOINTE, BIRCHWOOD, MAYTAG, EAGLE and EDEN — after a bug that makes the multiplexers intermittently drop out, with the mission impact recorded as unknown.
Programs: CLEVERDEVICE · HOMEMAKER · DOGHUT · APPLE1 · QUARTERPOUNDER · QUEENSLAND · SCALLION · SPORTCOAT · SUBSTRATUM · TITANPOINTE · BIRCHWOOD · MAYTAG · EAGLE · EDEN · BLARNEY · FAIRVIEW · OAKSTAR · STORMBREW -
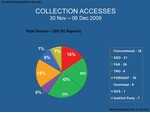
Collection Accesses 30 Nov - 06 Dec 2009 [pdf]
This National Security Agency chart shows the varied sources of 103 “accesses” to communications or computers collected in a single week in 2009 at the N.S.A.’s big station in San Antonio, Texas.
Programs: SSO -
Computer Network Exploitation (CNE) Classification Guide / 2-59 [pdf]
A NSA/TAO classification guide establishing the precise classification level for 41 categories of information about computer network exploitation operations — covering remote and physical subversion methods, CNE tools and techniques, supply chain operations, hardware implants, off-net field operations, zero-day vulnerabilities, and cryptographic material acquired through CNE.
“Core Secrets: NSA Saboteurs in China and Germany” - The Intercept ↗ (2014-10-10) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Maass, Peter · Poitras, Laura · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
Content Extraction Enhancements For Target Analytics: SMS Text Messages: A Goldmine to Exploit (9 June 2011) [pdf]
The document describes the NSA’s Dishfire program, which collects hundreds of millions of global SMS messages daily, and the PREFER system, which extracts detailed metadata—including contacts, geolocation, travel, and financial information—from these messages for analytic purposes. It highlights the scale, operational processes, and types of data exploited to support intelligence and target analysis.
-
Converged Analysis of Smartphone Devices [pdf]
This 2010 document outlines NSA methods for identifying, processing, and exploiting data from smartphones by targeting both telephony and digital network intelligence (DNI). It details how analysts use tools like XKEYSCORE and metadata extraction to collect geolocation, app data, call logs, unique identifiers, and user activity from popular mobile apps and services (e.g., Google Maps, Facebook, Flickr), emphasizing the intelligence potential of smartphones as rich surveillance targets.
People: Kuruc, Paula -
-
Discovery SIGINT Targeting Scenarios and Compliance [pdf]
This document is a top-secret NSA guidance manual detailing SIGINT targeting scenarios, compliance procedures, and legal guidance for querying foreign actors, malware, and potentially U.S.-linked systems, including considerations for minimizing incidental collection of U.S. persons’ communications. It outlines specific rules, approvals, and exceptions for using SIGINT tools, foreign intelligence tasks, and cases involving ambiguous or dual-use selectors like WikiLeaks, The Pirate Bay, and foreign actors operating through U.S. infrastructure.
-
DoD 2011 Strategy for Operating in Cyberspace – Supply Chain Excerpts [pdf]
The classified 2011 Department of Defense strategy warns that U.S. reliance on foreign manufacturing—especially from countries like China—creates major cybersecurity risks, including the potential insertion of malicious hardware or software into critical systems. It outlines a government-wide plan to mitigate these supply chain vulnerabilities through coordinated policies, risk management strategies, and collaboration with industry.
-
Exploiting Foreign Lawful Intercept (LI) Roundtable [pdf]
Top-secret PowerPoint presentation, "Exploiting Foreign Lawful Intercept Roundtable," highlights the agency’s strategy to exploit vulnerabilities in lawful intercept systems from telecom companies, such as Ericsson, Motorola, and Nokia, in countries like Mexico, Indonesia, and Egypt. The presentation also discusses NSA's use of various "Fingerprints" for identifying data and its collaboration with industry players and foreign lawful intercept systems.
“A Death in Athens” - The Intercept ↗ (2015-09-28) · “Americans and Greeks started the 2004 wiretaps together” - Kathimerini ↗ (2015-09-29) · Bamford, James · Petropoulos, Aggelos -
FASCIA: The NSA's huge trove of location records [pdf]
FASCIA is the National Security Agency's enormous database containing trillions of metadata records, many with device locations, that are collected from a variety of sources. This document shows the volume and types of device-location data collected by the agency.
“NSA tracking cellphone locations worldwide, Snowden documents show” - The Washington Post ↗ (2013-12-04) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Gellman, Barton · Soltani, Ashkan · Greenwald, Glenn -
Ferguson NSA Visit Précis [pdf]
This internal NSA "Visit Précis" from March 2013 details a high-level courtesy call between Ambassador Roy Ferguson of New Zealand and the Director of the NSA. The meeting's primary objective was to discuss proposed legislative changes to New Zealand’s intelligence community, focusing on increased oversight in the wake of public controversies.
Programs: FIRSTLIGHTPeople: Ferguson, Roy · Cusick, James M. · Inglis, Chris · Fleisch, Fran · Kagan, Edgard · Wolfenson, Hugh · Dotcom, Kim · Alexander, Keith B. -
FORNSAT technologies [pdf]
This document outlines a Foreign Satellite Communication Exploitation Model targeting satellite systems such as Intelsat, Iridium, Hughes, ND SatCom, and Inmarsat, using both fixed and mobile satellite services. It describes specific collection and geolocation systems—SEADIVER, ZODIACARRAY, and CANYONDUST—that capture and process voice, fax, data, and terminal location information across global coverage areas.
Programs: SHAREDVISION · DARKQUEST · EKB · GLOBALVIEW · TRYST · ZODIACARRAY · CANYONDUST · IRIDIUM · SEADIVER