Classification: TOP SECRET 823 documents
Search documents matching “TOP SECRET” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (14 years)
By published date (9 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
PGP encrypted email can't be decrypted by the NSA [pdf]
Two intercepted Yahoo email messages collected under FAA counterterrorism authority through PRISM (SIGAD US-984XN), both containing PGP-encrypted content that NSA was unable to decrypt — published by Der Spiegel as direct evidence that PGP encryption defeated NSA collection at the time of interception in January 2012.
Programs: PRISM -
PHANTOM PARROT [pdf]
This document discusses PHANTOM PARROT, a GTAC tool used for querying mobile phone data collected from individuals stopped at UK ports as part of the ITT Op WILDWAY initiative. The tool allows intelligence analysts to access phonebook, SMS, and call log data from these stops, which can be used for counter-terrorism efforts. Data is obtained under the Terrorism Act 2000, and the tool is part of a broader intelligence-gathering effort, eventually to be integrated into the LUCKY STRIKE project.
Programs: PHANTOM PARROT · WILDWAY · RANNOCH MOOR · LUCKY STRIKE · LOOKING GLASS · DISHFIRE · CORINTH · MOONRAKER · RUSSETT -
Phone Number Extractor [pdf]
A top secret XKEYSCORE training document from October 2009 describing the Phone Number Extractor capability, which automatically identifies and extracts telephone numbers from intercepted internet traffic including website content, email signature blocks, HTTP GET requests from mobile devices, HTTP POST submissions, and converged DNR/DNI collection — with operational examples targeting Iran, Lebanon, and Pakistan.
-
PINWALE: Transnational DNI Training [pdf]
This presentation is a classified NSA training guide on PINWALE, a SIGINT database used for the storage, retrieval, and analysis of intercepted digital network intelligence (DNI) communications. It outlines system capabilities, query creation, search tools, and interfaces such as NEXUS, UIS, and AGILITY, explaining how analysts search, retrieve, and analyze both content and metadata — including FISA-partitioned data — within the Five Eyes intelligence framework.
-
POISONNUT [pdf]
NSA Wiki page describing POISONNUT — also known as the VPN Attack Orchestrator (VAO) — a LONGHAUL cryptologic exploitation service for IPSec VPN decryption that has existed in various forms since 2003, serving clients including TURMOIL, WEALTHYCLUSTER and the Transform Engine emulator via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: POISONNUT · TURMOIL · WEALTHYCLUSTER · ISLANDTRANSPORT · ISLANDHIDEAWAY · LONGHAUL · OAKLEY · SCARLETFEVER · PICARESQUE · VALIANTSURF -
Post-war Iraq Plan SIDtoday [pdf]
Planning underway for post-war changes and challenges in April 2003.
The Intercept ↗ (2016-05-16) -
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
Presentation on the spying program PRISM and ECC's participation [pdf]
This presentation provides statistics on the PRISM surveillance program, detailing intelligence reporting and target tasking across various NSA units and partners from 2011 to 2013. The data reveals that while not the top producer by volume, the European Cryptologic Center (ECC) was the most proportionally reliant on PRISM, which constituted over half of its intelligence output.
-
Presidential Policy Directive/PPD-20 [pdf]
Eighteen-page presidential memo reveals how Barack Obama has ordered intelligence officials to draw up a list of potential overseas targets for US cyber attacks.
-
PRESTON Study [pdf]
This GCHQ document details the PRESTON surveillance program, revealing that over a six-month period, 97% of intercepted communications—including calls, texts, and internet data—were not viewed by analysts despite being fully warranted, highlighting systemic challenges in processing and exploiting the vast volume of collected intelligence. It underscores the reliance on traditional PRESTON sources for events like the London G20, while noting gaps in data feeds from other repositories, reflecting both operational scale and limitations in effective oversight.
-
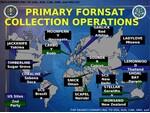
PRIMARY FORNSAT COLLECTION OPERATIONS [pdf]
This document is a TOP SECRET NSA/CSS slide mapping the global locations of primary FORNSAT (foreign satellite) collection operations, showing U.S. and second-party ground stations used to intercept satellite communications worldwide. It illustrates the geographic spread and allied integration of NSA satellite surveillance infrastructure rather than specific technical capabilities.
-
PRISM (US-984XN) expanded its impact [pdf]
FY2012 figures for PRISM: 24,096 end-product reports (up 27 percent), the most-cited SIGAD in first-party reporting at 15.1 percent, 1,477 reports cited in the President's Daily Brief, tasked selectors up 32 percent to 45,406, and taskable e-mail domains expanded from 40 to 22,000.
Programs: PRISM -
PRISM Olympic Option [pdf]
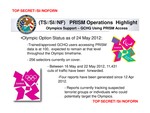
A May 2012 NSA operational highlight revealing that Britain's GCHQ was given access to the NSA's PRISM surveillance system during the London Olympics, with 100 trained British operatives secretly monitoring 256 targets and intercepting over 11,000 communications in a single week.
-
PRISM planning slide (PRISM briefing 1) [pdf]
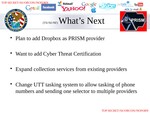
A PRISM slide headed 'What's Next': plans to add Dropbox as a PRISM provider, add a cyber threat certification, expand collection from existing providers, and change the UTT tasking system to allow phone-number tasking.
-
PRISM tasking slide (PRISM briefing 2) [pdf]
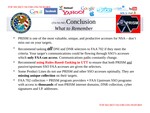
A PRISM slide headed 'Conclusion: What to Remember'. It says PRISM is among the most valuable NSA accesses, recommends tasking all DNI and DNR selectors to FAA 702 where they meet the criteria, and recommends Rules-Based Tasking in UTT so that PRISM and upstream SSO accesses both get the selectors.
-
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
PRISM/US-984XN Overview [pdf]
Blurry screengrabs from the "PRISM/US-984XN Overview" slide deck shown on the Fantástico O Globo broadcast. This document contains slides that are not incldued in the slides published by The Washington Post, The Guardian, Le Monde, and others.
-
Private Networks are Important [pdf]
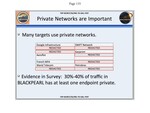
A slide arguing that many targets use private networks — Google's infrastructure, the SWIFT network, Gazprom, Aeroflot, the French foreign ministry, Warid Telecom and Petrobras — with a survey finding that 30 to 40 percent of BLACKPEARL traffic has at least one private endpoint.
Programs: BLACKPEARL -
Procedures Used By The National Security Agency For Targeting Non-United States Persons Reasonably Believed To Be Located Outside The United States To Acquire Foreign Intelligence Court Information Pursuant To Section 702 Of The Foreign Intelligence Surveillance Act Of 1978 [pdf]
The NSA’s 2009 Section 702 targeting procedures lay out how analysts decide who can be surveilled without a warrant, supposedly limiting spying to foreigners abroad. In reality, the rules give the agency wide latitude to presume people are foreign, rely on vague “totality of the circumstances” tests, and allow broad technical methods like IP filters and metadata checks. Oversight is mostly internal and after-the-fact, creating significant potential for U.S. communications to be swept up with little accountability.
People: Holder, Eric H. Jr. -
PROFILING SSL AND ATTRIBUTING PRIVATE NETWORKS [pdf]
A TOP SECRET GCHQ presentation introducing two prototype cloud analytics — FLYING PIG, a knowledge base for investigating TLS/SSL traffic at scale across approximately 20 billion events per week, and HUSH PUPPY, a tool for attributing private network traffic to identifiable organisations — with live interface screenshots demonstrating queries against mail.ru infrastructure and operational successes including identification of the Afghan Ministry of Defence network and a foreign Ministry of Foreign Affairs VSAT network.
Programs: FLYINGPIG · HUSHPUPPY · QUICKANT · GEOFUSION · LEGIONJADE · LEGIONRUBY · MAKERSMARK · XKEYSCORE · NOSEYPARKER“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Greenwald, Glenn · Kaz, Roberto · Casado, José