Classification: SI 265 documents
Search documents matching “SI” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
PRISM (US-984XN) expanded its impact [pdf]
FY2012 figures for PRISM: 24,096 end-product reports (up 27 percent), the most-cited SIGAD in first-party reporting at 15.1 percent, 1,477 reports cited in the President's Daily Brief, tasked selectors up 32 percent to 45,406, and taskable e-mail domains expanded from 40 to 22,000.
Programs: PRISM -
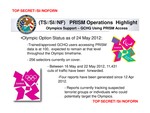
PRISM Olympic Option [pdf]
A May 2012 NSA operational highlight revealing that Britain's GCHQ was given access to the NSA's PRISM surveillance system during the London Olympics, with 100 trained British operatives secretly monitoring 256 targets and intercepting over 11,000 communications in a single week.
-
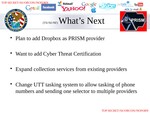
PRISM planning slide (PRISM briefing 1) [pdf]
A PRISM slide headed 'What's Next': plans to add Dropbox as a PRISM provider, add a cyber threat certification, expand collection from existing providers, and change the UTT tasking system to allow phone-number tasking.
-
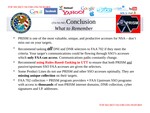
PRISM tasking slide (PRISM briefing 2) [pdf]
A PRISM slide headed 'Conclusion: What to Remember'. It says PRISM is among the most valuable NSA accesses, recommends tasking all DNI and DNR selectors to FAA 702 where they meet the criteria, and recommends Rules-Based Tasking in UTT so that PRISM and upstream SSO accesses both get the selectors.
-
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
PRISM/US-984XN Overview [pdf]
Blurry screengrabs from the "PRISM/US-984XN Overview" slide deck shown on the Fantástico O Globo broadcast. This document contains slides that are not incldued in the slides published by The Washington Post, The Guardian, Le Monde, and others.
-
Private Networks are Important [pdf]
A slide arguing that many targets use private networks — Google's infrastructure, the SWIFT network, Gazprom, Aeroflot, the French foreign ministry, Warid Telecom and Petrobras — with a survey finding that 30 to 40 percent of BLACKPEARL traffic has at least one private endpoint.
Programs: BLACKPEARL -
PROFILING SSL AND ATTRIBUTING PRIVATE NETWORKS [pdf]
A TOP SECRET GCHQ presentation introducing two prototype cloud analytics — FLYING PIG, a knowledge base for investigating TLS/SSL traffic at scale across approximately 20 billion events per week, and HUSH PUPPY, a tool for attributing private network traffic to identifiable organisations — with live interface screenshots demonstrating queries against mail.ru infrastructure and operational successes including identification of the Afghan Ministry of Defence network and a foreign Ministry of Foreign Affairs VSAT network.
Programs: FLYINGPIG · HUSHPUPPY · QUICKANT · GEOFUSION · LEGIONJADE · LEGIONRUBY · MAKERSMARK · XKEYSCORE · NOSEYPARKER“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Greenwald, Glenn · Kaz, Roberto · Casado, José -
PROJECT BULLRUN Classification Guide [pdf]
This BULLRUN classification guide outlines the NSA’s highly secretive methods for undermining and exploiting encryption technologies through a combination of cryptanalysis, industry collaboration, covert implants, and network exploitation. It specifies strict classification protocols for capabilities against protocols like TLS/SSL, VPNs, VoIP, and webmail, emphasizing secrecy around sources, methods, and industry partnerships that make commercial encryption systems deliberately vulnerable.
Programs: BULLRUN · APERIODIC · AMBULANT · AUNTIE · PAINTEDEAGLE · PAWLEYS · PITCHFORD · PENDLETON · PICARESQUE · PIEDMONT“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · Ball, James · Borger, Julian · Greenwald, Glenn · Perlroth, Nicole · Larson, Jeff · Shane, Scott -
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
QUANTUM Shooter SBZ Notes [pdf]
An NSA WikiInfo technical reference page describing the QUANTUM shooter infrastructure — covering how compromised internet hosts are configured with STRAITBIZARRE implants using FELONYCROWBAR and Deployed Node Documents, the CHIMNEYPOOL/FRIEZERAMP communications architecture linking shooters to TURBINE via SURPLUSHANGAR and HANGARSURPLUS diodes, and GCHQ's distinct MHS shooter configuration that suppresses callbacks entirely.
Programs: QUANTUM · QUANTUMSHOOTER · FREEFLOW · CHIMNEYPOOL · FELONYCROWBAR · STRAITBIZARRE · SURPLUSHANGAR · HANGARSURPLUS · PASSAGEHILL · FORESTPLACE · FUSSYKEEL · FINGERGNOME · FROZENEARTH · FRIEZERAMP · ISLANDTRANSPORT · GENIE · MIDDLEMAN · WEBSNIPERGATEWAY · WAITAUTO · ZOMBIEARMY · FIPTRIX · TURBINE -
QUANTUMTHEORY CT Successes [pdf]
This document details a successful NSA counterterrorism cyber operation in which analysts used QUANTUM techniques to deploy the UNITEDRAKE implant—equipped with keylogging and USB collection tools—against Al-Qaeda coordinator Muhsin al-Fadhli in Iran, even after detecting Kaspersky antivirus software on the target system. The operation yielded significant intelligence on Al-Qaeda communications, document forgery activities, and associated operatives.
Programs: QUANTUMTHEORY · ANCIENTBREW · VALIDATOR · QUANTUM · QUANTUMCOWBOY · UNITEDRAKE · GROK · SALVAGERABBITPeople: al-Fadhli, Muhsin -
Real-Time Regional Gateway Cloud Analytics for Forward Users [pdf]
This document outlines the NSA’s Real-Time Regional Gateway (RT-RG) program, a global cloud-based signals intelligence system designed to provide near real-time data analysis and targeting support for military and intelligence operations. It details the transition to scalable cloud architectures such as GHOSTMACHINE and Cloudbase, enabling massive data retention, exploitation, advanced geolocation, and automated analytics for tracking high-value targets across multiple theaters, including Afghanistan, Iraq, and the Horn of Africa.
Programs: RT-RG · GOLDMINER · GEOT · AGENTLOGIC · SHARKFINN · SKS · PANOPTICON · DRT · CIDNE · JUGGERNAUT · LOPERS · TALIS · MATTERHORN · AIRHANDLER · LYCANTHROPE · VOICESAIL · RETURNSPRING · SORTINGLEAD · GHOSTMACHINE · GMROYALE · GMREGAL · GMGEIST · GMIDEA · GMTOTE · GMPEN · GMPAC · GMCALM · GMMATE · GMAPPLE · GMCAVE · GMPEACH · GMDEN · GMMOUNT · GMALAMO · GMLIGHT · GMBALTIC · GMPLACE · GMPARK · GMHALO · GMCARBON · DRAGONFIRE · DOMEEXPOSE · GIANTSQUID · MAINWAY · FURIOUSCHAINSAW · SHARKFURY · NIAGARAFILES · SHARKQUERY · SHARKDOCS · OCTAVE · UTT · BEDDOWN · CHEEKYMONKEY · LAYERCAKE · CYBERTRANS · GMSEMINOLE · GMGULF · GMZILLA · HLT · JEMA · NEVIS · SEDB · CLOUDBASE · MAPREDUCE · CASPORT · WAVELEGAL“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
Report on an XKeyscore training session at the ECC / Dagger Complex [pdf]
This 2012 report details a highly successful XKEYSCORE (XKS) "Circuit Training" event at the European Cryptologic Center (ECC) in Germany, which dramatically increased analyst usage of the powerful SIGINT tool. The training, which used a "speed dating" format and gamification, helped analysts overcome their intimidation and led to significant intelligence discoveries.
-
Research & Technology – Penetrating Hard Targets [pdf]
The NSA’s “Penetrating Hard Targets” program aims at developing a cryptologically useful quantum computer capable of breaking strong encryption systems, including those protecting global financial and government communications. Conducted under the U.S. intelligence “black budget,” the program focuses on quantum physics research, engineering studies, and experimental milestones such as achieving dynamical decoupling and quantum control on semiconductor qubits, which are foundational for scaling to larger systems. A related initiative, “Owning the Net,” explores quantum communication technologies to develop new Quantum Key Distribution (QKD) attacks and assess the security of emerging encryption methods.
-
Rocoto: Implanting the iPhone [pdf]
A top secret abstract from the CIA's 2010 Trusted Computing Base Jamboree conference, describing a Johns Hopkins University Applied Physics Laboratory presentation on efforts to create intelligence community exploitation tools for the iPhone 3G, including analysis of its firmware security architecture and leveraging community jailbreak methods for signals intelligence purposes.
“The CIA Campaign to Steal Apple's Secrets” - The Intercept ↗ (2015-03-10) · Scahill, Jeremy · Begley, Josh -
Running Strategic Analytics Affecting Europe and Africa [pdf]
This Top Secret presentation from the NSA ECC (European Cryptologic Center) outlines the strategic challenges and technical methodology for conducting signal intelligence operations across Europe and Africa. It emphasizes a critical reliance on "Second Party" partnerships, particularly with the UK's GCHQ, and details the use of mass surveillance tools like XKEYSCORE to track terrorism, smuggling, and human trafficking networks.
Programs: XKEYSCORE · RTRG · DISTILLERY · CLOUD · GHOSTMACHINE · NIAGARAFILES · WHIZBANG · MAPREDUCE -
S3285/InternProjects [pdf]
A WikiInfo page from NSA's Persistence Division (S3285) listing intern project proposals covering firmware implants, BIOS-level persistence, hard drive exploitation and CNA capabilities — including IRATEMONK hard drive firmware implants across multiple vendors, POLITERAIN destructive attack tools, BERSERKR BIOS-resident backdoor, GOPHERRAGE hypervisor implant and CASTLECRASHER Windows payload execution.
Programs: POLITERAIN · PASSIONATEPOLKA · ARGYLEALIEN · BARNFIRE · IRATEMONK · SADDLEBACK · ALTEREDCARBON · FAKEDOUBT · PLUCKHAGEN · EASYKRAKEN · CASTLECRASHER · JUMPDOLLAR · MOPNGO · BERSERKR · GOPHERRAGE · WISTFULTOLL · CENTRICDUD · STYLISHCHAMP · SIERRAMIST · WICKEDVICAR · SPITEFULANGEL · ROGUESAMURAI · SIERRAMISTFREE · VALIDATOR · MOUSETRAP · BORGERKING · KIRKBOMB · SODAPRESSED · BENTWHISTLE · TWISTEDKILT · TORNSTEAK -
SCARLETFEVER [pdf]
NSA WikiInfo page describing SCARLETFEVER — the second LONGHAUL cryptanalytic capability, a message-driven cryptologic exploitation service for DNSC (Data Network Session Cipher) traffic serving clients including TURMOIL, WEALTHYCLUSTER and the TEe, communicating via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: SCARLETFEVER · LONGHAUL · TURMOIL · WEALTHYCLUSTER · TEE · ISLANDTRANSPORT · ISLANDHIDEAWAY · POISONNUT · PICARESQUE -
Shaping Diagram [pdf]
This hand-drawn diagram detail an NSA methodology for intercepting and redirecting internet traffic. The approach involves manipulating data flows through a controlled fiber cable, leveraging Computer Network Exploitation (CNE) to capture and replicate target communications for SIGINT processing, all framed in a tongue-in-cheek, yet highly classified, presentation style.