Banner: TOP SECRET//SI//REL TO USA, FVEY 14 documents
Search documents matching “TOP SECRET//SI//REL TO USA, FVEY” →The marking line each document prints.
Graphs
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Computer Network Exploitation (CNE) Classification Guide / 2-59 [pdf]
A NSA/TAO classification guide establishing the precise classification level for 41 categories of information about computer network exploitation operations — covering remote and physical subversion methods, CNE tools and techniques, supply chain operations, hardware implants, off-net field operations, zero-day vulnerabilities, and cryptographic material acquired through CNE.
“Core Secrets: NSA Saboteurs in China and Germany” - The Intercept ↗ (2014-10-10) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Maass, Peter · Poitras, Laura · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
Exploiting Foreign Lawful Intercept (LI) Roundtable [pdf]
Top-secret PowerPoint presentation, "Exploiting Foreign Lawful Intercept Roundtable," highlights the agency’s strategy to exploit vulnerabilities in lawful intercept systems from telecom companies, such as Ericsson, Motorola, and Nokia, in countries like Mexico, Indonesia, and Egypt. The presentation also discusses NSA's use of various "Fingerprints" for identifying data and its collaboration with industry players and foreign lawful intercept systems.
“A Death in Athens” - The Intercept ↗ (2015-09-28) · “Americans and Greeks started the 2004 wiretaps together” - Kathimerini ↗ (2015-09-29) · Bamford, James · Petropoulos, Aggelos -
How do we do SIGDEV or private networks? [pdf]
Top Secret SIGINT Development (SIGDEV) briefing explains how analysts conduct reconnaissance on private networks, noting that many targets rely on them and that 30–40% of traffic surveyed in BLACKPEARL has at least one private endpoint. It demonstrates the ROYALNET tool and its analytics for identifying network features, NetStrings, and links likely to carry a target’s traffic, with named targets and feature sets including Google’s infrastructure, the SWIFT banking network, the French Ministry of Foreign Affairs, Brazil’s Petrobras, and Huawei.
People: Higgins, Jean -
I hunt sys admins [pdf]
These internal documents outline the NSA’s strategy for identifying and targeting foreign system administrators to gain "keys to the kingdom" access to global network infrastructure. By correlating disparate datasets—such as passive telnet/SSH metadata and personal social media/webmail logins—the agency identifies personal accounts to facilitate QUANTUM-based hacking operations and network "pwnage."
-
MHS Leverages XKS for QUANTUM Against Yahoo and Hotmail [pdf]
This document describes a technical study conducted at Menwith Hill Station (MHS) in the UK. The study used XKEYSCORE (XKS) to evaluate the feasibility of launching QUANTUMTHEORY "man-on-the-side" attacks against users of Yahoo and Hotmail. Analysts developed a specialized Map/Reduce analytic called DRAGGABLEKITTEN to perform deep packet analysis on bulk internet traffic. The study concluded that 90% of Yahoo sessions and 50% of Hotmail sessions contained the specific technical "keywords" (such as unique cookies or headers) within a single data packet required to trigger a successful automated injection of malware.
-
Net Defense from Encrypted Communications [pdf]
A NSA Technology Directorate briefing from February 2012 describing BLUESNORT — a capability that repurposes GALLANTWAVE's SSL/TLS decryption pipeline for network defence, re-injecting decrypted traffic into TURMOIL Stage 1 Prime where BLUESNORT detects malware and other malicious activity — representing description of NSA using its own bulk decryption infrastructure for cyber defence as well as intelligence collection.
-
NSA Intelligence Relationship with New Zealand [pdf]
An April 2013 NSA information paper on the SIGINT relationship with New Zealand's GCSB, listing what each side provides: GCSB collection on China, Japanese, North Korean, Vietnamese and South American diplomatic communications, South Pacific Island nations, Pakistan, India, Iran, Antarctica and French police and nuclear testing activities in New Caledonia, and its role since 2004 as the Intelligence Community's lead on the Bangladesh counterterrorism target. It also covers GCSB's operational lead on cyber, the compliance review that followed its assistance to New Zealand law enforcement under Director Ian Fletcher, and its term as chair of SIGINT Seniors Pacific (SSPAC).
People: Fletcher, Ian“Snowden revelations: Nicky Hager and Ryan Gallagher: New Zealand's spy reach stretches across globe” - The New Zealand Herald ↗ (2015-03-11) · “New Zealand Targets Trade Partners, Hacks Computers in Spy Operations” - The Intercept ↗ (2015-03-10) · “Leaked papers reveal NZ plan to spy on China for US” - The New Zealand Herald ↗ (2015-04-19) · “New Zealand Plotted Hack on China With NSA” - The Intercept ↗ (2015-04-18) · “New Zealand Spy Data Shared With Bangladeshi Human Rights Abusers” - The Intercept ↗ (2015-04-15) · “Secret documents shine light on GCSB spying in Bangladesh” - The New Zealand Herald ↗ (2015-04-16) · Hager, Nicky · Gallagher, Ryan · Fisher, David -
NSA’s intelligence relationship with Australia [pdf]
This document summarizes the close intelligence partnership between the U.S. NSA and Australia’s Defence Signals Directorate (DSD), highlighting collaboration on cyber operations, SIGINT collection, and military support. It emphasizes Australia’s contributions through satellite access, geolocation, and terrorism-related communications, particularly in the Pacific region, while noting shared focus on China and joint participation in multinational intelligence coalitions.
-
NWP2 NSA [pdf]
The July 2012 issue of the Yakima Research Station's internal newsletter, covering the station's upcoming 40th anniversary celebrations, its origins under the ECHELON programme for INTELSAT collection during the Cold War, and a Norwegian partner enablement operation, alongside routine staff and community content.
Programs: ECHELON -
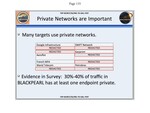
Private Networks are Important [pdf]
A slide arguing that many targets use private networks — Google's infrastructure, the SWIFT network, Gazprom, Aeroflot, the French foreign ministry, Warid Telecom and Petrobras — with a survey finding that 30 to 40 percent of BLACKPEARL traffic has at least one private endpoint.
Programs: BLACKPEARL -
PROJECT BULLRUN Classification Guide [pdf]
This BULLRUN classification guide outlines the NSA’s highly secretive methods for undermining and exploiting encryption technologies through a combination of cryptanalysis, industry collaboration, covert implants, and network exploitation. It specifies strict classification protocols for capabilities against protocols like TLS/SSL, VPNs, VoIP, and webmail, emphasizing secrecy around sources, methods, and industry partnerships that make commercial encryption systems deliberately vulnerable.
Programs: BULLRUN · APERIODIC · AMBULANT · AUNTIE · PAINTEDEAGLE · PAWLEYS · PITCHFORD · PENDLETON · PICARESQUE · PIEDMONT“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · Ball, James · Borger, Julian · Greenwald, Glenn · Perlroth, Nicole · Larson, Jeff · Shane, Scott -
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
SUSLOW Monthly Report for March 2013 [pdf]
People: Dotcom, Kim“Snowden revelations: Nicky Hager and Ryan Gallagher: New Zealand's spy reach stretches across globe” - The New Zealand Herald ↗ (2015-03-11) · “New Zealand Targets Trade Partners, Hacks Computers in Spy Operations” - The Intercept ↗ (2015-03-10) · “New Zealand Plotted Hack on China With NSA” - The Intercept ↗ (2015-04-18) · “Leaked papers reveal NZ plan to spy on China for US” - The New Zealand Herald ↗ (2015-04-19) · Hager, Nicky · Gallagher, Ryan · Fisher, David -
Types of IAT - Advanced Open Source Multi-hop [pdf]
This top-secret NSA/GCHQ document provides a detailed technical overview of the Tor network, including how it works, its strengths as the “king of high secure, low-latency Internet anonymity,” methods for identifying Tor traffic, censorship-driven protocol obfuscation, and ongoing intelligence efforts to analyze, fingerprint, and exploit Tor through passive SIGINT and active research, including collaboration between US and UK agencies.
People: Appelbaum, Jacob