Tag: traffic analysis 49 documents
Search documents matching “traffic analysis” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Instant-Gratification SIGINT SIDtoday [pdf]
An intelligence analysis intern describes his tour in Iraq and his belief that signals intelligence was “mostly responsible” for bringing an end to the al-Zarqawi terrorist network in Mosul.
People: Hussein, SaddamThe Intercept ↗ (2018-08-15) -
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
Interview with... Carl Johnson, Assistant Deputy Director for Customer Relationships (S1) SIDtoday [pdf]
A senior SID official is interviewed about his career at the agency. His most memorable experience was managing the emergency landing of a U.S. Navy spy plane in China in 2001.
The Intercept ↗ (2016-12-07) -
Losing Traffic and Wondering Why? SIDtoday [pdf]
The Resource Outage Coordination Center maintains SPRINGRAY, a database of all outages across the NSA.
Programs: SPRINGRAYPeople: Strauss, JaniceThe Intercept ↗ (2018-03-01) -
MHS Leverages XKS for QUANTUM Against Yahoo and Hotmail [pdf]
This document describes a technical study conducted at Menwith Hill Station (MHS) in the UK. The study used XKEYSCORE (XKS) to evaluate the feasibility of launching QUANTUMTHEORY "man-on-the-side" attacks against users of Yahoo and Hotmail. Analysts developed a specialized Map/Reduce analytic called DRAGGABLEKITTEN to perform deep packet analysis on bulk internet traffic. The study concluded that 90% of Yahoo sessions and 50% of Hotmail sessions contained the specific technical "keywords" (such as unique cookies or headers) within a single data packet required to trigger a successful automated injection of malware.
-
Mobile Apps Checkpoint Meeting Archives [pdf]
This GCHQ document tracks project checkpoints from December 2009 to July 2010, focusing on the rollout and operationalization of mobile apps, TERRAIN system upgrades, GTP/GRX access, and converged event processing. Key themes include coordinating multi-team dependencies, addressing technical gaps in handset and app data characterization, and ensuring timely delivery of milestones like MIP-1.
Programs: TERRAIN · PRESTON · XKEYSCORE · BEGAL · TAMING PASTRIES · MILKWHITE · MVR · SOCIAL ANTHROPOID · INTEGER SPIN · MUTANT BROTH · GEO FUSION · MARBLED GEKO · BLACKHOLE · ACTOR ACTION · TRAFFICMASTER · HARD ASSOC · MIRTF · HEARTBEAT · SILVER LINING · GREENHEART · EREPO · MAGLITE · POKERFACE · BOSTROM · MIDDLESEX GREEN · ENCHANTERSS · HAUSTORIUM · SALAMANCA · BROADOAK · MONKEY PUZZLE · TACHO · EREPO GAMMA · NINJA · PEBBLE BED · GOLDEN EYE · STRAPROC · STARPROC · LOOKING GLASS · SORCERER · SOCIAL ANIMAL · GTE · NGE · PPF · IIB · UDAQ · MES · TERRAINS · CCDF · SINO · GDR · OSDS · LECKWITH -
New Hire Story: What Is a Loadmaster? SIDtoday [pdf]
Anecdote about military jargon.
The Intercept ↗ (2016-08-10) -
Private Networks are Important [pdf]
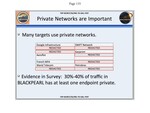
A slide arguing that many targets use private networks — Google's infrastructure, the SWIFT network, Gazprom, Aeroflot, the French foreign ministry, Warid Telecom and Petrobras — with a survey finding that 30 to 40 percent of BLACKPEARL traffic has at least one private endpoint.
Programs: BLACKPEARL -
PTC Glossary [pdf]
This GCWiki PTC Glossary excerpt defines SIGINT-related telecom terms—IMEI, IMSI, INMARSAT—and documents internal collection systems (e.g., INCENSER at Bude) and targeting notes (which identifiers are useful for targeting and which are not). It’s a technical reference for signals analysts describing selectors, collection sources, and operational caveats.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
QUANTUMINSERT [pdf]
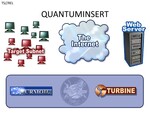
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
Report on an XKeyscore training session at the ECC / Dagger Complex [pdf]
This 2012 report details a highly successful XKEYSCORE (XKS) "Circuit Training" event at the European Cryptologic Center (ECC) in Germany, which dramatically increased analyst usage of the powerful SIGINT tool. The training, which used a "speed dating" format and gamification, helped analysts overcome their intimidation and led to significant intelligence discoveries.
-
SSO Collection Optimization [pdf]
This is another presentation on problems with the National Security Agency's overcollection of address books and buddy lists and its efforts to weed out useless content. See also EFF_-_20131104-wapo-optimization_google
-
Supporting Internet Operations - Special Source Access [pdf]
In this document GCHQ outlines its plans for expanding internet operations, focusing on increasing access to 10G bearers and enhancing its intercept and egress capabilities by 2011. The agency highlighted that “25 percent of all internet traffic” transits the U.K. through approximately 1,600 different 10-gigabit cables, and it noted that it could “survey the majority of the 1,600” to “select the most valuable to switch into our processing systems.”
-
TAC's Target Development Services (TDS): In the Spotlight and Behind the Scenes SIDtoday [pdf]
A profile of Target Development Services, which offers training in "traffic analytic techniques and SIGINT exploitation of advanced communications technologies" and runs tools used by over 4,000 analysts for contact chaining and SMS analysis. The author includes a list of success stories.
People: Mohammed, Khalid SheikhThe Intercept ↗ (2016-12-07) -
Tailored Access Operations, FOXACID, QUANTUM [pdf]
These NSA presentation slides detail "QUANTUM," a sophisticated system that allows the agency to intercept internet traffic and inject malware onto target computers with up to 80% success rates, far exceeding traditional spam-based methods. The system works by monitoring internet traffic for specific identifiers (like Yahoo or Facebook cookies), then racing to inject malicious code before legitimate web servers can respond, thereby compromising targets' computers without their knowledge and establishing persistent backdoor access.
Programs: FOXACID · QUANTUM · QUANTUMTHEORY · QUANTUMBISCUIT · VALIDATOR · OLYMPUS · UNITEDRAKE · OLYMPUSFIRE · SSO · FORESTPLACE -
TEMPORA -- "The World's Largest XKEYSCORE" -- Is Now Available to Qualified NSA Users [pdf]
This document announces expanded NSA analyst access to TEMPORA, GCHQ’s massive XKEYSCORE‑based internet buffer, positioning it as the largest single XKEYSCORE data source in existence. It promotes TEMPORA as a high‑value discovery and development platform for large‑scale internet surveillance.
-
The Prestigious Gold Nugget Award Goes To... SIDtoday [pdf]
An NSA employee received an award for his breakthrough work intercepting Iranian naval communications.
The Intercept ↗ (2019-05-29) -
TLS Trends: A roundtable discussion on current usage and future directions [pdf]
A presentation by Canada's Communications Security Establishment describing their TLS trend analysis programme, which systematically tracked SSL/TLS encryption parameters across warranted collection and Special Source access to identify cryptanalytic opportunities, monitor target behaviour and collaborate with GCHQ on exploiting weaknesses in widely-used encryption implementations.
-
Tor - 2006 CES Summer Program [pdf]
The following document is a 2006 research paper produced for the NSA's "Cryptanalysis and Exploitation Services" office. It lays out the technical features of Tor and proposes a number of theoretical and practical attacks, some of which the NSA developed and used in subsequent years. Among other things, the paper describes an NSA-written adaptation of Tor, "indistinguishable from an original Tor client," which enables the NSA to gather intelligence inside the network. It also describes two kinds of "denial of service" attacks against Tor, code-named Coil and Flower, which are used to divert would-be anonymous communications into open channels.
Programs: MJOLNIR -
TOR deanonymisation research (MIP) [pdf]
A TOP SECRET GCHQ wiki page documenting the research task on Tor deanonymisation — the project page linking the entry-exit correlation attack described in the OPC-MCR presentation to its formal research output, confirming the attack was successfully documented in OPC-M/TECH.B/61, presented at SANAR11, and planned for prototyping in the REMATION II workshop.