Tag: implants 63 documents
Search documents matching “implants” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
FOXACID SOP for Operational Management of FOXACID Infrastructure (Draft) [pdf]
This document is an NSA standard operating procedure (SOP) manual detailing how to manage and operate the FOXACID system, which delivers malware to targets through tools like SECONDDATE and BADDECISION. It provides technical instructions for tracking, deploying, and maintaining covert web-based infections used in global cyber operations.
Programs: FOXACID · FOXSEARCH · WAITAUTO · RAISEBED · FORRESTPLACE · FOXHelp · PUZZLECUBE · YACHTSHOP · SECONDDATE · MAGIC SQUIRREL · MAGICBEAN · FINKCOAT · FRUGALSHOT · QUANTUM · FERRETCANNON · BEACHHEAD · OLYMPUS · UNITERAKE · DIRESCALLOP · DEEPFREEZE · FINKDIFFERENT · DISABLEVALOR · VALIDATOR · MISTYVEAL · UNITEDRAKE · PEDDLE CHEAP · PKTWENCH · FORESTPLACE · FOXCONTACT · EASYHOOKUP · DEMENTIAWHEEL · CASTLECREEK · ROCHELP · QUANTUMINSERT · FABULOUSFABLE · WATCHER · FROZENGAZE · FABFAB · DARKFIRE · CRYPTICSENTINEL · DARKHELMET · PSP · WILLOWVIXEN -
GCHQ – Computer Network Exploitation [pdf]
This document outlines GCHQ’s Computer Network Exploitation (CNE) capabilities, detailing how teams remotely access computers and networks without owners’ consent to gather intelligence, support operations, and conduct effects. It also covers operational tools, techniques, infrastructure, joint working with partners, deconfliction, and challenges such as avoiding detection and meeting increasing intelligence demands.
-
Getting Close to the Adversary – Forward-based Defense with QFIRE (June 3, 2011) [pdf]
This document describes the QFIRE project which is designed to give the NSA a global, low-latency platform for “forward-based defense”, enabling real-time detection and manipulation of Internet traffic close to its source. By co-locating passive sensors (TURMOIL), decision logic (TURBINE), and injection capabilities, QFIRE can rapidly reset connections, redirect targets for exploitation, inject malicious payloads, and even seize control of botnets. It operates as part of the broader QUANTUMTHEORY architecture, leveraging both cooperative and non-cooperative infrastructure worldwide to enable CNE/CND/CNA effects with minimal delay.
Programs: QFIRE · QUANTUMTHEORY · TURBULENCE · TURMOIL · TURBINE · TUTELAGE · QUANTUM · QUANTUMSKY · QUANTUMINSERT · QUANTUMBOT · QUANTUMCOPPER · STRAIGHTBIZARRE · BLINDDATE · TUMULT · ISLANDTRANSPORT · SURPLUSHANGAR · MIDDLEMAN · SCSnet · WEALTHYCLUSTER · SSO -
Hackers are Humans too - Cyber leads to CI leads [pdf]
This document from Canada’s Communications Security Establishment (CSE) analyzes the Russian hacking team MAKERSMARK, highlighting how its operators misused technically sophisticated but poorly secured infrastructure, mixing personal and operational activity, which made them traceable despite their advanced tools. It details CSE’s methods for attributing cyber intrusions, monitoring malware-infected systems, and exploiting operational security lapses to gain intelligence on Russian cyber operations.
-
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
HIMR Data Mining Research Problem Book [pdf]
This document is a research roadmap created by GCHQ for the Heilbronn Institute for Mathematical Research (HIMR). Its purpose is to guide long-term mathematical and data-mining research that could improve signals intelligence (SIGINT) capabilities. It outlines key research problems, datasets, and collaboration plans between intelligence agencies and academic researchers. The main goal is to develop new algorithms and mathematical tools to analyze extremely large communications datasets produced by modern surveillance systems.
Programs: CLOUD · DISTILLERY · DISCOVER · PRESTON · LECKWITH · TERRAIN · BROADOAK · NGE · FIVEALIVE · CHARTBREAKER · FIRSTCONTACT · GEOFUSION · RADONSHARPEN-B · PRIMETIME · HIDDENOTTER · BAKERSDOZEN · CLASP · SALTYOTTER · BIRCH · SOLIDINK · FLUIDINK · MAMBA · GRINNINGROACH · PIRATECAREBEAR · AUTOASSOC · CROUCHINGSQUIRREL · HRMAP · KACHINA · SQUEAL · QUESTA · METEORSHOWER · SUNSTORM · GOLDMINE · HAGERAWEL · WOODY · BUZZ · SILVERLIBRARY · SILVERLINING · VALHALLA · MOUNTMCKINLEY · SEPANG · BLACKHOLE · SALAMANCA · HAGELAWEL · LUCKYSTRIKE · SPIKYROCK · MYOFIBRIL · INJUNCTION · PSYCHICSALMON · RAGINGBULLFROG · ROBOTICFISH · TIMIDTOAD · AURA · CARBONCOPY · CASK · CHORDAL · CRAN · INSTINCT · MADFORGE · SWAMP · VOLSUNGA · WHITERAVEN · MVR · PPF · JTRIG · MAPREDUCE · MAILORDERPeople: Tukey, John -
In-Flight GSM [pdf]
This NSA presentation outlines how the agency is reacting to the growth of mobile phone services on board commercial aircraft.
-
Industrial-Scale Exploitation [pdf]
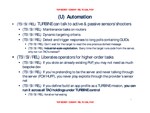
This top-secret NSA document details the operational philosophy behind the TURBINE system's transition to "industrial-scale exploitation." By integrating with both active and passive sensors, TURBINE automates the delivery of malware and the maintenance of network implants, specifically targeting routers and server-side code execution.
-
Intellipedia – Air Gapped Network Threats [pdf]
This document from an internal wiki for the U.S. intelligence community, surveys threats to so-called air-gapped systems, arguing that supply-chain compromises, physical implants (BIOS, KVMs, peripherals), infected removable media, and enabled wireless/emanations present realistic paths for adversaries to bridge isolated networks. It assesses likelihoods and attack vectors (including insider help and CDS/guard exploitation), highlights specific historic incidents (Agent.BTZ/MAKERSMARK), and recommends strict removable-media policies, TEMPEST countermeasures, and rigorous cross-domain guard protections to mitigate the risk.
People: Witte, Griff · Warren, Peter · Streeter, Michael · Watson, Paul · Louchard, Bjørn · Crawford, George · Rudge, David · Terrazas, Michael -
Is there "fifth party" collection? [pdf]
This NSA internal Q&A forum discussion reveals "fifth party collection"—where the NSA passively intercepts data from one intelligence service (South Korea) that has compromised another service's (North Korea) computer network exploitation operations, creating a three-layer chain where NSA exploits Actor One's access to Actor Two's CNE activities against shared targets. The thread provides concrete examples including NSA leveraging South Korean implants on North Korean officials' computers (who themselves were conducting CNE operations) and stealing zero-day exploits from unidentified foreign intelligence services by passively monitoring their successful attacks.
-
Moving Data Through Disconnected Networks - Delay-Tolerant Networking and the IC [pdf]
This June 2012 NSA Laboratory for Telecommunications Sciences presentation details Delay-Tolerant Networking (DTN) applications for surveillance operations, including covert communications in denied areas, data exfiltration from isolated networks, unwitting data mules, and integration with TAO's CHIMNEYPOOL implant framework. The document reveals R4 development of FUZZYLINT, an ultra-lightweight DTN implementation designed to enable multi-hop exfiltration from implants without requiring direct physical access.
People: Vahdat, Amin · Becker, David · Juang, Philo · Oki, Hidekazu · Wang, Yong · Martonosi, Margaret · Peh, Li-Shiuan · Rubenstein, Daniel · Grossglauser, Matthias · Tse, David N. C. · Fall, Kevin · Shah, Rahul C. · Roy, Sumit · Jain, Sushant · Brunette, Waylon · Lindgren, Anders · Doria, Avri · Schelen, Olov · Small, Tara · Haas, Zygmunt J. · Zhao, Wenrui · Ammar, Mostafa · Zegura, Ellen · Ginzboorg, Philip · Kärkkäinen, Teemu · Nagata, Akira · Lenders, Vincent · Legendre, Franck · May, Martin · Karlsson, Gunnar · Du, Bowei · Demmer, Michael · Brewer, Eric · Ott, Jörg · Pitkänen, Mikko Juhani · Han, Bo · Hui, Pan -
NSA ANT Catalog [pdf]
The NSA ANT catalog is a leaked confidential collection of sophisticated surveillance and hacking tools developed by the agency’s Tailored Access Operations unit (TAO), detailing hardware and software implants capable of covertly infiltrating computers, networks, and mobile devices. It revealed the NSA’s ability to conduct remote surveillance, implant malware, and maintain persistent access to targeted systems without users’ knowledge.
Programs: IRONCHEF · PROTOSS · STRONGMITE · GECKO II · STRAITBIZARRE · WAGONBED · UNITEDRAKE · DEITYBOUNCE · ARKSTREAM · TUNING FORK · GODSURGE · FLUXBABBITT · JETPLOW · BANANAGLEE · HALLUXWATER · TURBOPANDA · FEEDTROUGH · ZESTYLEAK · GOURMETTROUGH · SOUFFLETROUGH · HEADWATER · HAMMERMILL · HIT · SIERRAMONTANA · VALIDATOR · SCHOOLMONTANA · STUCCOMONTANA · CTX4000 · PHOTOANGLO · LOUDAUTO · ANGRYNEIGHBOR · NIGHTWATCHER · VIEWPLATE · LFS-2 · TAWDRYYARD · RAGEMASTER · CROSSBEAM · CHIMNEYPOOL · ROCKYKNOB · CANDYGRAM · CYCLONE Hx9 · TYPHON · EBSR · LANDSHARK · ENTOURAGE · HOLLOWPOINT · GALAXY · GENESIS · NEBULA · TYPHON HX · WATERWITCH · NIGHTSTAND · SPARROW II · BLINDDATE · DROPOUTJEEP · ARTEMIS · DROPMIRE · STRAITBIZZARE · FREEFLOW · TURBULENCE · GOPHERSET · MONKEYCALENDAR · TOTECHASER · TOTEGHOSTLY · PICASSO · TOTEGHOSTLY 2.0 · FRIEZERAMP · GENIE · VAGRANT · GOTHAM · SURLYSPAWN · GINSU · BULLDOZER · KONGUR · OMNIGAT · IRATEMONK · SERUM · SLICKERVICAR · RETURNSPRING · WISTFULTOLL · JIMSQ · SEAGULLFARO · SWAP · SNEAKERNET · TWISTEDKILT · HOWLERMONKEY · SUTURESAILOR · YELLOWPIN · CONJECTURE · SPECULATION · JUNIORMINT · MAESTRO · MAESTRO-II · SOMBERKNAVE · OLYMPUS · TRINITY · COTTONMOUTH-I · COTTONMOUTH-II · TURBINE · COTTONMOUTH-III · FIREWALK · DANDERSPRITZ -
NSA QUANTUM Tasking Techniques for the R&T Analyst [pdf]
A classified NSA training presentation, prepared by Booz Allen Hamilton, walking analysts step-by-step through how to secretly hack into a target's computer by hijacking their everyday internet traffic — exploiting platforms like Yahoo and Facebook to silently inject malware without the target's knowledge.
Programs: QUANTUM · QUANTUMTHEORY · QUANTUMNATION · VALIDATOR · COMMONDEER · SEASONEDMOTH · SMOTH · MARINA · FOXACID · RADIUS · QUANTUMBISCUIT · ALTEREGO · DOGCOLLAR · FOREMAN · ANCHORY · BRUTUS · REACTOR · SPARKLEPONY · WINDCHASER · YACHTSHOP · MUTANTBROTH · FOXSEARCH · WHITELIST · SSO · PSC -
NSA Supply Chain Attack From PMR 4-24-13 [pdf]
This document is a top-secret NSA report detailing a SIGINT development operation in which a classified Voice-over-IP network shipment was intercepted and subjected to a supply-chain interdiction, allowing NSA and its intelligence community partners to gain access to the hardware and intelligence. It describes the operational process, including tracking the shipment through China, coordinating with Tailored Access Operations (TAO), and using tools like XKEYSCORE to identify targeting selectors, ultimately enabling detailed surveillance and future operational opportunities.
-
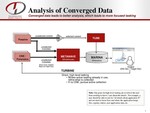
NSA Technology Directorate Analysis of Converged Data [pdf]
This document outlines the strategic integration of passive and active signals intelligence (SIGINT) to create a more efficient surveillance loop. The document centers on TURBINE, an intelligent command-and-control system designed to manage a massive network of malware implants (Computer Network Exploitation or CNE). The primary goal is to automate the extraction of data from targeted machines, effectively "converging" traditional passive collection with active hacking to refine intelligence tasking.
-
OP HIGHLAND FLING - Event Log [pdf]
A TOP SECRET operational event log from GCHQ's GCWiki documenting a January 2011 operation targeting Gemalto employees in France, Poland and elsewhere, using MUTANT BROTH cookie analysis, Facebook credentials, LinkedIn profiles and Computer Network Exploitation to identify and implant targets as part of the operation to steal SIM card encryption keys.
-
Pay attention to that man behind the curtain: Discovering aliens on CNE infrastructure [pdf]
CSEC briefing from 2010 outlines Canada’s counter–computer network exploitation efforts to detect, analyze, and pursue foreign and friendly cyber actors operating on shared CNE infrastructure. It details tools, methods, and a case study showing how hidden implants and overlapping state-sponsored operations were uncovered and attributed.
Programs: SNOWGLOBE · WARRIORPRIDE · DAREDEVIL · SLIPSTREAM · CHORDFLIER · NAMEDROPPER · WORMWOOD · REPLICANTFARM · OBELIX · SHEPHERD · CARBON · ALOOFNESS · REGBACKUP · DOGHOUSE · WALKER · CHOCOPOP · BLAZINGANGEL · WINDO · QUIVERINGSQUAB · DIESELRATTLE · CYDLL · CIVETCAT · WIDOWKEY · LASEX · PULLEDPORK · MAKERSMARK · FANNER · SEEDSPHERE · BYZANTINE · VOYEUR · SUPERDRAKE · GOSSIPGIRL · WATERMARK · DOURMAGNUM -
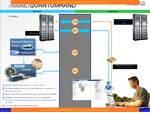
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.