Tag: cable tapping 55 documents
Search documents matching “cable tapping” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
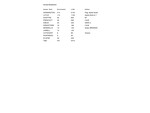
Access Breakdown [pdf]
This GCHQ document provides a technical breakdown of surveillance access points showing 11 different interception sites (with codenames like DONNINGTON, LATUS, SCEPTRE) accessing various undersea cables including Flag, Apollo North/South, BT, Cable & Wireless (C&W), SMW-3, Solas, and Verizon, totaling 541 10-gigabit connections representing 5,410 gigabits of surveillance capacity across the network.
Programs: DONNINGTON · LATUS · SCEPTRE · PRESCOTT · GIBUS · KIRKISTOWN · MONDELLO · LINNELL · CATEGORY · KNAPWEED · ELAPSE · BROKER“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
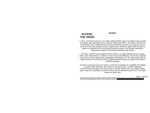
Access: Vision 2013 [pdf]
This July 2010 GCHQ strategic document outlines the agency's vision for 2013 to create "the world's biggest SIGINT engine" with access to 800 10-gigabit connections (up from existing capacity), expanding overseas operations to 60% while reducing UK-based to 40%, and developing new capabilities including computer network exploitation (CNE), exfiltration, beaconry, geolocation, and collection of "Internet Pocket Litter" like cookies and browsing data. The strategy emphasizes "scale and pace," "balance," and "agility" while claiming to operate within legal frameworks of "necessity, proportionality and authorisation," and highlights partnerships with second and third parties to access "intractable and hard targets."
Marking: SECRET -
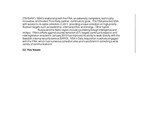
Baltic region [pdf]
This screenshot shows a part of a document which is about the growing relationship with the Swedish FRA, as an “extremely competent” partner. In 2011, the FRA gave the NSA access to “unique” material from its cable collection regarding, among other things, Russia and the Baltic region.
-
Black Budget: Special Source Access - Foreign Partner Access [pdf]
This document provides a detailed financial and operational breakdown from the NSA’s FY 2013 Congressional Budget Justification for the SSO's Foreign Partner Access project. It outlines the strategic funding for the RAMPART-A and WINDSTOP programs, which leverage international partnerships to intercept massive volumes of global communications traffic from long-haul fiber-optic cables and integrated 2nd Party architectures.
“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura · Jensen, Kristian -
BLARNEY report April 2013 [pdf]
This NSA document describes the deployment of surveillance systems (RINGBILL, TURTLEPOWER, SKIDROWE) at "TITAN POINTE" to process bulk communications data including VoIP and video teleconferencing traffic. The systems are designed to intercept, filter, and analyze high-volume network traffic using legacy architecture initially, with plans to transfer to newer processing solutions for long-term mass surveillance capabilities.
Programs: BLARNEY · RINGBILL · WEALTHYCLUSTER2 · XKEYSCORE · TRIREME · SKIDROWE · PINWALE · TITANPOINTE · VISIONQUEST · TURTLEPOWER · SKINNY -
Brown Bag Session on GNDA Is Rescheduled SIDtoday [pdf]
A top-secret session outlining gaps in cable access programs has been rescheduled.
The Intercept ↗ (2018-03-01) -
Brown Bag Session: Overview of Global Network Development Activity SIDtoday [pdf]
Global Network Development Activity is a place to experiment on techniques and automation for developing signals intelligence. One of the topics to be discussed in the brown bag is closing the gap for cable accesses, i.e. collecting signals intelligence from fiber optic cables.
Programs: GNDAThe Intercept ↗ (2018-03-01) -
Cable Master List [pdf]
This GCHQ document is a comprehensive master list of undersea fiber optic cables tracked for surveillance purposes, including both cables with UK landing points and international cables without UK connections, detailing technical specifications, ownership, capacity data, and code names for telecommunications partner companies that provided the intelligence agency with surveillance access.
Programs: PINNAGE · PFENNINGALPHA · NIGELLA · REMEDY · HIASCO · GERONTIC · SCEPTRE · PRESCOTT · KIRKISTOWN · LINNELL · CATEGORY · DACRON · KNAPWEED · ELAPSE · VITREOUS · LITTLE · STREETCAR · GIBBUS · VISAGE · LATUS · NUMDAH“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
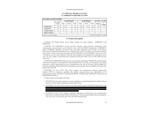
Cables we do not currently have good access [pdf]
This GCHQ document, titled "Cables we do not currently have good access," lists numerous undersea fiber-optic cables along with their active data capacity ("Lit Capacity"), indicating the substantial portion of global telecommunications infrastructure where the agency lacks adequate surveillance access, in contrast to other internal reports detailing cables it successfully monitors.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
CSEC SIGINT Cyber Discovery: Summary of the current effort [pdf]
This document provides a overview of the Communications Security Establishment Canada (CSEC) cyber operations, detailing its SIGINT, CNE (Computer Network Exploitation), and cyber counterintelligence programs, including tools like WARRIORPRIDE, REPLICANTFARM, and EONBLUE for threat detection, anomaly discovery, and metadata production. It outlines operational procedures, analytic methodologies, and collaborative frameworks with domestic and Five Eyes partners for sharing intelligence, tipping/cueing, and integrating cyber and traditional counterintelligence efforts.
Programs: REPLICANTFARM · SLIPSTREAM · WARRIORPRIDE · DAREDEVIL · CHORDFLIER · NAMEDROPPER · WORMWOOD · OBELIX · SHEPHERD · CARBON · REGBACKUP · DOGHOUSE · WALKER · ALOOFNESS · BLAZINGANGEL · TINYWEB · QUIVERINGSQUAB · WINDO · DIESELRATTLE · WIDOWKEY · CIVETCAT · WINBEE · SSLINST · PULLEDPORK · EONBLUE · SNIFFLE · QUANTUM · XKEYSCORE · HALTERHITCH · FASTFLUX · DEADSEA · NSPACES · PPF · SSO · TKB“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan -
Denmark DDIS partnership with NSA (2013) [pdf]
This document provides classified talking points and administrative guidance for the Director of the NSA (DIRNSA) regarding the DENUSA conference and the agency’s strategic partnership with the Danish Defence Intelligence Service (DDIS). It highlights the long-standing collaboration between the two nations on specialized cable access programs and reaffirms the NSA’s commitment to maintaining and expanding access to high-capacity international fiber-optic cables transiting Danish territory.
“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura -
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
ECI WHIPGENIE Classification Guide [pdf]
A 2004 NSA classification guide for ECI WHIPGENIE, covering the agency's Special Source Operations relationships with US corporate partners for cable collection and domestic wire access, including FISA-warranted collection and FBI-assisted compelled and cooperative partnerships.
Programs: WHIPGENIE · FAIRVIEW · STORMBREW · BLARNEY · POWERPLANT · TUMBRIL · WEALTHYCLUSTER · RAGTIME · PLUS · YELLOWSTONE · SSO -
Entries From Sample SSO Accesses [pdf]
This document reveals that OAKSTAR is a covert NSA program involving corporate partnerships to access global internet traffic, while MONKEYROCKET, a sub-program of OAKSTAR, specifically targets foreign internet traffic from the Middle East, Europe, South America, and Asia for surveillance, with data funneled to the NSA’s European Technical Center for further analysis. It also notes that the data collected is stored in the YANKEE partition for processing.
-
FAIRVIEW - Corp partner since 1985 [pdf]
1 p.A note describing FAIRVIEW as a corporate partnership dating to 1985 that gives access to international cables, routers and switches through a US company which is also “aggressively involved in shaping traffic to run signals of interest past our monitors”.
Programs: FAIRVIEW -
FAIRVIEW brief overview [pdf]
This document outlines the FAIRVIEW program, established in 1985, which leverages a corporate partner to exploit international communications through cables, switches, and routers. It is one of the NSA's top sources for metadata and serialized intelligence, supporting a wide range of targets including counter-terrorism, crime, and international security issues.
Programs: FAIRVIEW -
FAIRVIEW dataflow charts April 2012 [pdf]
This document outlines data flow diagrams that show how various types of sensitive communication, including voice, fax, and modem traffic, are handled through systems operated by the NSA and its partners. These partners include corporations, telecommunications companies, ISPs, and other entities involved in processing and managing the data through secure and classified channels. The document covers processing flows for various data types, metadata, and communications systems under NSA's control, detailing how data is routed, stored, and analyzed across different platforms and sites.
Programs: FAIRVIEW · SAGUARO · TURNSTILE · MESA · TITANPOINT · RIMROCK · MAILORDER · PINECONE · BLARNEY · STONEGATE · TINSEL · CONVEYANCE · FISHWAY · NUCLEON · PINWALE · SCISSORS · COURIERSKILL · DRIFTWOOD · ASDF · FALLOUT · MARINA · LOPERS · WEALTHYCLUSTER · PUPR · CLEARSIGHT · MIDFIELD · CADENCE · BUGCATCHER · WAYLAND · DESOTO · GATEKEEP · HIGHDECIBEL · XKEYSCORE · YANKEE · TOPROCK · FASCIA · DISHFIRE · SEAGULL · BIGDIPPER · CORPORATE · LILDIPPER · HAVASU · WEALTHYCLUSTER2 · RAGTIME · TUMULT · TATTOO · DARKTHUNDER · ICYTWINS · TML-STATUS · WATERFRONT · VULCANDEATHGRIP · STEELFLAUTA · UNITY · KEYCARD · UTT · BTUBE · ISLANDTRANSPORT · SSO · MAINWAY · SSDM · TUBE · TITANPOINTE · TURMOIL · VPCS“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “Titanpointe: The NSA’s Spy Hub in New York, Hidden in Plain Sight” - The Intercept ↗ (2016-11-16) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan -
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
GCHQ access to international internet communications [pdf]
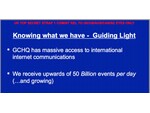
This document describes the scale of the agency's access to international internet communications, stating that GCHQ receives upwards of 50 billion events per day and that this volume is growing.
Programs: GUIDINGLIGHT“The US/UK Campaign to Demonize Social Media Companies as Terrorist Allies” - The Intercept ↗ (2014-11-26) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn -
GCHQ Report on the Technical Capabilities of the Powerful Espionage Program TEMPORA, which Allows for Full Take. [pdf]
In May 2012, GCHQ introduced the TEMPORA internet buffer capability, enabling full take collection of internet communications. This innovation provides NSA and GCHQ analysts access to extensive amounts of data, enhancing their analytical capabilities significantly.