Tag: active collection 17 documents
Search documents matching “active collection” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
CNE End Point Requirements [pdf]
This NSA/GCHQ document outlines comprehensive requirements for an endpoint surveillance systems that enables analysts to systematically identify intelligence collection needs and discover appropriate tools for data extraction from compromised computers. The framework covers capabilities for remote data collection, cross-platform intelligence integration, query functions, tasking procedures, and visualization tools across implanted networks.
Programs: STARGATE · LOOKING GLASS · QUANTUM · GOLDENEYE · XKEYSCORE · MARINA · JTRIG · BROADOAK · UTT · GLOBALREACH · GLOBALSURGE · THUGGEE · EREPO · DANCINGBEAR · HAUSTORIUM · SHAREOWN · MUTANTBROTH · MOONRAKER · CARBONROD · RUFFLE · ROCKOPERA · QUINCEY · ECLIPSE · MUGSHOT · HIGHNOTE · UDAQ2 · EKB · TURBINE · ACNO · FLAMECARPET · FUMECUPBOARD · JACKPOT · SLIPSTREAM · B13B · PSC · QUINCY · DAREDEVIL · ROADBED -
COMPUTER NETWORK OPERATIONS - GENIE [pdf]
A TOP SECRET Congressional Budget Justification entry for the NSA/CSS GENIE project — the Tailored Access Operations programme underpinning all endpoint Computer Network Operations — requesting $651.7 million and 1,870 military and civilian positions for FY2013, with plans to maintain 85,000-96,000 implant points-of-presence worldwide and 9,000-10,000 active accesses, including $25.1 million for covert purchase of software vulnerabilities and a $3.4 million supply chain implant operation targeting al-Qaeda.
-
DNI101 [pdf]
This TOP SECRET training guide, "DNI 101," provides a workflow for Digital Network Intelligence analysts on how to investigate a target's email address, detailing the specific tools, databases, and methodology used, and stressing the critical difference between initial open-source/classified research and the active "targeting" of raw SIGINT repositories like XKEYSCORE, PINWALE, and MARINA.
Programs: NKB · FOXTRAIL · FOREMAN · PINWALE · LIONHEART · XKEYSCORE · DISHFIRE · MARINA · MECWEB · MAINWAY · TRAFFICTHIEF · MAUI · ANCHORY · M3 · INTELLINK · HOMEBASE · PROTON · UTT · CADENCE · SPEEDBUMP · TUNINGFORK · MASTERSHAKE · BLACKPEARL · JACKSPARROW · ROADBED · STORYDUTY · LIONROAR · DOPHONE · UIS -
Finding and Querying Document Metadata [pdf]
This 2009 NSA training guide, created by Booz Allen Hamilton, explains how analysts can use the XKEYSCORE system to track targets by searching for "non-traditional selectors" embedded within documents, such as author names, company information, or even the hash values of company logos.
Programs: XKEYSCORE · TUNINGFORK · PINWALE · FOXACID · FOXBASE · CARBOY · CARDAMON · UNITEDRAKE · CADENCE -
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
GCHQ – Making network sense of the encryption problem (2011) [pdf]
GCHQ’s Network Analysis Centre convened a 2011 roundtable on “making network sense” of encryption, pushing a metadata-first strategy to triage SSL/TLS, IKE, OpenVPN, and SSH flows, pivot from “seed” indicators, and zero in on targets and subnets worth decrypting. The playbook leans on enrichment, AS-level scoping (explicitly citing Belgacom AS6774 GRX VPNs), and “access optimisation” to collect data pre‑encryption—passively or actively.
Programs: SQUEAL · BEARDEDPIGGY · CLOUD · IRASCIBLEHARE · IRASCIBLERABBIT · IRASCIBLEMOOSE · IRASCIBLEEMITT“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Getting Close to the Adversary – Forward-based Defense with QFIRE (June 3, 2011) [pdf]
This document describes the QFIRE project which is designed to give the NSA a global, low-latency platform for “forward-based defense”, enabling real-time detection and manipulation of Internet traffic close to its source. By co-locating passive sensors (TURMOIL), decision logic (TURBINE), and injection capabilities, QFIRE can rapidly reset connections, redirect targets for exploitation, inject malicious payloads, and even seize control of botnets. It operates as part of the broader QUANTUMTHEORY architecture, leveraging both cooperative and non-cooperative infrastructure worldwide to enable CNE/CND/CNA effects with minimal delay.
Programs: QFIRE · QUANTUMTHEORY · TURBULENCE · TURMOIL · TURBINE · TUTELAGE · QUANTUM · QUANTUMSKY · QUANTUMINSERT · QUANTUMBOT · QUANTUMCOPPER · STRAIGHTBIZARRE · BLINDDATE · TUMULT · ISLANDTRANSPORT · SURPLUSHANGAR · MIDDLEMAN · SCSnet · WEALTHYCLUSTER · SSO -
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
Is there "fifth party" collection? [pdf]
This NSA internal Q&A forum discussion reveals "fifth party collection"—where the NSA passively intercepts data from one intelligence service (South Korea) that has compromised another service's (North Korea) computer network exploitation operations, creating a three-layer chain where NSA exploits Actor One's access to Actor Two's CNE activities against shared targets. The thread provides concrete examples including NSA leveraging South Korean implants on North Korean officials' computers (who themselves were conducting CNE operations) and stealing zero-day exploits from unidentified foreign intelligence services by passively monitoring their successful attacks.
-
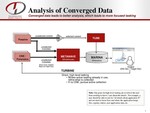
NSA Technology Directorate Analysis of Converged Data [pdf]
This document outlines the strategic integration of passive and active signals intelligence (SIGINT) to create a more efficient surveillance loop. The document centers on TURBINE, an intelligent command-and-control system designed to manage a massive network of malware implants (Computer Network Exploitation or CNE). The primary goal is to automate the extraction of data from targeted machines, effectively "converging" traditional passive collection with active hacking to refine intelligence tasking.
-
Pay attention to that man behind the curtain: Discovering aliens on CNE infrastructure [pdf]
CSEC briefing from 2010 outlines Canada’s counter–computer network exploitation efforts to detect, analyze, and pursue foreign and friendly cyber actors operating on shared CNE infrastructure. It details tools, methods, and a case study showing how hidden implants and overlapping state-sponsored operations were uncovered and attributed.
Programs: SNOWGLOBE · WARRIORPRIDE · DAREDEVIL · SLIPSTREAM · CHORDFLIER · NAMEDROPPER · WORMWOOD · REPLICANTFARM · OBELIX · SHEPHERD · CARBON · ALOOFNESS · REGBACKUP · DOGHOUSE · WALKER · CHOCOPOP · BLAZINGANGEL · WINDO · QUIVERINGSQUAB · DIESELRATTLE · CYDLL · CIVETCAT · WIDOWKEY · LASEX · PULLEDPORK · MAKERSMARK · FANNER · SEEDSPHERE · BYZANTINE · VOYEUR · SUPERDRAKE · GOSSIPGIRL · WATERMARK · DOURMAGNUM -
Project SANDSTORM [pdf]
This document shortly describes Project SANDSTORM, part of the Active Sigint Enabling Passive Geolocation (ASEPG) program at Menwith Hill, which uses Wi-Fi signal characterization and satellite-based Overhead capabilities to geolocate high-value targets, with geolocations of under 100 meters expected even for low-power signals in denied areas. It focuses on actively enabling SIGINT to track targets via 802.11 wireless networks.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
Reminder: Global Network Analyst Intern Program Showcase: 23 July SIDtoday [pdf]
Two interns will present their achievements in developing attacks against emerging technologies.
Programs: SSOThe Intercept ↗ (2017-04-24) -
TURBINE description [pdf]
These document excerpts introduces TURBINE, a revolutionary "Expert System" designed to solve the problem of scale in global hacking operations. Managed by the Tailored Access Operations (TAO) division, TURBINE marks the transition from manual, human-driven exploitation to automated, industrial-scale "Active SIGINT." While traditional "Passive SIGINT" involves eavesdropping on existing signals, Active SIGINT involves "intervention"—actively compromising target devices to extract data from within. TURBINE’s mission is to expand the NSA’s reach from a few thousand manual infections to a global network of millions of covert implants.
-
TURBULENCE - APEX - Active/passive Exfiltration [pdf]
This 2009 NSA presentation details APEX (Active/Passive Exfiltration), a TURBULENCE program component that combines passive collection infrastructure with active TAO implants to exfiltrate VPN and VoIP traffic from deep within target networks back to NSA collection systems. The system uses the FASHIONCLEFT protocol to tunnel captured packets through compromised routers and network devices, enabling decryption of VPN tunnels and collection of voice communications that would otherwise be invisible to passive surveillance.
Programs: TURBULENCE · TURMOIL · HAMMERSTEIN · HAMMERCHANT · FASHIONCLEFT · TUTELAGE · TURBINE · TRAFFICTHIEF · XKEYSCORE · ANALYTICS · PRESSUREWAVE · TOYGRIPPE · POISONNUT · FLAXENPRECEPT · FOGYNULL · FUNNELAPS · SHELLGREY · METROTUBE · VINYLSEAT · OLYMPUS · UNITEDRAKE · FIGBUILD · SURPASSPIN · ROOTKNOT · OPTICPINCH · SEAGULFARO · TREBLECLEF · CONVEY · PINWALE · SWEEPFORWARD · QUANTUM · KEYCARD · ASDF · TUBE · PUZZLECUBE · WEALTHYCLUSTER2 · COALSHOVEL · HAMMERMILL · ISLANDTRANSPORT · FASCIA · TURBINIE · APEX · PPF · AEG · FIP · SSO · PICARESQUE · PSP · IVE · PSC · CHIMNEYPOOL · CORESSC · FLASHHANDLE · IBRIDGE · CORALREEF · VAO · NUCLEON · PIQBLADE“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
VPN SigDev Basics [pdf]
A TOP SECRET VPN signals development training presentation from NSA's OTTERCREEK team introducing analysts to the six-stage workflow for discovering, assessing and exploiting VPN traffic — covering TOYGRIPPE, XKEYSCORE, DISCOROUTE and other repositories with live interface screenshots showing Iranian-German IPSec traffic and UNAMI (UN Assistance Mission for Iraq) router configurations containing pre-shared keys, including a Cuban VPN pre-shared key recovered in plaintext from a compromised router.
Programs: BLEAKINQUIRY · DISCOROUTE · TOYGRIPPE · MARINA · MASTERSHAKE · NKB · PINWALE · RENOIR · TREASUREMAP · TUNINGFORK · XKEYSCORE · GOLDPOINT · PILBEAM · RADIUS · CREAKSTILE · MAILORDER · ROADBED · DROPBOX · PPF