Tag: Tailored Access Operations 105 documents
Search documents matching “Tailored Access Operations” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
NSA's Counterterrorism (CT) Relationship with the German Federal Intelligence Service (BND) and the German Federal Office for the Protection of the Constitution (BfV) [pdf]
This April 2013 NSA talking points document prepares leadership for discussions with German intelligence services BND and BfV about counterterrorism cooperation, highlighting NSA's formal relationship with BfV approved March 20, 2013, planned provision of XKEYSCORE technology to enable German domestic surveillance, and warning that German requests for Skype interception capabilities and use of SIGINT in open court represent potential complications.
-
NSA's Offensive and Defensive Missions: The Twain Have Met SIDtoday [pdf]
The document outlines a case where NSA’s defensive malware analysis enabled offensive SIGINT teams to gain sustained access to a Chinese command-and-control server, allowing NSA to intercept intelligence China had stolen from the United Nations through a method known as fourth-party collection.
-
NSA's Technical Analysis of CNE Collection Goes Global -- A Success Story SIDtoday [pdf]
The Network Information Exploitation Target Analysis branch has six employees in Georgia who support their colleagues at the NSA’s headquarters. Recently, they took over coverage of top priority targets during a snowstorm at HQ.
The Intercept ↗ (2018-08-15) -
OSINT FUSION PROJECT [pdf]
A TOP SECRET//COMINT//REL TO USA, FVEY presentation by Lockheed Martin's Intelligence and Global Solutions division describing the OSINT Fusion Project — a programme to collect and weaponise open source intelligence from hacker forums, malicious email traffic, botnet data and commercial threat feeds to generate XKEYSCORE fingerprints for CNE targeting and fourth party collection.
-
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
QUANTUM Shooter SBZ Notes [pdf]
An NSA WikiInfo technical reference page describing the QUANTUM shooter infrastructure — covering how compromised internet hosts are configured with STRAITBIZARRE implants using FELONYCROWBAR and Deployed Node Documents, the CHIMNEYPOOL/FRIEZERAMP communications architecture linking shooters to TURBINE via SURPLUSHANGAR and HANGARSURPLUS diodes, and GCHQ's distinct MHS shooter configuration that suppresses callbacks entirely.
Programs: QUANTUM · QUANTUMSHOOTER · FREEFLOW · CHIMNEYPOOL · FELONYCROWBAR · STRAITBIZARRE · SURPLUSHANGAR · HANGARSURPLUS · PASSAGEHILL · FORESTPLACE · FUSSYKEEL · FINGERGNOME · FROZENEARTH · FRIEZERAMP · ISLANDTRANSPORT · GENIE · MIDDLEMAN · WEBSNIPERGATEWAY · WAITAUTO · ZOMBIEARMY · FIPTRIX · TURBINE -
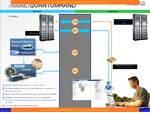
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
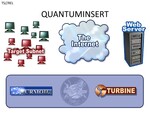
QUANTUMINSERT [pdf]
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
QUANTUMTHEORY CT Successes [pdf]
This document details a successful NSA counterterrorism cyber operation in which analysts used QUANTUM techniques to deploy the UNITEDRAKE implant—equipped with keylogging and USB collection tools—against Al-Qaeda coordinator Muhsin al-Fadhli in Iran, even after detecting Kaspersky antivirus software on the target system. The operation yielded significant intelligence on Al-Qaeda communications, document forgery activities, and associated operatives.
Programs: QUANTUMTHEORY · ANCIENTBREW · VALIDATOR · QUANTUM · QUANTUMCOWBOY · UNITEDRAKE · GROK · SALVAGERABBITPeople: al-Fadhli, Muhsin -
Re: Ehsanul Sadequee FISA Request [pdf]
This NSA email chain from April 2006 shows NSA analysts urgently requesting FBI FISA authorization documents for Ehsanul Sadequee so they could conduct a "TAO operation" (Tailored Access Operations hack) to retrieve a file he had shared, racing against the FBI's impending arrest which would invalidate their surveillance authority. The emails reveal the NSA's dependence on FBI-obtained FISA warrants to justify their operations and their need to complete the hack before Sadequee's arrest made their authorization "invalid."
Programs: CADENCEPeople: Sadequee, Ehsanul Islam -
S3285/InternProjects [pdf]
A WikiInfo page from NSA's Persistence Division (S3285) listing intern project proposals covering firmware implants, BIOS-level persistence, hard drive exploitation and CNA capabilities — including IRATEMONK hard drive firmware implants across multiple vendors, POLITERAIN destructive attack tools, BERSERKR BIOS-resident backdoor, GOPHERRAGE hypervisor implant and CASTLECRASHER Windows payload execution.
Programs: POLITERAIN · PASSIONATEPOLKA · ARGYLEALIEN · BARNFIRE · IRATEMONK · SADDLEBACK · ALTEREDCARBON · FAKEDOUBT · PLUCKHAGEN · EASYKRAKEN · CASTLECRASHER · JUMPDOLLAR · MOPNGO · BERSERKR · GOPHERRAGE · WISTFULTOLL · CENTRICDUD · STYLISHCHAMP · SIERRAMIST · WICKEDVICAR · SPITEFULANGEL · ROGUESAMURAI · SIERRAMISTFREE · VALIDATOR · MOUSETRAP · BORGERKING · KIRKBOMB · SODAPRESSED · BENTWHISTLE · TWISTEDKILT · TORNSTEAK -
SARC RT-RG Implementation And Progress [pdf]
A briefing from NSA/CSS Texas detailing the implementation status of the RT-RG signals intelligence capability at the Texas Cryptologic Center, focused on its operational use against Mexican drug cartel targets and border security missions as of August 2010.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
SIGDEV: Is It Time for a 'Target Reboot'? SIDtoday [pdf]
This SIDtoday article from March 2011 by an NSA Transnational and Strategic Partnerships SIGDEV analyst describing how a "target reboot" of Venezuela's state oil company PDVSA accidentally revealed that NSA had been collecting the company's internal communications all along — including over 10,000 employee contact profiles and 900 username/password combinations subsequently forwarded to TAO for network exploitation.
-
SIGINT Development Support II Program Management Review, 24 April 2013 (select slides) [pdf]
These selected slides briefly celebrate two NSA “success stories”: penetrating Pakistan’s Green Line infrastructure with SECONDDATE-enabled implants, and seizing country-wide leverage over Lebanon’s internet backbone through Ogero to siphon off Hezbollah-related data. It shows how U.S. intelligence treated supposedly inaccessible national networks as targets to be shaped, exploited, and folded into its global surveillance machine. See extra slide in "NSA Supply Chain Attack From PMR 4-24-13" https://theintercept.com/document/2019/01/24/nsa-supply-chain-attack-from-pmr-4-24-13/
Programs: MONSTERMIND · CHELSEABLUE · SECONDDATE · QUANTUM · REXKWONDO · STORMBREW · XKEYSCORE · MARINA · HAMMERCORE · HAMREX · CADENCE · HAMMERSTEIN · SSO -
SNIPs of SIGINT [pdf]
A monthly notes entry from June 2012 by an NSA analyst on exchange at DSD Australia, describing two CNA/CNE tool development projects — PITIEDFOOL, a Windows file system destruction suite that kills the MFT and volume shadow copies and was successfully tested inside FUZZYEBOLA, and PANT SPARTY, an OpenSSH daemon backdoor granting covert root access while suppressing log entries — alongside a briefing to the US Ambassador to Australia on CNA/CNE work and TAO collaboration.
-
Special Collection Service - Pacific SIGDEV Conference March 2011 [pdf]
This document is a TOP SECRET briefing describing the Special Collection Service (SCS)—its organizational structure, global posture and strategic partnerships—and how SCS leverages advanced SIGINT and cyber capabilities (microwave, cellular, satellite, VPN/Internet exploitation, tools like INTERQUAKE/Einstein/Castanet/Birdwatcher) from embassy/PoP sites to collect, analyze and support intelligence and covert operations. It also outlines SCS modernization goals (unified IT core, cloud/virtualization, expanded cyber presence), operational authorities and mission advantages for enabling both SIGINT and HUMINT activities. See also Spiegel's 2013 reporting based on the same presentation (back then they only published two slides from this presentation): https://www.spiegel.de/international/germany/cover-story-how-nsa-spied-on-merkel-cell-phone-from-berlin-embassy-a-930205.html
-
Special Source Operations - The Cryptologic Provider of Intelligence from Global High-Capacity Telecommunications Systems [pdf]
The document outlines NSA special source operations for accessing global telecommunications data, detailing corporate and foreign cable interception programs. It highlights the MUSCULAR program (DS-200B), a joint NSA–GCHQ operation in the UK that taps into high-capacity fiber-optic links to collect and process large volumes of data from private networks.
-
Special Source Operations corporate overview [pdf]
A classified NSA training presentation providing an in-depth operational overview of the FAIRVIEW program — the agency's largest corporate partner surveillance program — detailing its collection capabilities, legal authorities, TAO shaping operations, targeting tools, and productivity statistics, while revealing that BLARNEY/PRISM was the single most productive SSO program in 2012 with 806 serialized product reports.
Programs: FAIRVIEW · BLARNEY · PRISM · RAMPART-A · RAMPART-I · RAMPART-X · RAMPART-T · RAMPART-M · DGO · WINDSTOP · MYSTIC · PINWALE · XKEYSCORE · TURMOIL · STORMBREW · OAKSTAR · OCTAVE · UTT · CADENCE · COWBOY · YANKEE · MAINWAY · TOYGRIPPE · BLACKPEARL · TWISTEDPATH · NUCLEON · DISHFIRE · SPYDER · CARBONFURY · NATIVEFLORA · UNICORNSANDWICH · CROSSEYEDBEAR · SCORCHERSIX · TROPICTHUNDER · DARKTHUNDER · STEELFLAUTA · RAGTIME · SWEETSMACK2 · SOURSMACK2 · EVILOLIVE · SCALEABLE · FLEXIBLE · MONKEYROCKET · SHIFTINGSHADOW · ORANGECRUSH · YACHTSHOP · ORANGEBLOSSOM · SILVERZEPHYR · BLUEZEPHYR · COBALTFALCON · RAGTIME-A · RAGTIME-C · SSO · SURREY“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “The Wiretap Rooms: The NSA’s Hidden Spy Hubs in Eight U.S. Cities” - The Intercept ↗ (2018-06-25) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan -
SPINALTAP, Tracking Courier Use of Secure Digital Cards, and QUANTUMFALCON [pdf]
Three NSA presentations published as a single file. SPINALTAP, from Menwith Hill Station, extracts selectors from TAO, SFC and GCHQ endpoint accesses and translates them into XKEYSCORE fingerprints so that machines held by active operations can be recognised again in passive collection. Tracking Courier Use of Secure Digital Cards, from the NSA SIGINT Forensics Center, uses volume serial numbers and volume labels to identify SD cards and USB media that carry no USB controller, and reports identification information for 36 devices not seized during the UBL raid. QUANTUMFALCON summarises selector activity to triage targets for QUANTUM operations: see the Der Spiegel article The Digital Arms Race: NSA Preps America for Future Battle, 17 January 2015.
Programs: AARDVARKSTAKE · ABSOLINEDELTA · ACRIDMINI · AFTERBOOTSOLE · AFTERCLIFFDIVE · AFTERDOGHOUSE · AFTERGASSTATION · AFTERLASTTEAM · AFTERRICHGEAR · AFTERSHORTRUN · AFTERTANKERTRUCK · AFTERTREEFORM · AFTERWAYBACK · AFTERWINDBLOWN · AFTERYARDARM · ANCIENTBREW · APACHERIVER · ARMOREDCONDOR · ASDF · ATOMICCANNON · ATOMICFIREBALL · ATOMICFOG · ATOMICMONKEY · ATOMICPUNCH · ATOMICSTRIKE · AZTECTOMB · BACKSNARF · BEDOUINSTRIKE · BEEFCAKE · BLACK ALCHEMY · BLACKAMETHYST · BLACKMESA · BLOODDIAMOND · BROKENTHOUGHT · BULLETTOOTH · CAFFEINECRASH · CHOCOLATESHIP · COBALTGUPPY · COCOAMELTDOWN · CRISPWARE · CRYPTICSENTINEL · CUDDLYBADGER · CYGNUSOLOR · DANDERSPRITZ · DARKFIRE · DARKHELMET · DARKINTENT · DARKRAVEN · DARKRAZOR · DARKSCREW · DARKTHUNDER · DEADDRUMMER · DEPUTYSHIP · DETASSELJANICE · DIRTDIVER · DISTORTAFFECT · DOUBLETAP · DRINKMINT · DRINKMINTAA · DRUMBEAT · EDITIONHAZE · EFFABLELAMBDA · ELECTRONSWORD · EMPTYMOCHA · FIREBRUSH · FIREEATER · FIRESWAMP · FOXACID · FOXBASE · FRANTICDANCER · FREEACIDRAIN · FREEAIRFARE · FREEARCADEZONE · FREEBACKGAMMON · FREEBADFIBER · FREEBADRENT · FREEBALLROOM · FREEBATTLEZONE · FREEBEACHTREE · FREEBIGBOSS · FREEBITTERCLOUD · FREEBLACKCLOUD · FREEBLOODYWOLF · FREEBLOWNTURBO · FREEBLUEMAT · FREEBRASSBRUSH · FREEBUTTERCLOUD · UTT · FREECANALLOCK · FREECANESUGAR · FREECATBOX · FREECEMENTBLOCK · FREECHERRYCOLA · FREECHESSBOARD · FREECLEARTAPE · FREECOLDTEA · FREECORNHUSK · FREECORNMAZE · FREECREEKMOOR · FREECRUSHEDDISK · FREEDARKSUIT · FREEDATALOSS · FREEDEADBATTERY · FREEDETOURSIGN · FREEDIRTYTRICK · FREEDISCOVERY · FREEDISKBRAKE · FREEDOGCRATE · FREEDOMECUPOLA · FREEDOVETAIL · FREEEMUFARM · FREEENERGYTAX · FREEFAMILYTIE · FREEFASTCAR · FREEFIBERBOARD · FREEFILEDELETE · FREEFLATFIBER · FREEFLOWCHART · FREEFLOWERPEOPLE · FREEFRIEZEFRESCO · FREEGEMSTONE · FREEGLASSTUBE · FREEGLUESTRIP · FREEHAVEFUN · FREEHOMEBASE · FREEHOOKHANDLE · FREEHOOPDREAM · FREEJETFUEL · FREEKIDPOOL · FREEKINGSPAWN · FREEKNOCKOUT · FREELANDLINE · FREELEADSHOT · FREELEADSINGER · FREELIFERAFT · FREELIKESAME · FREELINEDOWN · FREELOLLYPOP · FREEMARBLEBASIN · FREEMETALCRATE · FREEMETALFILE · FREEMETALSHARD · FREEMINETUNNEL · FREEMINTJELLY · FREENAVYBLUE · FREENIGHTTRAIN · FREEOBLIQUECASE · FREEOILLEAK · FREEOILPAINT · FREEOLDBIKE · FREEOUTRUN · FREEPAINTBALL · FREEPICKLEBRINE · FREEPINEPLANK · FREEPLASTICCASE · FREEPONGPLAYER · FREEPOSTMARK · FREEPOWERFAILURE · FREEPUFFYCLOUD · FREEPULLCHAIN · FREERAINCLOUD · FREERAVENTICKET · FREEREDBEER · FREEREDERASER · FREEREDMARKER · FREEREDSHIRT · FREEREDSTAIN · FREERIDEAROUND · FREERIGHTWHALE · FREERIPPINGBLADE · FREEROCKSONG · FREESAFEKEY · FREESALTTRUCK · FREESASHCORD · FREESCHOOLLOCKER · FREESCREENDOOR · FREESEADADDY · FREESHORTCARD · FREESHORTPASS · FREESINEWAVE · FREESLOWFAST · FREESMALLSPACE · FREESMOKESCREEN · FREESNOWCLOUD · FREESNOWSHOVEL · FREESPACEFLIGHT · FREESPEEDTRAP · FREESTATEWARD · FREESTONESHIP · FREESTORAGEROOM · FREETANKSTAND · FREETESTSHEET · FREETHUNDERCLOUD · FREETICKETBOOTH · FREETIMELEGEND · FREETIMESHARE · FREETINYTANK · FREETRICKYKICK · FREETROUTSTREAM · FREETRUEPINBALL · FREETWINBEE · FREEVINYLMESH · FREEWARRIORPAINT · FREEWATERBED · FREEWATERGLASS · FREEWATERTANK · FREEWATERTOWER · FREEWAVECREST · FREEWAYPOINT · FREEWHEELCOVER · FREEWHEELNUT · FREEWINDCLOUD · FREEWINDSHEAR · FREEWOODENSTICK · FURRYEWOK · GHOSTMACHINE · GMPLACE · GOODMONKEY · HAMMERBROTHERS · HASTYCOBRA · HORSEWRAP · ICEBLOCK · IMPUREHOLSTER · INDEPENDENCEPIE · INQUIRY · JAVAFRESCO · JEALOUSJOKER · JEEPFLEA · JEEPFLEAMARKET · JOLLYROGER · KIDSHIPAA · KOOPATROOPA · KUKRISTEEL · LIQUIDSTEEL · LUTEUSASTRO · MAGNUMOPUS · MAGNUMOPUSCC · MARINA · MAXRANKLE · MICEFUR · MIDNIGHTSCORPION · MILKSTEAK · MIRACLEMAX · MUSHROOMKINGDOM · NAPALAN · NATIVEFLORA · OBSCUREBLAZE · OFFICELINEBACKER · OFFICEQUARTERBACK · OPTIMUSPRIME · PARLAYBUFFET · PHANTOMSTARFISH · PLUMREVOLVER · PRETZELDOG · QBISCUIT · QDIRK · QUANTUM · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUMFALCON · REACTOR · ROLLEDHAT · SANDPALACE · SCARFSLOOP · SHADYNINJA · SHAKEWEIGHT · SHATTEREDSHIELD · SILENTTONGUES · SILLYBUNNY · SILVERJUMP · SKYJACKBRAD · SLYNINJA · SLYSNOW · SLYWIZARD · SNAPKEY · SPARTANFURY · SPIKEYFARM · SPINALTAP · STARPROC · STEELSKY · STEELSKYDELTA · STEELSKYECHO · STEELSKYFOXTROT · STEELSKYGOLF · STONEHENGE · STRAITLACED · SWITCHDOWN · SWITCHDOWNIRAW · SWITCHDOWNIRBR · SWITCHDOWNIRCD · THIEVESQUARTER · TOADYTEAL · TOTALDAGGER · TOXICSNOW · TROPICALSTORM · UMBRAGESPIDER · UNITEDRAKE · UPPERMUTANT · VALIDATOR · VEILEDMAGIC · WATERCASKET · WATERWINGS · WAXCHIP · WICKEDAMP · WILDCHOCOBO · WITHEREDFRUIT · WOLFACID · WOLFACIDANISE · WOLFACIDARGON · WOLFACIDBARIUM · WOLFACIDCHILI · WOLFACIDIODINE · WOLFACIDIRON · WOLFACIDJUPITER · WOLFACIDLEAD · WOLFACIDPRECIOUS · WOLFACIDTIN · WOLFACIDURANIUM · WOLFACIDZINC · XKEYSCORE · YELLOWFAN · MUSCULAR · INCENSER · DANCINGOASIS · MAPREDUCE“Documents Reveal Top NSA Hacking Unit” - Der Spiegel ↗ (2013-12-29) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Appelbaum, Jacob · Poitras, Laura · Rosenbach, Marcel · Stöcker, Christian · Schindler, Jörg · Stark, Holger · Gallagher, Ryan · Greenwald, Glenn · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael