Program: SSO 105 documents
Search documents matching “SSO” →Codenames and programs recorded for each document.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
New FAA702 Certification in the Works - Cyber Threat [pdf]
A 23 March 2012 SSO article on a draft FAA 702 certification for cyber threats. It would let analysts task selectors tied to malicious cyber activity without attributing them to a foreign government or terrorist group, and would codify tasking of IP addresses and code strings through PRISM and the upstream accesses.
-
New Skype Stored Comms Capability For PRISM [pdf]
An SSO item on PRISM's new Skype stored-communications capability — buddy lists, credit card details, call data records and account information — with roughly 2,000 Skype selectors sent for FBI adjudication on 29 March 2013 and over 2,800 reports issued from PRISM Skype collection since April 2011.
-
NSA inspector general report on email and internet data collection under Stellar Wind, 24 March 2009 [Working Draft] [pdf]
This 2009 NSA Inspector General draft report details the origins and legal framework of the President’s Surveillance Program (PSP), launched after 9/11 to bypass FISA limits and authorize bulk interception of internet and telephony content and metadata, including communications with one end inside the U.S. It reveals how NSA, with White House backing, expanded surveillance authority to cover “collection gaps” that existing law didn’t allow, effectively legalizing large-scale warrantless spying under a secret presidential directive.
People: Bush, George W. · Hayden, Michael · Tenet, George · Gonzales, Alberto R. · Addington, David S. · Graham, Robert · Deitz, Robert L. · Shelby, Richard · Pelosi, Nancy · Cheney, Dick · Libby, I. Lewis · Lamberth, Royce · Inouye, Daniel · Levin, Daniel · Stevens, Theodore · Kollar-Kotelly, Colleen · Rockefeller, Jay · Alexander, Keith B. · Potenza, Vito -
NSA QUANTUM Tasking Techniques for the R&T Analyst [pdf]
A classified NSA training presentation, prepared by Booz Allen Hamilton, walking analysts step-by-step through how to secretly hack into a target's computer by hijacking their everyday internet traffic — exploiting platforms like Yahoo and Facebook to silently inject malware without the target's knowledge.
Programs: QUANTUM · QUANTUMTHEORY · QUANTUMNATION · VALIDATOR · COMMONDEER · SEASONEDMOTH · SMOTH · MARINA · FOXACID · RADIUS · QUANTUMBISCUIT · ALTEREGO · DOGCOLLAR · FOREMAN · ANCHORY · BRUTUS · REACTOR · SPARKLEPONY · WINDCHASER · YACHTSHOP · MUTANTBROTH · FOXSEARCH · WHITELIST · SSO · PSC -
NWP NSA [pdf]
A January 2011 internal NSA newsletter from Yakima Research Station (YRS) covering the station's early history as the West Coast ECHELON/FROSTING satellite interception facility established in 1966 to collect INTELSAT communications, and its more recent expansion into cloud-based cyber threat discovery using FORNSAT and Special Source Operations data.
Programs: EARLYBIRD · FROSTING · TRANSIENT · ECHELON · JACKKNIFE · SAFEGUARD · STEAMS · CYBERQUEST · GINPENNANT · RUMBUCKET · CROSSBONES · SSO -
OAKSTAR Travel Hanbook: A Guide for Traveling [pdf]
This document is a NSA OAKSTAR Travel Handbook, providing detailed guidance for personnel traveling on OAKSTAR-related missions, including MONKEYROCKET. It covers travel preparation, clearance requirements, coordination with partner organizations, operational security measures, conduct during visits, reporting obligations, and expense documentation to ensure sensitive intelligence operations are protected while engaging with private-sector partners.
Programs: OAKSTAR · STEELKNIGHT · SILVERZEPHYR · YACHTSTOP · SHIFTINGSHADOW · MONKEYROCKET · COBALTFALCON · BLUEZEPHYR · ORANGECRUSH · ORANGEBLOSSOM · PRIMECANE · TRANSPORTORO · THUNDERLISLAND · WHIPGENIE · SSO · THUNDERISLAND · YACHTSHOP -
ORANGECRUSH, part of the OAKSTAR program [pdf]
An SSO item reporting that ORANGECRUSH — the OAKSTAR access at a third-party partner site in Poland, known to the Poles only as BUFFALOGREEN — began forwarding metadata to NSA on 3 March and content on 25 March, with collection shared to Second Parties through TICKETWINDOW.
-
Phone Number Extractor [pdf]
A top secret XKEYSCORE training document from October 2009 describing the Phone Number Extractor capability, which automatically identifies and extracts telephone numbers from intercepted internet traffic including website content, email signature blocks, HTTP GET requests from mobile devices, HTTP POST submissions, and converged DNR/DNI collection — with operational examples targeting Iran, Lebanon, and Pakistan.
-
Presentation on the spying program PRISM and ECC's participation [pdf]
This presentation provides statistics on the PRISM surveillance program, detailing intelligence reporting and target tasking across various NSA units and partners from 2011 to 2013. The data reveals that while not the top producer by volume, the European Cryptologic Center (ECC) was the most proportionally reliant on PRISM, which constituted over half of its intelligence output.
-
PRESTON Business Processes [pdf]
The PRESTON Business Processes document outlines GCHQ’s internal workflows for authorizing, enabling, managing, and terminating communications interception, as well as producing intelligence from intercepted data. It defines the roles, responsibilities, and technical processes that support lawful interception operations within the PRESTON system.
-
PRISM Olympic Option [pdf]
A May 2012 NSA operational highlight revealing that Britain's GCHQ was given access to the NSA's PRISM surveillance system during the London Olympics, with 100 trained British operatives secretly monitoring 256 targets and intercepting over 11,000 communications in a single week.
-
PRISM planning slide (PRISM briefing 1) [pdf]
A PRISM slide headed 'What's Next': plans to add Dropbox as a PRISM provider, add a cyber threat certification, expand collection from existing providers, and change the UTT tasking system to allow phone-number tasking.
-
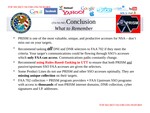
PRISM tasking slide (PRISM briefing 2) [pdf]
A PRISM slide headed 'Conclusion: What to Remember'. It says PRISM is among the most valuable NSA accesses, recommends tasking all DNI and DNR selectors to FAA 702 where they meet the criteria, and recommends Rules-Based Tasking in UTT so that PRISM and upstream SSO accesses both get the selectors.
-
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
PRISM/US-984XN Overview [pdf]
Blurry screengrabs from the "PRISM/US-984XN Overview" slide deck shown on the Fantástico O Globo broadcast. This document contains slides that are not incldued in the slides published by The Washington Post, The Guardian, Le Monde, and others.
-
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
RAMPART-A Project Overview [pdf]
This document is a 2010 project overview of RAMPART-A, a highly unconventional NSA special access program dedicated to tapping high-capacity international fiber-optic cables at global "congestion points." Through clandestine bilateral partnerships, the NSA installs U.S. equipment on foreign soil to intercept massive volumes of transit data, providing the agency with a unique vantage point that covers virtually every country in the world.
Programs: RAMPART-A · RAMPART-T · SMOKYSINK · AZUREPHOENIX · SPINNERET · TRANQUIL · MOONLIGHTPATH · FIREBIRD · FALCONSTRIKE · DULCIMER · REDHARVEST · FLASHMARK · CONDORSPEAK · TURMOIL · SSO“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura · Jensen, Kristian -
SHELLTRUMPET Processes its One Trillionth Metadata Record [pdf]
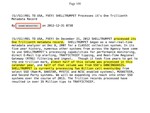
An SSO news item announcing that SHELLTRUMPET processed its one-trillionth metadata record on 21 December 2012 — almost half of that volume in 2012 alone — feeding TRAFFICTHIEF tipping and Real-Time Regional Gateway filtering from CLASSIC, DANCINGOASIS, RAMPART-M, OAKSTAR, MYSTIC, NCSC, MUSKETEER and Second Party systems.
Programs: SHELLTRUMPET · CLASSIC · TRAFFICTHIEF · RTRG · SSO · DANCINGOASIS · RAMPART-M · OAKSTAR · MYSTIC · NCSC · MUSKETEER -
SID Oversight and Compliance [pdf]
Signals Intelligence Directorate (SID) oversight and compliance. A 2012 quarterly audit of the NSA's surveillance activities, which describes 865 violations by the NSA of the surveillance laws and its internal rules and regulations.
-
SIGINT Development Support II Program Management Review, 24 April 2013 (select slides) [pdf]
These selected slides briefly celebrate two NSA “success stories”: penetrating Pakistan’s Green Line infrastructure with SECONDDATE-enabled implants, and seizing country-wide leverage over Lebanon’s internet backbone through Ogero to siphon off Hezbollah-related data. It shows how U.S. intelligence treated supposedly inaccessible national networks as targets to be shaped, exploited, and folded into its global surveillance machine. See extra slide in "NSA Supply Chain Attack From PMR 4-24-13" https://theintercept.com/document/2019/01/24/nsa-supply-chain-attack-from-pmr-4-24-13/
Programs: MONSTERMIND · CHELSEABLUE · SECONDDATE · QUANTUM · REXKWONDO · STORMBREW · XKEYSCORE · MARINA · HAMMERCORE · HAMREX · CADENCE · HAMMERSTEIN · SSO