Classification: TOP SECRET 823 documents
Search documents matching “TOP SECRET” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (14 years)
By published date (9 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
DGSE and ANSSI Delegation to NSA (April 2013), cyberattacks [pdf]
This Top Secret NSA visit précis details the April 12, 2013 meeting between senior French cyber officials Bernard Barbier (DGSE) and Patrick Pailloux (ANSSI) and NSA leadership to discuss and seek U.S. assistance in attributing May 2012 cyberattacks on the French Presidential network. The document outlines the visit agenda, background tensions over French media accusations of U.S. involvement, and NSA’s plan to emphasize cyber defense cooperation while carefully navigating potential diplomatic sensitivities.
-
DIA - Swimming Upstream in the SIGINT System SIDtoday [pdf]
NSA collects “medical SIGINT” from the communications of NGOs and treaty-monitoring organizations and is collaborating with the DIA’s Armed Forces Medical Intelligence Center at the Army’s bioweapons research facility at Fort Detrick for expertise in epidemiology.
The Intercept ↗ (2016-08-10) -
Did You Know that NSA Has an Arctic Presence? SIDtoday [pdf]
This SIDtoday document describes the NSA's Arctic operations, highlighting its Alaska Mission Operations Center (AMOC) at Point Barrow, Alaska, which monitors Russian military activity in the Arctic. The facility supports U.S. and Canadian defense efforts, tracks Russian air movements, and is involved in upgrades and collaborations with Arctic partners to address emerging intelligence challenges in the region.
-
Digital Network Exploitation (DNE), Digital Network Intelligence (DNI) and Computer Network Exploitation (CNE) SIDtoday [pdf]
Explanation of the differences between Digital Network Exploitation, Digital Network Intelligence, and Computer Network Exploitation: DNE is extracting intelligence from a device on the global network; DNI is the intelligence produced by DNE; and CNE is hacking end-point devices (mentions “subtly weakening encryption”). Article acknowledges that “our targets communications are increasingly buried by millions of non-target communications.”
The Intercept ↗ (2016-08-10) -
Discovery SIGINT Targeting Scenarios and Compliance [pdf]
This document is a top-secret NSA guidance manual detailing SIGINT targeting scenarios, compliance procedures, and legal guidance for querying foreign actors, malware, and potentially U.S.-linked systems, including considerations for minimizing incidental collection of U.S. persons’ communications. It outlines specific rules, approvals, and exceptions for using SIGINT tools, foreign intelligence tasks, and cases involving ambiguous or dual-use selectors like WikiLeaks, The Pirate Bay, and foreign actors operating through U.S. infrastructure.
-
Dispatch from NIST Baghdad: Life in the Palace SIDtoday [pdf]
Report from NSA staff on duty with the Coalition Provisional Authority in Iraq.
Programs: MUSKETEERPeople: Bremer, PaulThe Intercept ↗ (2016-08-10) -
DNE, DNI, and CNE (repost) SIDtoday [pdf]
(Repost) Explanation of the differences between Digital Network Exploitation, Digital Network Intelligence, and Computer Network Exploitation: DNE is extracting intelligence from a device on the global network; DNI is the intelligence produced by DNE; and CNE is hacking end-point devices (mentions “subtly weakening encryption”). Article acknowledges that “our targets communications are increasingly buried by millions of non-target communications.”
The Intercept ↗ (2016-08-10) -
DNI101 [pdf]
This TOP SECRET training guide, "DNI 101," provides a workflow for Digital Network Intelligence analysts on how to investigate a target's email address, detailing the specific tools, databases, and methodology used, and stressing the critical difference between initial open-source/classified research and the active "targeting" of raw SIGINT repositories like XKEYSCORE, PINWALE, and MARINA.
Programs: NKB · FOXTRAIL · FOREMAN · PINWALE · LIONHEART · XKEYSCORE · DISHFIRE · MARINA · MECWEB · MAINWAY · TRAFFICTHIEF · MAUI · ANCHORY · M3 · INTELLINK · HOMEBASE · PROTON · UTT · CADENCE · SPEEDBUMP · TUNINGFORK · MASTERSHAKE · BLACKPEARL · JACKSPARROW · ROADBED · STORYDUTY · LIONROAR · DOPHONE · UIS -
Do's and Don'ts of Deploying SIDtoday [pdf]
A tongue-in-cheek guide to civilian intelligence analysts deploying in support of military units. The advice includes not discharging weapons, addressing personnel correctly, and not hoarding information.
The Intercept ↗ (2018-08-15) -
Do's and Don'ts of Deploying (repost) SIDtoday [pdf]
(Repost.) A tongue-in-cheek guide to civilian Intelligence Analysts deploying in support of military units. The advice includes not discharging weapons, addressing personnel correctly and not hoarding information.
The Intercept ↗ (2019-05-29) -
Docked in Haiti, Collecting SIGINT SIDtoday [pdf]
The author took part in a U.S. Navy humanitarian mission to Haiti after the devastating Hurricane Jeanne in September 2004. He provided linguistic support and assisted with recovering network collection, including from the United Nations Stabilization Mission in Haiti, the Haitian National Police, and the Haitian interim government.
The Intercept ↗ (2017-09-13) -
Doing SIGINT in Pakistan SIDtoday [pdf]
A SID intern from the Pakistan Branch was deployed to work at Special Collection Service sites in Islamabad and Lahore. He played a part in tracking a terrorist target captured in August 2004 and worked on leads related to threats on the U.S. Embassy.
The Intercept ↗ (2017-04-24) -
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
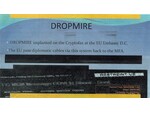
DROPMIRE on the Cryptofax at the EU Embassy D.C. [pdf]
This document reveals that the NSA secretly targeted EU diplomatic communications through a program called DROPMIRE, which involved placing surveillance implants on encrypted fax machines at the EU Embassy in Washington, D.C. This operation was part of a broader effort to spy on 38 foreign embassies and missions—including allies such as France, Italy, and Greece—to gain inside knowledge of policy debates and diplomatic positions.
Programs: DROPMIRE -
DSD Delves into Reverse Engineering SIDtoday [pdf]
A Signals Intelligence Directorate mathematician deployed to Australia collaborated with Defence Signals Directorate staff to establish a formal capacity to reverse-engineer communications systems for exploitation.
The Intercept ↗ (2017-09-13) -
EAGLEVIEW -- A Data Processing Tool for GSM Cellular Networks SIDtoday [pdf]
A system called "EAGLEVIEW" helps analysts map out GSM cellular phone networks. The system takes information collected in the field and plots out network coverage.
The Intercept ↗ (2017-09-13) -
ECI WHIPGENIE Classification Guide [pdf]
A 2004 NSA classification guide for ECI WHIPGENIE, covering the agency's Special Source Operations relationships with US corporate partners for cable collection and domestic wire access, including FISA-warranted collection and FBI-assisted compelled and cooperative partnerships.
Programs: WHIPGENIE · FAIRVIEW · STORMBREW · BLARNEY · POWERPLANT · TUMBRIL · WEALTHYCLUSTER · RAGTIME · PLUS · YELLOWSTONE · SSO -
Efforts Against Virtual Private Networks Bear Fruit SIDtoday [pdf]
Recent progress in exploiting Virtual Private Networks has resulted in access to “hundreds” of secure links, including Al Jazeera’s internal communications.
The Intercept ↗ (2018-08-15) -
Email Address vs User Activity [pdf]
This 2009 NSA training presentation explains how to use the XKEYSCORE system to search raw SIGINT, detailing the differences between the "Email Address" query, which finds email addresses in full content, and the more flexible "User Activity" query, which can search for selectors like cookies, usernames, and phone numbers.
“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
Embedded with USSOCOM: NSA Reps Provide Direct Analytic Support SIDtoday [pdf]
The NSA helped U.S. special forces “discover a vast and disparate network of Iranian agents in Iraq serving the Iranian Ministry of Intelligence ... or the Islamic Revolutionary Guards Corps.” Analysts embedded with special forces also help to find enemy safe houses, “ratlines,” and VIP facilities.
People: Brown, Bryan D.The Intercept ↗ (2018-08-15)