Classification: COMINT 287 documents
Search documents matching “COMINT” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (13 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
CSEC Cyber Threat Capabilities [pdf]
This document details CSEC’s full-spectrum cyber operations architecture, integrating SIGINT and IT Security to conduct both defensive and offensive activities under the guise of “information superiority.” While early sections emphasize detection, anomaly analysis, and collaboration with Five Eyes partners, later portions reveal active measures including network infiltration (implant deployment), command-and-control tracking, traffic manipulation and redirection, DNS interference, and potential disruption or deception operations—illustrating CSEC’s capacity not only to defend Canadian networks but also to surveil, exploit, and influence foreign and domestic digital infrastructure.
Programs: EONBLUE · CYBERDMZ · SEEDSPHERE · PHOTONICPRISM · SPECIALSOURCE · SUPERDRAKE · DARKSPACE · QUANTUM · MANDATE · STREAMING SENTRY · SSO · TKB · COVENANT -
CSEC Cyber Threat Detection [pdf]
This document details the Communications Security Establishment’s (CSEC) cyber threat detection and intelligence infrastructure, including systems like EONBLUE, CROSSBOW, CRUCIBLE, and LODESTONE, which enable passive monitoring, anomaly detection, and botnet identification through metadata and deep packet inspection. It outlines how CSEC integrates SIGINT, cryptanalysis, and network forensics to detect and mitigate cyber intrusions using both SIGINT and domestic sensors, while collaborating with Five Eyes partners to enhance Canada’s cyber defense and situational awareness. The presentation is duplicated from page 7 onwards - one of the duplicated slide has internal CSE comments.
Programs: EONBLUE · SPECIALSOURCE · WARRANTEDACCESS · COVENANT · SEEDSPHERE · DIESELRATTLE · SIENNABLUE · DOWNGRADE · CROSSBOW · CRUCIBLE · LODESTONE -
CSEC SIGINT Cyber Discovery: Summary of the current effort [pdf]
This document provides a overview of the Communications Security Establishment Canada (CSEC) cyber operations, detailing its SIGINT, CNE (Computer Network Exploitation), and cyber counterintelligence programs, including tools like WARRIORPRIDE, REPLICANTFARM, and EONBLUE for threat detection, anomaly discovery, and metadata production. It outlines operational procedures, analytic methodologies, and collaborative frameworks with domestic and Five Eyes partners for sharing intelligence, tipping/cueing, and integrating cyber and traditional counterintelligence efforts.
Programs: REPLICANTFARM · SLIPSTREAM · WARRIORPRIDE · DAREDEVIL · CHORDFLIER · NAMEDROPPER · WORMWOOD · OBELIX · SHEPHERD · CARBON · REGBACKUP · DOGHOUSE · WALKER · ALOOFNESS · BLAZINGANGEL · TINYWEB · QUIVERINGSQUAB · WINDO · DIESELRATTLE · WIDOWKEY · CIVETCAT · WINBEE · SSLINST · PULLEDPORK · EONBLUE · SNIFFLE · QUANTUM · XKEYSCORE · HALTERHITCH · FASTFLUX · DEADSEA · NSPACES · PPF · SSO · TKB“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan -
Cyber Defence Operations Legal Policy [pdf]
GCHQ's internal wiki laying out the legal plumbing for its Cyber Defence Operations (formerly NDIST)—detailing warrant types (RIPA, ISA, CNE), data retention schedules, targeting rules for UK/Five Eyes infrastructure, XKEYSCORE query protocols, and the bureaucratic hoops analysts must jump through to search attacker IPs, fingerprint UK networks, and share malware intelligence without tripping over location/nationality safeguards or commercial sensitivities.
Programs: JTRIG · SPAY · GORDIANKNOT · CHORDAL · DISCOVER · EVENTS · CASPORT · XKEYSCORE · CONTENT CLOUD · SQUEAL · MIRAGE · MUTANTBROTH · ANXIOUS · HALTERHITCH · BROADOAK · DONKEYKONG · ZOOL · PALANTIR · OVERLINK · RT · GATEKEEPER · IRONHAND · HARUSPEX · B3M · LOOKINGGLASS · GOLDENEYE · BLAZINGSADDLES · MOONRAKER · TRITON -
Cyber Integration [pdf]
The leaked 2012 GCHQ JTRIG presentation detail a wide range of offensive cyber and influence operations designed to “deny, disrupt, degrade, and deceive” targets, including hackers, foreign governments, companies, and individuals. Tactics include hacking, DDOS attacks, disinformation, honey traps, credential harvesting, and psychological operations, reflecting a shift from traditional surveillance to active disruption and manipulation campaigns.
“Exclusive: Snowden Docs Show British Spies Used Sex and 'Dirty Tricks'” - NBC News ↗ (2014-02-07) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Cole, Matthew · Esposito, Richard · Schone, Mark · Greenwald, Glenn -
Data Stored in BLACK HOLE [pdf]
This document describes BLACK HOLE, a TOP SECRET data repository that stores approximately 200GB per day of internet activity "events" such as webmail, chat, and browsing. It details the system's various datamarts, including MUTANT BROTH and KARMA POLICE, which collectively hold terabytes of data for intelligence analysis.
Programs: BLACKHOLE · B13B · MUTANTBROTH · KARMAPOLICE · MEMORYHOLE · AUTOASSOC · SOCIALANIMAL · HRMAP · INFINITEMONKEYS -
DEFIANTWARRIOR and the NSA's Use of Bots [pdf]
This TOP SECRET NSA presentation from 2010 documents the DEFIANTWARRIOR effort to identify, seize, and operate botnets using SIGINT-enabled infrastructure, detailing both early failures and subsequent operational successes. The document reveals how bot herding was integrated into broader offensive cyber and intelligence collection strategies across the Five Eyes.
Programs: DEFIANTWARRIOR · OLYMPUS · UNITEDRAKE · TURBULENCE · QUANTUMBOT · TURMOIL · TURBINE · SNIPERS · XKEYSCORE · INCENSER · STELLABLUE · SMOKYSINK · STOVEPIPES · ISLANDTRANSPORT · FESTIVEWRAPPER · FREEFLOW · PRESSUREWAVE · HANGARSURPLUS · SURPLUSHANGER · WAITAUTO · DEEPFRIEDPIG · SEAGULLFARO · COLOSSUS · STORMPIG · YELLPIG · PASTEPIG · SHOUTPIG · ZORPIG · MAILORDER · TREASUREMAP · MARINA · WARNVOLCANO · STRAITBIZARRE · BOTINSTANCES · PUZZLECUBE · SEEKER · SURPLUSHANGAR -
DNI101 [pdf]
This TOP SECRET training guide, "DNI 101," provides a workflow for Digital Network Intelligence analysts on how to investigate a target's email address, detailing the specific tools, databases, and methodology used, and stressing the critical difference between initial open-source/classified research and the active "targeting" of raw SIGINT repositories like XKEYSCORE, PINWALE, and MARINA.
Programs: NKB · FOXTRAIL · FOREMAN · PINWALE · LIONHEART · XKEYSCORE · DISHFIRE · MARINA · MECWEB · MAINWAY · TRAFFICTHIEF · MAUI · ANCHORY · M3 · INTELLINK · HOMEBASE · PROTON · UTT · CADENCE · SPEEDBUMP · TUNINGFORK · MASTERSHAKE · BLACKPEARL · JACKSPARROW · ROADBED · STORYDUTY · LIONROAR · DOPHONE · UIS -
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
ECI WHIPGENIE Classification Guide [pdf]
A 2004 NSA classification guide for ECI WHIPGENIE, covering the agency's Special Source Operations relationships with US corporate partners for cable collection and domestic wire access, including FISA-warranted collection and FBI-assisted compelled and cooperative partnerships.
Programs: WHIPGENIE · FAIRVIEW · STORMBREW · BLARNEY · POWERPLANT · TUMBRIL · WEALTHYCLUSTER · RAGTIME · PLUS · YELLOWSTONE · SSO -
Email Address vs User Activity [pdf]
This 2009 NSA training presentation explains how to use the XKEYSCORE system to search raw SIGINT, detailing the differences between the "Email Address" query, which finds email addresses in full content, and the more flexible "User Activity" query, which can search for selectors like cookies, usernames, and phone numbers.
“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
EP-3E Collision: Cryptologic Damage Assessment and Incident Review [pdf]
A joint US Navy and NSA report from July 2001, prepared three months after a US spy plane was forced to land in China, assessing how far surveillance sources and methods were compromised and reviewing the emergency destruction that failed to prevent it. Damage to tactical SIGINT against the PRC is rated medium and overall SIGINT damage low, with the greatest loss the LUNCHBOX PROFORMA processor and MARTES signals analysis tools; COMSEC damage is rated low because keying material was superseded within 15 hours.
Programs: LUNCHBOX · MARTES · NICKELBACK · SENSOR PACER · PROFORMA · HULTEC · STRUM · TEXTA · RASIN · CRITIC · KLIEGLIGHT · XBIT · BLACKMAGIC · NOIWON · ZIRCON · MIDB · EOB-LITE · NIMROD · ARIEL · COBRA BALL · COMBAT SENT · RIVET JOINT · SEABOOT · SETTEE · KAMPUS · DRUID · RORIPA · MARKHAM · FOREJUDGE · SAM HEARTBURN · NOVELETTE · RSBN · BEGGAR HAWK · BEGGAR SHADOW · CAPSULE JACK · DISTANT WIND · DISTANT SENT · CHILING · RIBBED · UNACCENTED · SLIPSTICK · SIERRA ONEPeople: Meals, Charlie -
Event (SIGINT) [pdf]
5 p.This document explains that within GCHQ and NSA SIGINT operations, an “Event” refers to metadata about observable communications or user actions rather than message content, categorized into types like Communications, Presence, Social, and Geo-reference Events. These events are collected, stored in various databases, and analyzed through convergence and correlation processes, with standardized formats defined by Interface Control Documents such as INTERSTELLAR DUST (IDUST) and Actor Action (AA).
Programs: INTERSTELLAR DUST · HAUSTORIUM · SOCIAL ANTHROPOID · ACTOR-ACTION · SAMREF · GEOFUSION · HARD ASSOC · SALAMANCA · ASSOCIATION · BANYAN · MAINWAY · FASCIA · CULTWEAVE II · VOICESAIL · TEEDALE · PILBEAM · MUTANTBROTH · AUTOASSOC · MARBLEDGECKO · KARMAPOLICE · HRMAP · MEMORYHOLE · INFINITEMONKEYS · SOCIALANIMAL · AUTOTDI · SAMUELPEPYS · Mobile Applications Project · NGE · PPF · SLR -
Excerpt of May 2008 NSA Afghanistan Dataflow Analysis [pdf]
The document outlines how the NSA’s Real Time Regional Gateway (RT-RG) in Afghanistan progressively expanded from late 2007 through 2008 to ingest massive amounts of GSM, VHF, HF, and telephony metadata from dozens of locations across Afghanistan, supplemented by third-party “dirtbox” collection from allied nations such as the Netherlands, Denmark, Norway, Germany, and Spain. It details the specific collection sites, data types, and timelines (SPIN 9, 10, 11, etc.), illustrating how partner contributions and multiple signals sources fed into the RT-RG system to enable real-time intelligence.
Programs: FOURCORNERS · FORTRESS · WARRIOR · ECHIDNA · CASSIEOPIA · KARUS · SOUNDER · SNICK · TEMPOWOLFE · CALYPSO · TATTERAN · AIRBORNE · LEAVEBEHIND · UDEAUS · NELEUS · CROSSHAIR · SSO · DRT · RIVET JOINT · VOICESAIL“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
Expeditionary Access Operations: NSA’s Close Access Network Exploitation Program [pdf]
The document describes NSA/TAO’s Expeditionary Access Operations (EAO, S3283), a deployable arm that conducts human-enabled Close Access Network Exploitation (CNE) worldwide—using techniques from physical implants and gifted/compromised laptops to wireless injection tools (e.g., BLINDDATE, NITESTAND) and Wi-Fi geolocation—to support tactical customers like SOCOM, DIA, and task forces in Afghanistan, Iraq, and elsewhere. It details organization, tools, operational theaters (Bagram, Kabul, Kandahar, Stuttgart, Texas, etc.), specific operations (IRONPERSISTENCE, CLIMBINGSHIRT), and plans to formalize partnerships with USCYBERCOM and expand expeditionary CANO capabilities.
Programs: NITESTAND · HAPPY HOUR · BADDECISION · MASTERSHAKE · IRONPERSISTENCE · CLIMBINGSHIRT · BLINDDATE -
FAA702 comms memo [pdf]
This document details NSA's response to concerns raised by the FISA Court over the collection of non-targeted data in FAA-702 upstream collection. To mitigate the risk of continued acquisition, NSA is implementing temporary measures, including cautionary banners and updated processes, to prevent misuse of data that may not be directly related to tasked selectors.
People: Shea, Teresa H. -
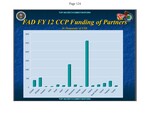
FAD FY 12 CCP Funding of Partners [pdf]
A Foreign Affairs Directorate slide showing Combined Cryptologic Program funding of foreign partners in fiscal year 2012, in thousands of dollars, across fifteen countries including Canada, Israel, Japan, Jordan, Pakistan, Taiwan and Thailand.
-
FAIRVIEW dataflow charts April 2012 [pdf]
This document outlines data flow diagrams that show how various types of sensitive communication, including voice, fax, and modem traffic, are handled through systems operated by the NSA and its partners. These partners include corporations, telecommunications companies, ISPs, and other entities involved in processing and managing the data through secure and classified channels. The document covers processing flows for various data types, metadata, and communications systems under NSA's control, detailing how data is routed, stored, and analyzed across different platforms and sites.
Programs: FAIRVIEW · SAGUARO · TURNSTILE · MESA · TITANPOINT · RIMROCK · MAILORDER · PINECONE · BLARNEY · STONEGATE · TINSEL · CONVEYANCE · FISHWAY · NUCLEON · PINWALE · SCISSORS · COURIERSKILL · DRIFTWOOD · ASDF · FALLOUT · MARINA · LOPERS · WEALTHYCLUSTER · PUPR · CLEARSIGHT · MIDFIELD · CADENCE · BUGCATCHER · WAYLAND · DESOTO · GATEKEEP · HIGHDECIBEL · XKEYSCORE · YANKEE · TOPROCK · FASCIA · DISHFIRE · SEAGULL · BIGDIPPER · CORPORATE · LILDIPPER · HAVASU · WEALTHYCLUSTER2 · RAGTIME · TUMULT · TATTOO · DARKTHUNDER · ICYTWINS · TML-STATUS · WATERFRONT · VULCANDEATHGRIP · STEELFLAUTA · UNITY · KEYCARD · UTT · BTUBE · ISLANDTRANSPORT · SSO · MAINWAY · SSDM · TUBE · TITANPOINTE · TURMOIL · VPCS“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “Titanpointe: The NSA’s Spy Hub in New York, Hidden in Plain Sight” - The Intercept ↗ (2016-11-16) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan -
FAIRVIEW site book [pdf]
The Fairview TDY Handbook provides essential guidelines for NSA employees travelling in support of the FAIRVIEW Program, detailing required training, security protocols, and travel procedures for both CONUS and OCONUS missions. It covers travel authorization, necessary courses, cover travel considerations, vehicle usage, and operational security (OPSEC) instructions for visits to partner and collection sites. The handbook emphasizes security, confidentiality, and appropriate conduct while interacting with partner organizations and traveling to sensitive locations.
Programs: FAIRVIEW · EAGLE · EDEN · TITANPOINT · PINECONE · TITANPOINTE · BLARNEY · STORMBREW · OAKSTAR · SILVER COLLAM · SSO · LITHIUM -
FASCIA: The NSA's huge trove of location records [pdf]
FASCIA is the National Security Agency's enormous database containing trillions of metadata records, many with device locations, that are collected from a variety of sources. This document shows the volume and types of device-location data collected by the agency.
“NSA tracking cellphone locations worldwide, Snowden documents show” - The Washington Post ↗ (2013-12-04) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Gellman, Barton · Soltani, Ashkan · Greenwald, Glenn