Classification: COMINT 287 documents
Search documents matching “COMINT” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (13 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
3G: impact and update - SDF Nov 09 [pdf]
This 2009 top-secret presentation from Australia’s Defence Signals Directorate (DSD) detailing 3G mobile network rollouts in Southeast Asia and identifying Indonesian President Susilo Bambang Yudhoyono, his wife, and senior officials as surveillance targets. It includes handset information, call data records, intercepted call attempts, and outlines plans for continued interception of Indonesian leadership communications.
-
A potential technique to deanonymise users of the TOR network [pdf]
A TOP SECRET GCHQ research presentation describing a traffic correlation attack against Tor — using cumulative packet counts observed simultaneously at a controlled exit node and at SIGINT collection points near a target's guard node to deanonymise Tor users without breaking the encryption — with GTE and JTRIG having adapted owned exit nodes to collect the required data for live deployment.
-
A potential technique to deanonymise users of the TOR network [pdf]
The GCHQ technical report documenting the entry-exit traffic correlation attack against Tor — providing the complete mathematical specification, test methodology, experimental results and software reference implementation, with distribution to NSA R1, NSA R4, NSA CES, CSE, DSD, SEQUOIA, ICTR, JTRIG, TEA, GTE and multiple OPC divisions.
-
Advanced HTTP Activity Analysis [pdf]
This NSA training document from 2009 teaches intelligence analysts how to analyze HTTP internet traffic and exploit it using the XKEYSCORE surveillance system to monitor and identify internet users globally.
“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
Afghanistan Coalition Dissemination Brief to Senior Leadership Forum [pdf]
This document ooutlines the structure, goals, and challenges of multinational signals intelligence (SIGINT) collaboration in Afghanistan as of 2009. It reveals how the U.S. and its intelligence-sharing allies (notably the 5 Eyes, 9 Eyes, and 14 Eyes) coordinated SIGINT collection, decryption, analysis, and dissemination across NATO and coalition forces.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA presentation examines metadata attribution challenges arising when active TAO implants exfiltrate traffic through passive TURMOIL collection infrastructure, creating conflicts where intercepted data carries dual classification markings, case notations, and legal authorities from both collection systems. The briefing highlights how existing databases and analytic tools were not designed to handle traffic with two simultaneous sets of metadata parameters, requiring enterprise-wide solutions to consistently attribute and track actively-shaped intelligence collection.
Programs: BRAVENICKEL · HAMMERMILL · APEX · MARINA · TURMOIL · PRESSUREWAVE · METROTUBE · TOYGRIPPE · HAMMERSTEIN · HAMMERSTONE · METAWAVE · TURBULENCE · SSO -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA briefing addresses the technical and administrative friction caused by "shaping" operations. Shaping occurs when an active malware implant, typically situated on network infrastructure like a router, copies specific data streams and redirects them past a passive surveillance sensor such as TURMOIL. While this ensures the capture of data that might otherwise be missed, it creates a "double metadata" conflict where a single piece of intelligence carries two competing sets of identifiers: one from the active Tailored Access Operations (TAO) implant and another from the passive collection site. The document tasks analysts with finding a way to reconcile these source notations to ensure the data remains searchable and legally compliant within legacy databases.
Programs: BRAVENICKEL · HAMMERMILL · APEX · TURMOIL · HAMMERSTONE · PRESSUREWAVE · METROTUBE · TOYGRIPPE · TURBULENCE · METAWAVE · MARINA · SSO · CONVEYANCE · NUCLEON · FASCIA · HAMMERCHANT -
Analyzing Mobile/Cellular DNI in XKEYSCORE, May 2009 [pdf]
The XKEYSCORE document explains how the agency analyzes mobile/cellular device internet usage by collecting and processing both converged DNI/DNR data within cellular networks and traditional internet traffic, using various tools and indicators to identify mobile users even when their device type isn't immediately evident. The document demonstrates how the system can track mobile internet activity across applications like Yahoo Mail and identifies devices through various technical "hints" including MSISDN codes, browser fingerprints, and user agent strings.
-
"Anarchist" Image Index [pdf]
Images collected through ANARCHIST, the GCHQ covername for a joint GCHQ/NSA SIGINT collection site on Mt. Troodos, Cyprus, drawn from imagery and pages in GCHQ's internal GCWiki.
Programs: ANARCHIST -
Approved SIGINT Partners [pdf]
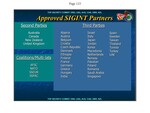
A Foreign Affairs Directorate slide listing NSA's approved SIGINT partners: the four Second Parties, 33 Third Parties from Algeria to the United Arab Emirates, and the coalitions AFSC, NATO, SSEUR and SSPAC. This is document is from Fiscal Year 2013 "Foreign Partner Review."
-
AURORAGOLD – Project Overview [pdf]
A technical briefing document outlining an NSA SIGINT initiative designed to map, monitor, and forecast the evolution of global mobile networks. It details the project's infrastructure, which aggregates both unclassified commercial data and classified intelligence intercepted from international roaming agreements to identify technical trends and exploitation opportunities.
-
AZTECTOMB32 DMW Install and ESH Package [pdf]
This document is a top-secret NSA internal project log detailing restrictions on installing new implants on machines running Kaspersky 2010+ due to the software’s cloud functionality, which prevents safe deployment of NSA malware. It records the suspension and eventual closure of a project (AZTECTOMB32/DEMENTIAWHEEL) that would have targeted such systems.
-
-
BLARNEY report April 2013 [pdf]
This NSA document describes the deployment of surveillance systems (RINGBILL, TURTLEPOWER, SKIDROWE) at "TITAN POINTE" to process bulk communications data including VoIP and video teleconferencing traffic. The systems are designed to intercept, filter, and analyze high-volume network traffic using legacy architecture initially, with plans to transfer to newer processing solutions for long-term mass surveillance capabilities.
Programs: BLARNEY · RINGBILL · WEALTHYCLUSTER2 · XKEYSCORE · TRIREME · SKIDROWE · PINWALE · TITANPOINTE · VISIONQUEST · TURTLEPOWER · SKINNY -
BLARNEY site book [pdf]
2011 BLARNEY Program TDY Handbook outlining procedures for NSA personnel traveling in support of the program, including cover protocols, required training, site visit guidelines (e.g., FBI HQ, Quantico, Titan Pointe), and rules for transporting classified materials. It emphasizes the use of cover stories, special vehicles, and strict coordination with program directors to maintain operational security.
-
Blazing Saddles [pdf]
This document describes BLAZING SADDLES, a GCHQ program designed to massively scale the storage and analysis of bulk internet surveillance data through multiple specialized databases that track website visits, online identities, communications patterns, and geolocation queries across the global internet population.
Programs: BLAZINGSADDLES · BLACKHOLE · SOCIALANTHROPOID · AUTOASSOC · HRMAP · INFINITEMONKEYS · KARMAPOLICE · MARBLEDGECKO · MUTANTBROTH · MEMORYHOLE · SAMUELPEPYS · SOCIALANIMAL · HAUSTORIUM · GOLDENAXE · NGE -
Broadcast/Internet Radio Exploitation and Analysis, 6th November 2009, GCHQ [pdf]
This GCHQ report analyzes 6.68 million internet radio listening events collected over three months in 2009, detailing global broadcasting patterns, user behaviors, and specifically examining Islamic radio stations and Pakistan-UK connections for potential radicalization intelligence, while recommending integration with bulk surveillance databases like KARMA POLICE for enhanced user profiling.
-
BULLRUN CoI - Briefing Sheet [pdf]
A GCHQ briefing sheet introducing the BULLRUN Community of Interest — the access control framework protecting Five Eyes capabilities to defeat encryption across TLS/SSL, HTTPS, SSH, VPNs, IPSec, encrypted chat and encrypted VoIP — covering the classification structure, handling procedures and protective marking guidance for intelligence derived from cryptanalytic exploitation.
“N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Perlroth, Nicole · Larson, Jeff · Shane, Scott · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
BYZANTINE HADES: An Evolution of Collection [pdf]
A classified NSA SIGINT briefing from 2010 describes “BYZANTINE HADES,” a collection of Chinese computer network exploitation activities, with a focus on the BYZANTINE CANDOR actor set and U.S. efforts to analyze, attribute, and counter those intrusions. The document details targeting patterns, technical tradecraft, and a TAO-led counterintelligence operation that successfully penetrated the attackers’ infrastructure and personal systems.
Programs: BYZANTINEHADES · BYZANTINECANDOR · BYZANTINERAPTOR · BYZANTINEANCHOR · BISHOPKNIGHT · BYZANTINEVIKING · MAVERICKCHURCH · BISHOP · BYZANTINETRACE · DIESELRATTLE · BYZANTINEFOOTHOLD · BYZANTINEPRAIRIE · SEEDSPHERE · CARBONPEPTIDE · TITANRAIN · PINWALE · XKEYSCORE · CROSSBONES · TUNINGFORK · ARROWECLIPSE · CUTEBOY · POPROCKS · BYZANTINE -
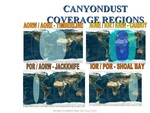
Canyondust coverage regions [pdf]
This document describes NSA's capabilities for exploiting commercial satellite communications (VSAT), including systems from Hughes, ViaSat, iDirect, and others. It details programs such as FALLOWHAUNT and CORRALCLOUD for targeting and analyzing satellite communications technologies, including TDMA and PCMA systems.
Programs: CANYONDUST · TIMBERLINE · CARBOY · JACKKNIFE · SHOAL BAY · FALLOWHAUNT · CORRALCLOUD · DOUBLETALK