Country: Turkmenistan 9 documents
Search documents matching “Turkmenistan” →Countries mentioned in each document. A country may be mentioned directly (e.g., France) or inferred from a related reference, such as a city (Paris -> France) or a domain name (.fr -> France).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
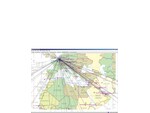
Belgacom connections [pdf]
A "Belgacom connections" map lays out the carrier’s sprawling roaming and backbone interconnects, precisely the arteries GCHQ wanted to get access into. Under Operation Socialist GCHQ successfully gained access to Belgacom’s infrastructure, including internal employee computers and encrypted and unencrypted streams of private communications handled by the company.
Programs: CARBONROD“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.
-
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
Israel-US 1999 Agreement [pdf]
This July 1999 top secret agreement between the U.S. Defense Intelligence Agency and Israel's Directorate of Military Intelligence establishes comprehensive intelligence-sharing arrangements covering Middle Eastern threats, terrorism, weapons of mass destruction, and foreign materiel exploitation, superseding previous agreements dating back to 1968 and including specific provisions for conferences, written requests, face-to-face analyst meetings, and security protocols.
-
-
List of foreign governments and organizations authorized for surveillance [pdf]
This exhibit lists the 193 foreign governments as well as foreign factions, political organizations and other entities that were part of a 2010 certification approved by the Foreign Intelligence Surveillance Court. These are the entities about which the NSA may conduct surveillance, for the purpose of gathering foreign intelligence. Each year a new certification must be approved by the court to permit such surveillance under Section 702 of the FISA Amendments Act.
-
NSA Video Games Paper [pdf]
The NSA paper entitled “Games: A Look at Emerging Trends, Uses, Threats, and Opportunities in Influence Activities” stresses the risk of leaving gaming communities under-monitored and how the NSA and GCHQ are conducting surveillance in various online games, collecting gamers' chat data, and deploying agents into World of Warcraft and Second Life.
People: Garite, Matt · Prasad, Kaira · Castronova, Edward · DeBenedictis, Steven · Robbins, Brian · Dunin, Elonka · Estanislao, Jon · James, Daniel · Valadares, Jeferson · Kushner, David · Ondrejka, Corey · Bonk, Curtis J. · Dennen, Vanessa P. · Lindstrom, Martin · Yee, Nick · Jayaganthan, Rengaswamy · Tawil-Souri, Helga · Soussi, Alasdair · Baertlein, Lisa · Brachman, Jarret M. · Rolston, David · Dille, Flint · Bilson, David S. · Bray, Hiawatha · Morgan, Dan · Henry, Dean · Halper, Keith · Pardew, Leslie A. · Betrus, Anthony D. · Steinkuehler, Constance A. · Gupta, Shankar · Joshi, Mahesh P. · Fong, Gwenda · Andersen, John · Reid, David · Kramer, Stephen E. · Brown, Seely · Thomas, Douglas · Phillips, Andrea · Thompson, Brooke · Alexander, Bryan · Dena, Christy · Barlow, Nova · Weimann, Gabriel · Mace, Michael · Knight, Will · Gibson, Erin · Langley, Hugh · Huang, Shih-Lian · Ruff, Chris · Gibson, Ben · Cialdini, Robert B. · Johnson, Steven · Tulloch, Paul · McLundie, Martin · Galles, Kara · Berkowitz, Jeff · May, William · Leonard, David J. · Williams, Dmitri“World of Spycraft: NSA and CIA Spied in Online Games” - ProPublica ↗ (2013-12-09) · “Spies Infiltrate a Fantasy Realm of Online Games” - The New York Times ↗ (2013-12-09) · “Xbox Live among game services targeted by US and UK spy agencies” - The Guardian ↗ (2013-12-09) · Elliott, Justin · Mazzetti, Mark · Ball, James -
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
SSO Weekly Brief 25 April 2013: Excerpt [pdf]
This document highlights a PRISM FAA report from 10 April 2013, detailing U.S.-based Uzbek refugee Fazliddin Kurbanov’s communications with Adnan, an official from the Pakistan-based Islamic Movement of Uzbekistan (IMU). Kurbanov expressed his continued intention to attack the U.S., involving explosives and potentially raising money for the IMU, despite believing he was under surveillance by the FBI.