Tag: metadata collection 47 documents
Search documents matching “metadata collection” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
NSA BOUNDLESSINFORMANT Chart on Denmark [pdf]
The Denmark BOUNDLESSINFORMANT chart covering Dec 10, 2012 to Jan 8, 2013 shows that Danish intelligence collected and shared about 22.9 million cellphone metadata records with the NSA through DRTBOX systems. These records were gathered in Afghanistan as part of the Afghanistan SIGINT Coalition, not mass surveillance inside Denmark.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
NSA BOUNDLESSINFORMANT Chart on France [pdf]
The France BOUNDLESSINFORMANT chart covering Dec 10, 2012 to Jan 8, 2013 shows that French intelligence collected and shared about 70.3 million cellphone metadata records with the NSA, primarily through DRTBOX systems. These records were gathered in Afghanistan as part of the Afghanistan SIGINT Coalition, not mass surveillance inside France.
“Comment la NSA espionne la France” - Le Monde ↗ (2013-10-21) · Follorou, Jacques · Greenwald, Glenn -
NSA BOUNDLESSINFORMANT Chart on Germany [pdf]
The Germany BOUNDLESSINFORMANT chart covering Dec 10, 2012 to Jan 8, 2013 shows that German intelligence collected and shared about 553 million cellphone metadata and internet records with the NSA, primarily through XKEYSCORE, LOPERS, and JUGGERNAUT systems.
-
NSA BOUNDLESSINFORMANT Chart on Netherlands [pdf]
The Netherlands BOUNDLESSINFORMANT chart covering Dec 10, 2012 to Jan 8, 2013 shows that Dutch intelligence collected and shared about 1.8 million cellphone metadata records with the NSA, primarily through CERF CALL systems. According to the Dutch government, the records were collected by the Dutch National SIGINT Organisation (NSO) for counterterrorism and military operations abroad, with Dutch phone numbers filtered out before sharing, and were not interception of calls in the Netherlands.
-
NSA BOUNDLESSINFORMANT Chart on Norway [pdf]
The Norway BOUNDLESSINFORMANT chart covering Dec 10, 2012 to Jan 8, 2013 shows that Norwegian intelligence collected and shared about 33.2 million cellphone metadata records with the NSA, primarily through DRTBOX systems. These records were gathered in Afghanistan as part of the Afghanistan SIGINT Coalition, not mass surveillance inside Norway.
-
NSA BOUNDLESSINFORMANT Chart on Spain [pdf]
The Spain BOUNDLESSINFORMANT chart covering Dec 10, 2012 to Jan 8, 2013 shows that Spanish intelligence collected and shared about 60 million cellphone metadata records with the NSA. These records were gathered in Afghanistan as part of the Afghanistan SIGINT Coalition, not mass surveillance inside Spain.
Programs: BOUNDLESSINFORMANT -
NSA BOUNDLESSINFORMANT Chart on Sweden [pdf]
The Sweden BOUNDLESSINFORMANT chart covering Dec 10, 2012 to Jan 8, 2013 shows that Swedish intelligence collected and shared about 33.7 million cellphone metadata records with the NSA. These records were gathered in Afghanistan as part of the Afghanistan SIGINT Coalition, not mass surveillance inside Sweden.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
NSA inspector general report on email and internet data collection under Stellar Wind, 24 March 2009 [Working Draft] [pdf]
This 2009 NSA Inspector General draft report details the origins and legal framework of the President’s Surveillance Program (PSP), launched after 9/11 to bypass FISA limits and authorize bulk interception of internet and telephony content and metadata, including communications with one end inside the U.S. It reveals how NSA, with White House backing, expanded surveillance authority to cover “collection gaps” that existing law didn’t allow, effectively legalizing large-scale warrantless spying under a secret presidential directive.
People: Bush, George W. · Hayden, Michael · Tenet, George · Gonzales, Alberto R. · Addington, David S. · Graham, Robert · Deitz, Robert L. · Shelby, Richard · Pelosi, Nancy · Cheney, Dick · Libby, I. Lewis · Lamberth, Royce · Inouye, Daniel · Levin, Daniel · Stevens, Theodore · Kollar-Kotelly, Colleen · Rockefeller, Jay · Alexander, Keith B. · Potenza, Vito -
NSA June 2012 SSO Weekly Brief Excerpt [pdf]
This NSA Special Source Operations (SSO) briefing from June 2012 describes SPINNERET, a surveillance program that became the second-largest source of phone calling records and "tips" feeding into SHELLTRUMPET, a system that obscures the origin of collected metadata before forwarding it to NSA's Real-Time Regional Gateway (RT-RG) in Texas. The document indicates SHELLTRUMPET "obfuscates the source designators" and filters metadata to only include call events within NSA-Texas's area of responsibility.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
NSA/GCHQ/CSEC Network Tradecraft Advancement Team [pdf]
The "NSA/GCHQ/CSEC Network Tradecraft Advancement Team (NTAT) 2010" document describes a collaborative mission between the US, UK, and Canada to synchronize and advance SIGINT techniques. The NTAT focused on "Network Analysis Tradecraft," specifically integrating analysis tools such as IRASCIABLE RABBIT and TOYGRIPPE into CSEC's OLYMPIA and developing standardized "use cases" for tracking mobile networks and virtual private networks (VPNs).
-
NTAC Overview [pdf]
This document outlines the structure, mission, and operations of the U.K.’s National Technical Assistance Centre (NTAC), a GCHQ-controlled unit responsible for enabling and managing lawful interception of communications and decryption of data across national networks. It details NTAC’s integration into GCHQ, its key role in programs like MILKWHITE, its extensive interception capacity, and the technical and resource challenges it faces in adapting to evolving telecommunications technologies.
Marking: SECRET -
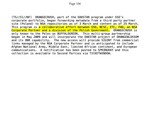
ORANGECRUSH, part of the OAKSTAR program [pdf]
An SSO item reporting that ORANGECRUSH — the OAKSTAR access at a third-party partner site in Poland, known to the Poles only as BUFFALOGREEN — began forwarding metadata to NSA on 3 March and content on 25 March, with collection shared to Second Parties through TICKETWINDOW.
-
OTR encrypted messages can't be decrypted by the NSA [pdf]
Three intercepted chat sessions from 16 March 2012 collected under PRISM, showing a target switching mid-conversation from unencrypted to OTR-encrypted messaging — with NSA able to collect the session metadata and unencrypted portions but unable to decrypt the OTR messages, each annotated "No decrypt available for this OTR encrypted message."
Programs: PRISM -
RT10 Overview [pdf]
This RT10 overview document is a high-level briefing on the implementation of a real-time SIGINT architecture designed to modernize intelligence operations in the Iraq theater, specifically Baghdad. The project aims to replace legacy, "manual-intensive" processes with a "SIGINT Brain"—a distributed database and automated analytic framework capable of processing over 50 million GSM metadata events per day.
Programs: RT10 · OBELISK · WISPYKNIT · VICTORYUNIFORM · JUGGERNAUT · COBRAFOCUS · MATTERHORN · EXPIATION · VoiceRT · GREENDRAGON · TAREX · KEYCARD -
Shaping Diagram [pdf]
This hand-drawn diagram detail an NSA methodology for intercepting and redirecting internet traffic. The approach involves manipulating data flows through a controlled fiber cable, leveraging Computer Network Exploitation (CNE) to capture and replicate target communications for SIGINT processing, all framed in a tongue-in-cheek, yet highly classified, presentation style.
-
SIERRA LEONE - BELGIUM [pdf]
May 2009 GCHQ report documents the interception of two satellite carriers linking Sierra Leone and Belgium (via INTELSAT 9F3), surveyed using the TERRAIN collection suite, which identified numerous email selectors of interest carried over the link. Among the hits was the email address of “Oles” — Octave Klaba, founder and CEO of OVH, Europe’s largest internet hosting company — flagged as a target alongside diplomatic and political addresses, though his presence on the list reflects metadata collection rather than proof his message contents were intercepted.
Programs: TERRAINPeople: Klaba, Octave -
SKIDROWE [pdf]
This document reveals the extensive surveillance capabilities of the NSA's SKIDROWE program at TITANPOINTE, specifically designed to intercept and analyze satellite communications and internet data. It highlights how intercepted data is processed and filtered through advanced systems like XKEYSCORE, which enables real-time intelligence gathering by sifting through massive amounts of digital content, including emails, calls, and internet activity.
Programs: SKIDROWE · WEALTHYCLUSTER2 · WEALTHYCLUSTER · TURNWEALTHY · VPCS · XKEYSCORE · GENESIS · CONTROLAND · ATM · FITBOY · DARKTHUNDER · FIP · METTLESOME · SKYFRAME · PVOICE · XXPY0012 · AGITATOR · STARPROC · SPELLBINDER · BLACKPEARL · BLACKALCHEMY · BLACKGOLD · BLACKFIRE · MONKEYMIND · BCD · EVVIPER · QUANTUM · MISTYPEAK · VALIANTSURF · GALLANTWAVE · SWINE · BLUESNORT · TOSSSWUNG · GNOMEVISION · GNOMEGOGGLES · HIDDENSALAMANDER · TURMOIL · PSC -
Special Source Collection - March 2013 [pdf]
A March 2013 NSA Special Source Operations briefing for the NSA Threat Operations Center outlining SSO's portfolio of surveillance programs, their legal authorities, and operational constraints — revealing that SSO accounts for approximately 60% of NSA content collection and 75% of metadata collection, and mapping all major collection programs across three access categories: foreign partner, corporate, and unilateral.
-
Special Source Operations - Corporate Partner Access [pdf]
A classified NSA Special Source Operations briefing detailing the four major corporate partner surveillance programs — BLARNEY, FAIRVIEW, STORMBREW, and OAKSTAR — their legal authorities, collection access points, target lists, and funding profiles totaling nearly $480 million in FY2010, revealing the infrastructure through which the NSA taps U.S. telecommunications companies to intercept international fiber optic communications on American soil.
Programs: BLARNEY · FAIRVIEW · STORMBREW · OAKSTAR · LITHIUM · ARTIFICE · ROCKSALT · SERENADE · PINECONE · BRECKENRIDGE · TAHOE · SUNVALLEY · WHISTLER · KILLINGTON · COPPERMOUNTAIN · MAVERICK · CONUS · TURMOIL · UTT · STEELKNIGHT · SSO“Snowden document reveals key role of companies in NSA data collection” - The Guardian ↗ (2013-11-01) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “Titanpointe: The NSA’s Spy Hub in New York, Hidden in Plain Sight” - The Intercept ↗ (2016-11-16) · MacAskill, Ewen · Rushe, Dominic · Dance, Gabriel · Greenwald, Glenn · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan -
Special Source Operations - The Cryptologic Provider of Intelligence from Global High-Capacity Telecommunications Systems [pdf]
The document outlines NSA special source operations for accessing global telecommunications data, detailing corporate and foreign cable interception programs. It highlights the MUSCULAR program (DS-200B), a joint NSA–GCHQ operation in the UK that taps into high-capacity fiber-optic links to collect and process large volumes of data from private networks.