Tag: OPSEC 48 documents
Search documents matching “OPSEC” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Final Day: SID OPSEC Name-the-Mascot Contest SIDtoday [pdf]
It's the last day to submit names for the SID OPSEC dragon mascot naming contest.
The Intercept ↗ (2017-04-24) -
IDENTITY THEFT - OPSEC for SID Personnel SIDtoday [pdf]
Announcement for an unclassified seminar that the OPSEC program is hosting about identity theft: how identities are stolen and used, what to do if your identity is stolen, and how to prevent it.
The Intercept ↗ (2017-04-24) -
Operations Security (OPSEC) in SID SIDtoday [pdf]
Brief introduction to operational security and the SID OPSEC managers.
The Intercept ↗ (2016-08-10) -
OPSEC - Don't Forget About It! SIDtoday [pdf]
A fictional cartoon, Prudence the OPSEC Dragon, helps the Signals Intelligence Directorate think about what information needs protecting and how to protect it.
The Intercept ↗ (2018-03-01) -
OPSEC 1201 - OPSEC for SID Personnel SIDtoday [pdf]
Announcing a new online OPSEC course designed specifically for SID personnel, OPSEC 1201.
Marking: UNCLASSIFIEDPrograms: VUPORTThe Intercept ↗ (2016-12-07) -
OPSEC Bulletin: Converting Sanitized Text from Word to PDF? -- Caution! SIDtoday [pdf]
A new report from the Information Assurance Directorate highlights a common operational security error: converting “sanitized” Microsoft Word documents to PDF without purging metadata or properly redacting images, text, or diagrams.
Programs: E-SpaceThe Intercept ↗ (2018-08-15) -
OPSEC in SID - Some Answers SIDtoday [pdf]
Helpful hints for SID personnel on applying operational security to their day-to-day activities.
Marking: CONFIDENTIALPrograms: VUPORTThe Intercept ↗ (2016-12-07) -
OPSEC: Why Should You Care? SIDtoday [pdf]
Presents a hypothetical scenario in which 15 coworkers meet at a restaurant to bid farewell to an employee. If an adversary happened to be at a nearby table listening in, what would they learn?
The Intercept ↗ (2016-12-07) -
SID OPSEC: Identity Theft and Name-the-Mascot SIDtoday [pdf]
This article is written in the voice of an anthropomorphic SID OPSEC purple dragon as "dictated to" SID OPSEC program managers. The dragon, which doesn't have a name yet, discusses identity theft, phishing emails, and other OPSEC topics, and ends with the announcement of a naming contest.
The Intercept ↗ (2017-04-24) -
Upcoming OPSEC Training Opportunities SIDtoday [pdf]
Secretary of Defense Paul Wolfowitz wants everyone in the DOD to apply the process of OPSEC to their daily work. The SID OPSEC Program Manager lists several upcoming trainings for personnel to attend.
Programs: VUPORTPeople: Wolfowitz, Paul D.The Intercept ↗ (2016-12-07) -
ZabaSearch.com: OPSEC Worry? SIDtoday [pdf]
The Internet Program Manager explains to anxious NSA staffers that public records information revealing addresses, phone numbers, and other personal information is now widely available on the web. "OPSEC/COMSEC concern? Sure. Is there anything you can do to mitigate it? No."
The Intercept ↗ (2017-09-13) -
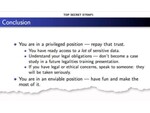
Access to the future [pdf]
The conclusion slide excerpt of a GCHQ presentation on TEMPORA, telling analysts they are in a "privileged" and "enviable" position with ready access to a great deal of sensitive data, and to "have fun and make the most of it".
Programs: TEMPORA -
BLARNEY site book [pdf]
2011 BLARNEY Program TDY Handbook outlining procedures for NSA personnel traveling in support of the program, including cover protocols, required training, site visit guidelines (e.g., FBI HQ, Quantico, Titan Pointe), and rules for transporting classified materials. It emphasizes the use of cover stories, special vehicles, and strict coordination with program directors to maintain operational security.
-
BYZANTINE HADES: An Evolution of Collection [pdf]
A classified NSA SIGINT briefing from 2010 describes “BYZANTINE HADES,” a collection of Chinese computer network exploitation activities, with a focus on the BYZANTINE CANDOR actor set and U.S. efforts to analyze, attribute, and counter those intrusions. The document details targeting patterns, technical tradecraft, and a TAO-led counterintelligence operation that successfully penetrated the attackers’ infrastructure and personal systems.
Programs: BYZANTINEHADES · BYZANTINECANDOR · BYZANTINERAPTOR · BYZANTINEANCHOR · BISHOPKNIGHT · BYZANTINEVIKING · MAVERICKCHURCH · BISHOP · BYZANTINETRACE · DIESELRATTLE · BYZANTINEFOOTHOLD · BYZANTINEPRAIRIE · SEEDSPHERE · CARBONPEPTIDE · TITANRAIN · PINWALE · XKEYSCORE · CROSSBONES · TUNINGFORK · ARROWECLIPSE · CUTEBOY · POPROCKS · BYZANTINE -
CLASSIFICATION GUIDE FOR ECI PAWLEYS (PAW) [pdf]
This 2006 NSA classification guide outlines the protocols for ECI PAWLEYS (PAW). PAWLEYS is an Exceptionally Compartmented Information (ECI) category designed to protect clandestine operations—both physical (HUMINT) and digital (CNE)—specifically aimed at acquiring foreign cryptographic information and material. The document confirms that the NSA actively seeks to circumvent encryption through clandestine HUMINT and computer network access aimed at cryptographic information and material, rather than relying solely on traditional codebreaking.
Programs: PAWLEYS -
CSEC Cyber Threat Capabilities [pdf]
This document details CSEC’s full-spectrum cyber operations architecture, integrating SIGINT and IT Security to conduct both defensive and offensive activities under the guise of “information superiority.” While early sections emphasize detection, anomaly analysis, and collaboration with Five Eyes partners, later portions reveal active measures including network infiltration (implant deployment), command-and-control tracking, traffic manipulation and redirection, DNS interference, and potential disruption or deception operations—illustrating CSEC’s capacity not only to defend Canadian networks but also to surveil, exploit, and influence foreign and domestic digital infrastructure.
Programs: EONBLUE · CYBERDMZ · SEEDSPHERE · PHOTONICPRISM · SPECIALSOURCE · SUPERDRAKE · DARKSPACE · QUANTUM · MANDATE · STREAMING SENTRY · SSO · TKB · COVENANT -
CSEC SIGINT Cyber Discovery: Summary of the current effort [pdf]
This document provides a overview of the Communications Security Establishment Canada (CSEC) cyber operations, detailing its SIGINT, CNE (Computer Network Exploitation), and cyber counterintelligence programs, including tools like WARRIORPRIDE, REPLICANTFARM, and EONBLUE for threat detection, anomaly discovery, and metadata production. It outlines operational procedures, analytic methodologies, and collaborative frameworks with domestic and Five Eyes partners for sharing intelligence, tipping/cueing, and integrating cyber and traditional counterintelligence efforts.
Programs: REPLICANTFARM · SLIPSTREAM · WARRIORPRIDE · DAREDEVIL · CHORDFLIER · NAMEDROPPER · WORMWOOD · OBELIX · SHEPHERD · CARBON · REGBACKUP · DOGHOUSE · WALKER · ALOOFNESS · BLAZINGANGEL · TINYWEB · QUIVERINGSQUAB · WINDO · DIESELRATTLE · WIDOWKEY · CIVETCAT · WINBEE · SSLINST · PULLEDPORK · EONBLUE · SNIFFLE · QUANTUM · XKEYSCORE · HALTERHITCH · FASTFLUX · DEADSEA · NSPACES · PPF · SSO · TKB“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan -
DEFIANTWARRIOR and the NSA's Use of Bots [pdf]
This TOP SECRET NSA presentation from 2010 documents the DEFIANTWARRIOR effort to identify, seize, and operate botnets using SIGINT-enabled infrastructure, detailing both early failures and subsequent operational successes. The document reveals how bot herding was integrated into broader offensive cyber and intelligence collection strategies across the Five Eyes.
Programs: DEFIANTWARRIOR · OLYMPUS · UNITEDRAKE · TURBULENCE · QUANTUMBOT · TURMOIL · TURBINE · SNIPERS · XKEYSCORE · INCENSER · STELLABLUE · SMOKYSINK · STOVEPIPES · ISLANDTRANSPORT · FESTIVEWRAPPER · FREEFLOW · PRESSUREWAVE · HANGARSURPLUS · SURPLUSHANGER · WAITAUTO · DEEPFRIEDPIG · SEAGULLFARO · COLOSSUS · STORMPIG · YELLPIG · PASTEPIG · SHOUTPIG · ZORPIG · MAILORDER · TREASUREMAP · MARINA · WARNVOLCANO · STRAITBIZARRE · BOTINSTANCES · PUZZLECUBE · SEEKER · SURPLUSHANGAR -
Expeditionary Access Operations: NSA’s Close Access Network Exploitation Program [pdf]
The document describes NSA/TAO’s Expeditionary Access Operations (EAO, S3283), a deployable arm that conducts human-enabled Close Access Network Exploitation (CNE) worldwide—using techniques from physical implants and gifted/compromised laptops to wireless injection tools (e.g., BLINDDATE, NITESTAND) and Wi-Fi geolocation—to support tactical customers like SOCOM, DIA, and task forces in Afghanistan, Iraq, and elsewhere. It details organization, tools, operational theaters (Bagram, Kabul, Kandahar, Stuttgart, Texas, etc.), specific operations (IRONPERSISTENCE, CLIMBINGSHIRT), and plans to formalize partnerships with USCYBERCOM and expand expeditionary CANO capabilities.
Programs: NITESTAND · HAPPY HOUR · BADDECISION · MASTERSHAKE · IRONPERSISTENCE · CLIMBINGSHIRT · BLINDDATE -
FAIRVIEW site book [pdf]
The Fairview TDY Handbook provides essential guidelines for NSA employees travelling in support of the FAIRVIEW Program, detailing required training, security protocols, and travel procedures for both CONUS and OCONUS missions. It covers travel authorization, necessary courses, cover travel considerations, vehicle usage, and operational security (OPSEC) instructions for visits to partner and collection sites. The handbook emphasizes security, confidentiality, and appropriate conduct while interacting with partner organizations and traveling to sensitive locations.
Programs: FAIRVIEW · EAGLE · EDEN · TITANPOINT · PINECONE · TITANPOINTE · BLARNEY · STORMBREW · OAKSTAR · SILVER COLLAM · SSO · LITHIUM