Tag: MITM 19 documents
Search documents matching “MITM” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
BYZANTINE HADES: An Evolution of Collection [pdf]
A classified NSA SIGINT briefing from 2010 describes “BYZANTINE HADES,” a collection of Chinese computer network exploitation activities, with a focus on the BYZANTINE CANDOR actor set and U.S. efforts to analyze, attribute, and counter those intrusions. The document details targeting patterns, technical tradecraft, and a TAO-led counterintelligence operation that successfully penetrated the attackers’ infrastructure and personal systems.
Programs: BYZANTINEHADES · BYZANTINECANDOR · BYZANTINERAPTOR · BYZANTINEANCHOR · BISHOPKNIGHT · BYZANTINEVIKING · MAVERICKCHURCH · BISHOP · BYZANTINETRACE · DIESELRATTLE · BYZANTINEFOOTHOLD · BYZANTINEPRAIRIE · SEEDSPHERE · CARBONPEPTIDE · TITANRAIN · PINWALE · XKEYSCORE · CROSSBONES · TUNINGFORK · ARROWECLIPSE · CUTEBOY · POPROCKS · BYZANTINE -
CNE End Point Requirements [pdf]
This NSA/GCHQ document outlines comprehensive requirements for an endpoint surveillance systems that enables analysts to systematically identify intelligence collection needs and discover appropriate tools for data extraction from compromised computers. The framework covers capabilities for remote data collection, cross-platform intelligence integration, query functions, tasking procedures, and visualization tools across implanted networks.
Programs: STARGATE · LOOKING GLASS · QUANTUM · GOLDENEYE · XKEYSCORE · MARINA · JTRIG · BROADOAK · UTT · GLOBALREACH · GLOBALSURGE · THUGGEE · EREPO · DANCINGBEAR · HAUSTORIUM · SHAREOWN · MUTANTBROTH · MOONRAKER · CARBONROD · RUFFLE · ROCKOPERA · QUINCEY · ECLIPSE · MUGSHOT · HIGHNOTE · UDAQ2 · EKB · TURBINE · ACNO · FLAMECARPET · FUMECUPBOARD · JACKPOT · SLIPSTREAM · B13B · PSC · QUINCY · DAREDEVIL · ROADBED -
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
FOXACID SOP for Operational Management of FOXACID Infrastructure (Draft) [pdf]
This document is an NSA standard operating procedure (SOP) manual detailing how to manage and operate the FOXACID system, which delivers malware to targets through tools like SECONDDATE and BADDECISION. It provides technical instructions for tracking, deploying, and maintaining covert web-based infections used in global cyber operations.
Programs: FOXACID · FOXSEARCH · WAITAUTO · RAISEBED · FORRESTPLACE · FOXHelp · PUZZLECUBE · YACHTSHOP · SECONDDATE · MAGIC SQUIRREL · MAGICBEAN · FINKCOAT · FRUGALSHOT · QUANTUM · FERRETCANNON · BEACHHEAD · OLYMPUS · UNITERAKE · DIRESCALLOP · DEEPFREEZE · FINKDIFFERENT · DISABLEVALOR · VALIDATOR · MISTYVEAL · UNITEDRAKE · PEDDLE CHEAP · PKTWENCH · FORESTPLACE · FOXCONTACT · EASYHOOKUP · DEMENTIAWHEEL · CASTLECREEK · ROCHELP · QUANTUMINSERT · FABULOUSFABLE · WATCHER · FROZENGAZE · FABFAB · DARKFIRE · CRYPTICSENTINEL · DARKHELMET · PSP · WILLOWVIXEN -
GCHQ NAC review – April to June (2011) [pdf]
The GCHQ NAC review (Apr–Jun 2011) details the continuation of Operation Socialist, describing how NAC supported mapping Belgacom’s internal network and guided CNE operators to infiltrate key GRX routers. The aim was to establish positions within the network to enable man-in-the-middle (MitM) operations against roaming mobile handsets.
“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
GCHQ NAC review – January to March (2012) [pdf]
The GCHQ NAC review (Jan–Mar 2012) reports ongoing progress in maintaining CNE access to the Belgacom GRX operator, with the CNE EREPO team issuing new operational requirements to the NAC to further guide and support the hacking operation "OP Socialist".
“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
GCHQ NAC review – July to September (2011) [pdf]
The GCHQ NAC review (Jul–Sep 2011) outlines the continued support by NAC following the successful OP SOCIALIST operation, focusing on mapping Belgacom’s internal network and identifying key internal GRX routers to establish man-in-the-middle (MitM) platforms targeting roaming mobile handsets.
“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
GCHQ NAC review – October to December (2011) [pdf]
The GCHQ NAC review (Oct–Dec 2011) reports that the Belgacom GRX exploitation was highly successful, enabling both CNE and Crypt Ops by uncovering extensive VPN exploitation opportunities through OP SOCIALIST II. The surge operation focused on mapping mobile operators connecting via VPN, analyzing GTP traffic for target selector extraction, and identifying optimal access points—ultimately strengthening sustained network exploitation under the VERACIOUS Project.
“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Introduction to BADDECISION [pdf]
This presentation details the use of the NSA program BADDECISION, which is a computer network exploitation tool (CNE) that uses a frame injection technique to redirect the target client to a FOXACID server.
-
JTRIG tools and techniques [pdf]
This document is an internal GCHQ wiki page from July 2012 detailing the capabilities of GCHQ’s Joint Threat Research Intelligence Group (JTRIG). It serves as an internal "Chinese menu" or catalog of digital tools and techniques used for engineering, intelligence collection, and "effects" (offensive operations).
Programs: JTRIG · CERBERUS · JTRIG RADIANTSPLENDOUR · ALLIUMARCH · ASTRALPROJECTION · TWILIGHTARROW · SPICEISLAND · POISONARROW · FRUITBOWL · NUTALLERGY · BERRYTWISTER · BERRYTWISTER+ · FORESTWARRIOR · JAZZFUSION · BRANDYSNAP · WINDFARM · BOMBAYROLL · COUNTRYFILE · TECHNOVIKING · JAZZFUSION+ · BUMBLEBEEDANCE · AIRBAG · EXPOW · AXLEGREASE · PODRACE · WATCHTOWER · REAPER · DIALd · DIRTYDEVIL · AIRWOLF · ANCESTRY · BEARTRAP · BIRDSONG · BIRDSTRIKE · BUGSY · DANCINGBEAR · DEVILSHANDSHAKE · DRAGON'SSNOUT · EXCALIBUR · FATYAK · FUSEWIRE · GLASSBACK · GODFATHER · GOODFELLA · HACIENDA · GEOFUSION · GLOBALSURGE · ICE · INSPECTOR · LANDINGPARTY · VIKINGPILLAGE · MINIATUREHERO · MOUTH · MUSTANG · PHOTONTORPEDO · RESERVOIR · SEBACIUM · SILVERSPECTER · SODAWATER · SPRINGBISHOP · DIRTYRAT · SYLVESTER · TANNER · TRACERFIRE · VIEWER · TOPHAT · ANGRYPIRATE · ARSONSAM · BUMPERCAR+ · BOMBBAY · BADGER · BURLESQUE · CANNONBALL · CLEANSWEEP · CLUMSYBEEKEEPER · CHINESEFIRECRACKER · BUMPERCAR · CONCRETEDONKEY · DEERSTALKER · GATEWAY · GAMBIT · GESTATOR · GLITTERBALL · IMPERIALBARGE · PITBULL · POISONEDDAGGER · PREDATORSFACE · ROLLINGTHUNDER · SCARLETEMPEROR · SCRAPHEAPCHALLENGE · SERPENTSTONGUE · SILENTMOVIE · SILVERBLADE · SILVERFOX · SILVERLORD · SKYSCRAPER · SLIPSTREAM · STEALTHMOOSE · SUNBLOCK · SWAMPDONKEY · TORNADOALLEY · UNDERPASS · VIPERSTONGUE · WARPATH · HOMEPORTAL · CYBERCOMMANDCONSOLE · NAMEJACKER · BABYLON · CRYOSTAT · ELATE · PRIMATE · JEDI · JILES · MIDDLEMAN · OUTWARD · TANGLEFOOT · SCREAMINGEAGLE · SLAMMER · EARTHLING · NEWPIN · BYSTANDER · CONDUIT · QUINCY · BEARSCRAPE · SFL · SNOOPY · MOBILEHOOVER · NEVIS · CHANGELING · HAVOK · MIRAGE · SHADOWCAT · SPACEROCKET · RANA · LUMP · GURKHASSWORD · CRINKLECUT · SHORTFALL · DEADPOOL · HUSK · LONGSHOT · MOLTEN-MAGMA · NIGHTCRAWLER · PISTRIX · WURLITZER -
Mobile Networks in My NOC World [pdf]
This TOP SECRET STRAP 2 GCHQ document outlines the “MyNOC” operations, a specialized Network Operations Centre used by the UK’s GCHQ to coordinate cyber exploitation of international mobile and telecom infrastructure, with a particular focus on Belgacom’s GRX network under “Operation Socialist” (OP SOCIALIST). It details operational planning, toolsets, personnel roles, network mapping, QUANTUM INSERT targeting, and successful infiltration strategies that enabled CNE (Computer Network Exploitation) access to key Belgacom systems and staff infrastructure.
Programs: HIGHNOTE · COPPERHEAD · NEXUS · CADDIS · BRENT · RUSSETT PHONE · CERBERUS · E-BEAM · PIA · JEDI · WYLEKEY · INTERACTION · EREPO · QUANTUM · WOODCUTTER · MUTANT BROTH · QUANTUM INSERT · NRTA · MERION ZETA · JTRIG · A-SPACE · GEOFUSION“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · “Britain's GCHQ Hacked Belgian Telecoms Firm” - Der Spiegel ↗ (2013-09-20) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
PROFILING SSL AND ATTRIBUTING PRIVATE NETWORKS [pdf]
A TOP SECRET GCHQ presentation introducing two prototype cloud analytics — FLYING PIG, a knowledge base for investigating TLS/SSL traffic at scale across approximately 20 billion events per week, and HUSH PUPPY, a tool for attributing private network traffic to identifiable organisations — with live interface screenshots demonstrating queries against mail.ru infrastructure and operational successes including identification of the Afghan Ministry of Defence network and a foreign Ministry of Foreign Affairs VSAT network.
Programs: FLYINGPIG · HUSHPUPPY · QUICKANT · GEOFUSION · LEGIONJADE · LEGIONRUBY · MAKERSMARK · XKEYSCORE · NOSEYPARKER“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Greenwald, Glenn · Kaz, Roberto · Casado, José -
QUANTUMHAND [pdf]
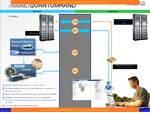
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
QUANTUMINSERT [pdf]
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
SIGINT Development Support II Program Management Review, 24 April 2013 (select slides) [pdf]
These selected slides briefly celebrate two NSA “success stories”: penetrating Pakistan’s Green Line infrastructure with SECONDDATE-enabled implants, and seizing country-wide leverage over Lebanon’s internet backbone through Ogero to siphon off Hezbollah-related data. It shows how U.S. intelligence treated supposedly inaccessible national networks as targets to be shaped, exploited, and folded into its global surveillance machine. See extra slide in "NSA Supply Chain Attack From PMR 4-24-13" https://theintercept.com/document/2019/01/24/nsa-supply-chain-attack-from-pmr-4-24-13/
Programs: MONSTERMIND · CHELSEABLUE · SECONDDATE · QUANTUM · REXKWONDO · STORMBREW · XKEYSCORE · MARINA · HAMMERCORE · HAMREX · CADENCE · HAMMERSTEIN · SSO -
Synergising Network Analysis Tradecraft [pdf]
These Five Eyes slides give an overview of Synergising Network Analysis Tradecraft, a program the NSA and its closest allies developed to plant spyware on smartphones without the knowledge or consent of the user. Specifically, the method seeked to alter the content of data packets moving between targeted smartphones and app servers, causing the spyware to be downloaded along with the app.
Programs: ATLAS · ATHENA · FRETTINGYETI · CRAFTYSHACK · IRRITANTHORN · XKEYSCORE · BLAZINGSADDLES · SPLUNK · SCORPIOFORE · PLINKO · MASTERSHAKE · PEITHO · HYPERION · DANAUS · CONVERGENCE · UCWEB · EONBLUE -
Tailored Access Operations, FOXACID, QUANTUM [pdf]
These NSA presentation slides detail "QUANTUM," a sophisticated system that allows the agency to intercept internet traffic and inject malware onto target computers with up to 80% success rates, far exceeding traditional spam-based methods. The system works by monitoring internet traffic for specific identifiers (like Yahoo or Facebook cookies), then racing to inject malicious code before legitimate web servers can respond, thereby compromising targets' computers without their knowledge and establishing persistent backdoor access.
Programs: FOXACID · QUANTUM · QUANTUMTHEORY · QUANTUMBISCUIT · VALIDATOR · OLYMPUS · UNITEDRAKE · OLYMPUSFIRE · SSO · FORESTPLACE -
Tor - 2006 CES Summer Program [pdf]
The following document is a 2006 research paper produced for the NSA's "Cryptanalysis and Exploitation Services" office. It lays out the technical features of Tor and proposes a number of theoretical and practical attacks, some of which the NSA developed and used in subsequent years. Among other things, the paper describes an NSA-written adaptation of Tor, "indistinguishable from an original Tor client," which enables the NSA to gather intelligence inside the network. It also describes two kinds of "denial of service" attacks against Tor, code-named Coil and Flower, which are used to divert would-be anonymous communications into open channels.
Programs: MJOLNIR -
TURBULENCE - APEX - Active/passive Exfiltration [pdf]
This 2009 NSA presentation details APEX (Active/Passive Exfiltration), a TURBULENCE program component that combines passive collection infrastructure with active TAO implants to exfiltrate VPN and VoIP traffic from deep within target networks back to NSA collection systems. The system uses the FASHIONCLEFT protocol to tunnel captured packets through compromised routers and network devices, enabling decryption of VPN tunnels and collection of voice communications that would otherwise be invisible to passive surveillance.
Programs: TURBULENCE · TURMOIL · HAMMERSTEIN · HAMMERCHANT · FASHIONCLEFT · TUTELAGE · TURBINE · TRAFFICTHIEF · XKEYSCORE · ANALYTICS · PRESSUREWAVE · TOYGRIPPE · POISONNUT · FLAXENPRECEPT · FOGYNULL · FUNNELAPS · SHELLGREY · METROTUBE · VINYLSEAT · OLYMPUS · UNITEDRAKE · FIGBUILD · SURPASSPIN · ROOTKNOT · OPTICPINCH · SEAGULFARO · TREBLECLEF · CONVEY · PINWALE · SWEEPFORWARD · QUANTUM · KEYCARD · ASDF · TUBE · PUZZLECUBE · WEALTHYCLUSTER2 · COALSHOVEL · HAMMERMILL · ISLANDTRANSPORT · FASCIA · TURBINIE · APEX · PPF · AEG · FIP · SSO · PICARESQUE · PSP · IVE · PSC · CHIMNEYPOOL · CORESSC · FLASHHANDLE · IBRIDGE · CORALREEF · VAO · NUCLEON · PIQBLADE“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn