Tag: Five Eyes 94 documents
Search documents matching “Five Eyes” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By document date (10 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
NSA document on targeting Five Eyes countries and territories [pdf]
This document states that the National Security Agency is prohibited from conducting foreign surveillance on the "Five Eyes" countries, which include U.S. allies Australia, Canada, New Zealand and the United Kingdom, or their territories.
-
2003 CSE/NSA SIGINT Bilateral SIDtoday [pdf]
Canada’s Communications Security Establishment hosted an annual SIGINT bilateral, including discussions on support to military operations in Afghanistan, homeland security issues, and counterterrorism in Southeast Asia.
The Intercept ↗ (2016-08-10) -
5-Eyes Global Network Forum SIDtoday [pdf]
Canada's Communications Security Establishment hosted a meeting of representatives from the Five Eyes agencies to discuss how best to coordinate the collection of data from commercial services worldwide.
Programs: STATEROOMThe Intercept ↗ (2017-04-24) -
All EYES on the Counterintelligence Conference SIDtoday [pdf]
The second Five Eyes conference on counterintelligence issues presented a "marked change" from the first conference in attitude and productivity.
People: Coyner, Mary JoThe Intercept ↗ (2017-09-13) -
Almost Like Being There: Collaborating Via InfoWorkSpace SIDtoday [pdf]
More than 3,500 NSA personnel had accounts on InfoWorkSpace, an agency collaboration tool with a "virtual structure of Buildings/Floors/Rooms," chat, voice calls, virtual whiteboards, screen-sharing, and voting tools. The system was deployed to three servers for different classification levels.
The Intercept ↗ (2017-09-13) -
An Intern Tour at the SNAW... With a 3-Month TDY to New Zealand SIDtoday [pdf]
During a three-month tour to New Zealand, an intelligence analysis intern got to apply his social network analysis skills on “one of GCSB’s largest SIGINT targets: the Solomon Islands.”
People: McKloskey, Michael C.The Intercept ↗ (2018-08-15) -
Announcing the 2005 Pacific SIGINT Development Conference SIDtoday [pdf]
The latest iteration of an annual conference on signals intelligence development in the Pacific theater will include briefings to outline achievements, capabilities, and gaps in the region among Five Eyes intelligence agencies.
Marking: CONFIDENTIALPeople: Newton, AndyThe Intercept ↗ (2017-09-13) -
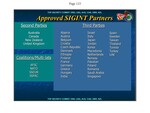
Approved SIGINT Partners [pdf]
A Foreign Affairs Directorate slide listing NSA's approved SIGINT partners: the four Second Parties, 33 Third Parties from Algeria to the United Arab Emirates, and the coalitions AFSC, NATO, SSEUR and SSPAC. This is document is from Fiscal Year 2013 "Foreign Partner Review."
-
Automated NOC detection [pdf]
This slide deck lays out how GCHQ and Canada’s CSEC systematically identified and penetrated Network Operations Centers—most notably Belgacom—by automating NOC discovery and weaponizing that mapping for QUANTUM INSERT attacks. It reads like a blueprint for turning router configs, metadata, and bulk scans into cookie-based targeting against telecom engineers inside core networks.
Programs: SURGE · NOCTURNALSURGE · RT · NACSHACK · CHAINGUARD · TIDALSURGE · GLOBALSURGE · PENTAHO · OLYMPIA · HYPERION · TERMINALSURGE · HACIENDA · QUANTUMINSERT · MUTANTBROTH · OPSOCIALIST · SAMUEL PEPYS · GEOFUSION · FIVEALIVE · NRTA · RADIUS“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Bangladesh: A 'Cocoon of Terror'? SIDtoday [pdf]
Bangladesh appears newly important for counterterrorism efforts after a number of recent terror attacks there, as well as several accused terrorist groups using the country as a “flee haven.” The Five Eyes partners — especially the NSA and New Zealand's Government Communications Security Bureau — are collaborating to increase signals intelligence-gathering in Bangladesh and will hold a conference to discuss their plans.
The Intercept ↗ (2018-03-01) -
Brown Bag Session: Access to 5-EYES Sensitive Source Metadata SIDtoday [pdf]
A brown bag talk will discuss efforts to enhance the 5-Eyes partners' abilities to share sensitive metadata with each other.
People: Deuink, BarbaraThe Intercept ↗ (2019-05-29) -
CNE End Point Requirements [pdf]
This NSA/GCHQ document outlines comprehensive requirements for an endpoint surveillance systems that enables analysts to systematically identify intelligence collection needs and discover appropriate tools for data extraction from compromised computers. The framework covers capabilities for remote data collection, cross-platform intelligence integration, query functions, tasking procedures, and visualization tools across implanted networks.
Programs: STARGATE · LOOKING GLASS · QUANTUM · GOLDENEYE · XKEYSCORE · MARINA · JTRIG · BROADOAK · UTT · GLOBALREACH · GLOBALSURGE · THUGGEE · EREPO · DANCINGBEAR · HAUSTORIUM · SHAREOWN · MUTANTBROTH · MOONRAKER · CARBONROD · RUFFLE · ROCKOPERA · QUINCEY · ECLIPSE · MUGSHOT · HIGHNOTE · UDAQ2 · EKB · TURBINE · ACNO · FLAMECARPET · FUMECUPBOARD · JACKPOT · SLIPSTREAM · B13B · PSC · QUINCY · DAREDEVIL · ROADBED -
Collaboration on Target Templating? It Just Got Easier SIDtoday [pdf]
The article describes the new Five Eyes Target Templating Focal Group, which aims to increase collaboration between agencies when developing targets and standardize methodologies for target templating (which is not defined).
The Intercept ↗ (2018-03-01) -
Coming Soon: A SID Classification Guide SIDtoday [pdf]
The Signals Intelligence Directorate has a new classification guide separate from the NSA/CSS classification guide, which "significantly revamp[s] what is considered COMINT [communications intelligence]." It also changes the default classification to be releasable to Five Eyes allies.
Programs: CLASSIFYThe Intercept ↗ (2017-09-13) -
Communications Security Establishment (CSE) - Our Good Neighbor to the North SIDtoday [pdf]
Communications Security Establishment, the Canadian spy agency, shares a history with NSA dating back to World War II. The article explains what CSE (now CSEC) brings to the SIGINT partnership, including unique access because of Canada’s geography and technical niches.
People: Moffa, ToniThe Intercept ↗ (2016-08-10) -
Conference Eyes Data Flow Among Second Parties SIDtoday [pdf]
The Five Eyes partners held a conference to discuss the standardization of data formats to ease the exchange of voice, text, fax, and digital network intelligence.
Programs: IWSThe Intercept ↗ (2017-04-24) -
Conference Looks at Support to NATO Ops in Afghanistan SIDtoday [pdf]
A newly held Five Eyes conference in Ottawa, Canada, discussed signals intelligence issues related to the International Security Assistance Force’s effort to provide security in Afghanistan.
Programs: CENTER ICEPeople: MazzolinThe Intercept ↗ (2018-08-15) -
CRD Hosts Second Party Customer Relations Conference SIDtoday [pdf]
The Customer Relations Directorate and the Customer Gateway hosted a Second Party Customer Relations Conference, where the Five Eyes partners worked on collaboration, information exchange, networking, and future planning.
Programs: SCORECARDThe Intercept ↗ (2017-04-24) -
CSEC Cyber Threat Capabilities [pdf]
This document details CSEC’s full-spectrum cyber operations architecture, integrating SIGINT and IT Security to conduct both defensive and offensive activities under the guise of “information superiority.” While early sections emphasize detection, anomaly analysis, and collaboration with Five Eyes partners, later portions reveal active measures including network infiltration (implant deployment), command-and-control tracking, traffic manipulation and redirection, DNS interference, and potential disruption or deception operations—illustrating CSEC’s capacity not only to defend Canadian networks but also to surveil, exploit, and influence foreign and domestic digital infrastructure.
Programs: EONBLUE · CYBERDMZ · SEEDSPHERE · PHOTONICPRISM · SPECIALSOURCE · SUPERDRAKE · DARKSPACE · QUANTUM · MANDATE · STREAMING SENTRY · SSO · TKB · COVENANT -
CSEC Cyber Threat Detection [pdf]
This document details the Communications Security Establishment’s (CSEC) cyber threat detection and intelligence infrastructure, including systems like EONBLUE, CROSSBOW, CRUCIBLE, and LODESTONE, which enable passive monitoring, anomaly detection, and botnet identification through metadata and deep packet inspection. It outlines how CSEC integrates SIGINT, cryptanalysis, and network forensics to detect and mitigate cyber intrusions using both SIGINT and domestic sensors, while collaborating with Five Eyes partners to enhance Canada’s cyber defense and situational awareness. The presentation is duplicated from page 7 onwards - one of the duplicated slide has internal CSE comments.
Programs: EONBLUE · SPECIALSOURCE · WARRANTEDACCESS · COVENANT · SEEDSPHERE · DIESELRATTLE · SIENNABLUE · DOWNGRADE · CROSSBOW · CRUCIBLE · LODESTONE