Tag: FISA Amendments Act 10 documents
Search documents matching “FISA Amendments Act” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
FAA702 Glossary - Section 702 of the Fisa Amendments Act (FAA) [pdf]
This document outlines NSA rules under Section 702 of the FISA Amendments Act, which prohibit directly targeting U.S. persons or individuals inside the U.S., but quietly note a 2011 rule change allowing analysts to use U.S. person identifiers to query data already collected under 702—pending internal oversight. This effectively establishes a “backdoor search” capability enabling warrantless searches of Americans’ communications stored in NSA databases. Section 702 also gives the NSA authority to target without warrant the communications of foreign targets.
-
FISA Amendments Act Certifications and Operations [pdf]
This document exposes how, after the FISA Court found flaws in NSA’s upstream surveillance in 2011, the agency pushed through new certifications on schedule the following year and quietly used taxpayer money to cover millions in compliance costs for PRISM companies like Google and Yahoo. Rather than scaling back unconstitutional collection, the NSA treated the ruling as a logistical hurdle to manage with corporate partners, underscoring its deep financial and operational entanglement with major tech firms. Check also the document "FAA Certification Renewals with Caveats"
Programs: PRISM -
BLARNEY Exploits the Social Network via Expanded Facebook Collection [pdf]
An SSO highlight of 14 March 2011 announcing substantially expanded Facebook collection under FISA and FAA authorities — chat, private messages, profile information, subscriber videos and geolocation from IP addresses — built with the FBI over six months, with PRINTAURA writing the new software.
-
Collection Accesses 30 Nov - 06 Dec 2009 [pdf]
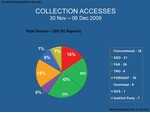
This National Security Agency chart shows the varied sources of 103 “accesses” to communications or computers collected in a single week in 2009 at the N.S.A.’s big station in San Antonio, Texas.
Programs: SSO -
Expanding PRISM Sharing With FBI and CIA [pdf]
An SSO item describing two projects that widened PRISM sharing with the FBI and CIA: PRINTAURA software that compiles the tasked-selector list every two weeks for both agencies, and weekly operational PRISM news and guidance from the mission programme manager.
-
FAA702 comms memo [pdf]
This document details NSA's response to concerns raised by the FISA Court over the collection of non-targeted data in FAA-702 upstream collection. To mitigate the risk of continued acquisition, NSA is implementing temporary measures, including cautionary banners and updated processes, to prevent misuse of data that may not be directly related to tasked selectors.
People: Shea, Teresa H. -
N.S.A. Timeline of Surveillance Law Developments [pdf]
This chart, apparently from an internal N.S.A. presentation, lists milestones in surveillance rules over nearly four decades. The July 2002 “Raw Take” sharing order, whose existence has not previously been disclosed, is just one of three rulings by the Foreign Intelligence Surveillance Court to make the list. The other two were 2004 and 2006 rulings allowing bulk collection of data about emails and phone calls.
-
NSA Cyber Timeline (Some Key SSO Cyber Milestone Dates Since Fall 2005) [pdf]
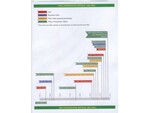
A one-page NSA SSO timeline of cyber-related milestones from fall 2005 to late 2012: CNCI implementation, the Protect America Act and FISA Amendments Act certifications, TURMOIL and XKEYSCORE deployments, and the August 2012 Iranian DDoS attack on Saudi Aramco.
Programs: TURMOIL · SSO · BLUESNORT · DANCINGOASIS · MADCAPOCELOT · TURBULENCE · XKEYSCORE · WEALTHYCLUSTER -
SID concur: SSO's Support to the FBI for Implementation of their Cyber FISA Orders (CATS 2012-704) [pdf]
A 2012 NSA staff processing form (CATS 2012-704) with a four-page SSO memo, concurred by the SIGINT Director on 27 March 2012. SSO would give the FBI technical help implementing FISC cyber orders (docket 11-91, which the FBI calls STYGIAN FLOW), using NSA collection and processing infrastructure (LITHIUM, ARTIFICE, TURMOIL), with the FBI responsible for the costs and for legal compliance.
People: Shea, Teresa H. -
SSO Court Orders [pdf]
A TOP SECRET NOFORN Special Source Operations weekly court orders update showing a FISA court order authorising NSA surveillance of Germany (case 13-319, signed 7 March 2013), alongside expiring orders for Jordan and Morocco — published by Der Spiegel on 29 March 2014 as part of reporting on NSA targeting of Angela Merkel and German companies.