Tag: surveillance oversight 4 documents
Search documents matching “surveillance oversight” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
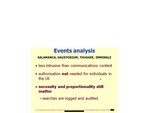
Events Analysis [pdf]
This GCHQ document explains authorization policies for querying metadata databases (SALAMANCA, HAUSTORIUM, THUGGEE, IMMINGLE), stating that metadata is "less intrusive than communications content" and that authorization is "not needed for individuals in the UK," though searches are logged and audited with necessity and proportionality considerations still applying.
-
Legalities - GCHQ Databases eg Pilbeam, Salamanca, UDAQ etc [pdf]
This October 2007 GCHQ document outlines the legal authorization requirements for querying surveillance databases, revealing that GCHQ analysts can search their own databases (like PILBEAM, SALAMANCA, UDAQ) for metadata on anyone regardless of nationality without additional authorization, while NSA databases (like MARINA, MAINWAY, DISHFIRE) prohibit searches for Americans and other Five Eyes citizens but permit searches for UK persons.
-
Minimization Procedures Used By The National Security Agency In Connection With Acquisitions Of Foreign Intelligence, Information Pursuant To Section 702 Of The Foreign Intelligence Court Surveillance Act Of 1978 [pdf]
The NSA’s Section 702 minimization rules expose how the agency can collect, keep, and use Americans’ communications without warrants, despite claiming to target only foreigners. While the document sets out procedures for handling U.S. data, it includes broad loopholes—like keeping “inadvertently” collected domestic messages for years, sharing unfiltered data with the FBI, CIA, and even foreign governments, and giving NSA analysts wide discretion over who gets surveilled—all under secret FISA Court approval.
People: Holder, Eric H. Jr. -
Sensitive Targeting Authorisation [pdf]
A GCHQ internal form template for Sensitive Targeting Authorisation (STA), used to obtain approval for surveillance targeting of individuals or organisations with sensitive nationalities or in sensitive locations, covering both real-time tasking and historical database datamining, with separate authorisation tracks for overseas targets and UK-based targets.