Tag: compliance 28 documents
Search documents matching “compliance” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Discovery SIGINT Targeting Scenarios and Compliance [pdf]
This document is a top-secret NSA guidance manual detailing SIGINT targeting scenarios, compliance procedures, and legal guidance for querying foreign actors, malware, and potentially U.S.-linked systems, including considerations for minimizing incidental collection of U.S. persons’ communications. It outlines specific rules, approvals, and exceptions for using SIGINT tools, foreign intelligence tasks, and cases involving ambiguous or dual-use selectors like WikiLeaks, The Pirate Bay, and foreign actors operating through U.S. infrastructure.
-
Intelligence Oversight Training -- Register Your Compliance SIDtoday [pdf]
Each year, SID employees must complete Intelligence Oversight training, to be reported to NSA's Inspector General office. As of September 8, 2004, only 60 percent of the workforce completed their training, and that needed to be 100 percent by September 30. The article explains who must complete this process, what reading materials they must review (legal documents that justify NSA's surveillance authorities), where to access this reading material, when it's due, and why. ("The basic principles behind these documents is the right to privacy.")
The Intercept ↗ (2017-04-24) -
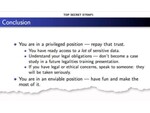
Access to the future [pdf]
The conclusion slide excerpt of a GCHQ presentation on TEMPORA, telling analysts they are in a "privileged" and "enviable" position with ready access to a great deal of sensitive data, and to "have fun and make the most of it".
Programs: TEMPORA -
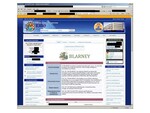
BLARNEY program overview [pdf]
The document is an NSA Special Source Operations (SSO) portal page screenshot for the BLARNEY program, describing it as a top-secret collection initiative established in the 1970s that leverages government and commercial partnerships to intercept foreign intelligence under FISA authority. It highlights BLARNEY’s major intelligence value—contributing heavily to counterterrorism reporting and the President’s Daily Brief—and lists its primary targets as diplomatic, economic, foreign government, and counterterrorism communications.
-
CADENCE Read Me [pdf]
This NSA engineering manual details how to configure XKEYSCORE—the agency's sprawling surveillance system—to integrate with CADENCE, an automated keyword scanning tool that filters intercepted communications and routes intelligence based on search terms submitted by analysts.
-
Committees: Are Your 'Papers' in Order? SIDtoday [pdf]
Agency committees or boards that meet on a regular basis are required to have an approved charter on file.
The Intercept ↗ (2018-08-15) -
FISA Amendments Act of 2008 Section 702 summary document [pdf]
This document summarizes the way the law works and describes the three types of certifications used to permit the surveillance, as well as targeting and minimization procedures. The three certification are for foreign governments, counterterrorism and WMD/proliferation.
-
Guidance from the SIGINT Director on Machine Room Management Procedures SIDtoday [pdf]
Signals Intelligence Director Richard Quirk urges compliance with a new set of procedures for cryptologic machine rooms rolled out by the IT directorate.
People: Quirk, RichardThe Intercept ↗ (2018-03-01) -
HRA auditing [pdf]
This GCHQ internal wiki page provides detailed procedural guidance for conducting Human Rights Act (HRA) compliance audits of analyst activities using surveillance databases like BROAD OAK and Events, establishing quarterly and six-monthly random sampling schedules, defining compliance metrics (Red <75%, Amber 75-94%, Green ≥95%), and specifying the responsibilities of analysts, auditors, and business unit heads to demonstrate that targeting, tasking, and examination of intercept content or metadata meet legal requirements for necessity and proportionality.
Marking: UK CONFIDENTIAL -
Intelligence Oversight Training: Webpage Access Restored SIDtoday [pdf]
The Oversight Training Webpage is on a new server and is now working.
The Intercept ↗ (2016-12-07) -
Is There a Sustainable Ops Tempo in S2? How Can Analysts Deal with the Flood of Collection? SIDtoday [pdf]
The NSA's Deputy Director for Analysis and Production discusses the unsustainable operational tempo caused by overwhelming data collection volumes, advocating for "Analytic Modernization" that would shift from treating SIGINT as "radioactive" NSA-only material to sharing raw intelligence with other agencies for collaborative exploitation.
Programs: A-SPACE -
Keeping Congress Informed SIDtoday [pdf]
A "Congressional Notification" is a letter the NSA sends to various congressional committees to inform them of a "significant intelligence activity" or a "significant intelligence failure," as required by the National Security Act of 1947. The article lists defining criteria for a "significant activity" or a "significant intelligence failure."
The Intercept ↗ (2016-12-07) -
New Contact-Chaining Procedures to Allow Better, Faster Analysis SIDtoday [pdf]
The SIGINT Management Directive 424 briefing (Jan 2011) announces a major procedural shift at the NSA, allowing analysts to conduct contact chaining and large-scale metadata analysis from any selector, regardless of nationality or location. This change removes prior restrictions on U.S. data, enabling more powerful social network mapping for foreign intelligence purposes.
Programs: GATEKEEPER -
New Intelligence Oversight Training Process SIDtoday [pdf]
Each year, as part of Intelligence Oversight training, all SID employees are required to read the five legal documents that govern SID's mission. "The basic principle behind these documents is the right to privacy. Since the SID mission involves electronic surveillance, it is subject to strict control under the U.S. Constitution."
The Intercept ↗ (2016-12-07) -
NSA document on targeting Five Eyes countries and territories [pdf]
This document states that the National Security Agency is prohibited from conducting foreign surveillance on the "Five Eyes" countries, which include U.S. allies Australia, Canada, New Zealand and the United Kingdom, or their territories.
-
OIG Inspection and Audit Schedule for 2004 Unveiled SIDtoday [pdf]
The NSA's Office of the Inspector General releases its audit and inspection schedule for 2004.
The Intercept ↗ (2016-12-07) -
OIG Inspection and Audit Schedule for 2004 Unveiled (repost) SIDtoday [pdf]
(Repost) The NSA's Office of the Inspector General releases its audit and inspection schedule for 2004.
Marking: SECRETThe Intercept ↗ (2016-12-07) -
Preparing for the SID 2007 Inventory, a Look at SID's 2006 Inventory Pitfalls SIDtoday [pdf]
The 2006 SID property inventory succeeded in locating 99.44% or SID's equipment. Only 232 of over 40,000 items were lost. Better compliance with documentation can improve the results in 2007.
Programs: DPASThe Intercept ↗ (2019-05-29) -
Required Reading... SIDtoday [pdf]
All Signals Intelligence Directorate employees are required to annually review the legal and policy documents guaranteeing U.S. citizens' right to privacy.
People: Quirk, RichardThe Intercept ↗ (2017-09-13) -
Sensitive Targeting Authorisation [pdf]
A GCHQ internal form template for Sensitive Targeting Authorisation (STA), used to obtain approval for surveillance targeting of individuals or organisations with sensitive nationalities or in sensitive locations, covering both real-time tasking and historical database datamining, with separate authorisation tracks for overseas targets and UK-based targets.