Tag: smartphone exploitation 4 documents
Search documents matching “smartphone exploitation” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Refine (combine with another filter, via search)
Sort: Title
Documents
-
How the NSA Accesses Smartphone Data [pdf]
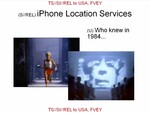
This document reveals how the NSA and its Five Eyes partners developed sophisticated methods to exploit iPhone location services and BlackBerry communications, framing smartphone users as “zombies” willingly sharing data. It includes examples of intercepted geolocation data and decrypted BlackBerry emails, illustrating targeted surveillance capabilities against both consumer and government communications.
-
Leaky phone apps [pdf]
These GCHQ slides describe the "WARRIOR PRIDE" mobile intrusion capability being ported to iPhone and Android, with plugins for power management, remote microphone, high‑precision geolocation, kernel stealth, and self‑protection. It claims the ability to retrieve almost any content from infected phones (SMS/MMS, email, call records, photos, calendar, etc.). Part of GCHQ's project "Mobile Applications Project".
Programs: Mobile Applications Project · WARRIORPRIDE · DREAMYSMURF · NOSEYSMURF · TRACKERSMURF · PORUS · PARANOIDSMURF -
Mobile Theme Briefing (May 28, 2010) [pdf]
This 2010 GCHQ briefing document outlines the “Mobile Applications Project,” which aims to expand intelligence capabilities to exploit the growing shift from fixed to mobile internet usage. It details objectives for targeting mobile apps and roaming network traffic (GRX), enabling converged analysis of voice, text, command-and-control, and geolocation data across multiple mobile platforms such as iPhone, Symbian, Android, and Windows Mobile. See also: EFF_-_20140128-guard-leaky_phone_apps_0 (includes other slides from the same slideset)
Programs: Mobile Applications Project -
Real Life Stats from GPRS work [pdf]
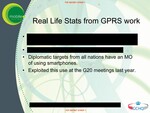
GCHQ’s TOP SECRET briefing touts real-time interception of diplomats’ smartphone traffic at the 2009 G20—especially BlackBerry—feeding live messages and newly discovered selectors to analysts and UK ministers to shape summit outcomes. It’s a snapshot of summit espionage turned into a policy tool: exploit the smartphone dependence of foreign delegations, deliver actionable SIGINT on demand.
“GCHQ intercepted foreign politicians' communications at G20 summits” - The Guardian ↗ (2013-06-16) · “For the NSA, espionage was a means to strengthen the US position in climate negotiations” - Dagbladet Information ↗ (2014-01-30) · MacAskill, Ewen · Davies, Nick · Hopkins, Nick · Borger, Julian · Ball, James · Gjerding, Sebastian · Geist, Anton · Moltke, Henrik · Poitras, Laura