Genre: other 148 documents
Search documents matching “other” →What kind of document it is: slides, report, wiki, manual, guide, newsletter.
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Where we are [pdf]
This GCHQ document is a table tracking the agency's access to undersea fiber-optic cables as of an unspecified date, listing 13 cables with their codenames, telecommunications company partners (primarily "GERONTIC"/Cable & Wireless and "REMEDY"), and the capacity of data access and egress points measured in 10 gigabit connections. The table shows GCHQ had access to 592 10-gigabit connections across these cables with 69 egress points, with an unlabelled column totalling 2,960, with GERONTIC (Cable & Wireless) providing access to 9 of the 13 cables including FEA (NIGELLA), APOLLO North and South, and TAT-14S.
Programs: NUMDAH · SCEPTRE · NIGELLA · LATUS · ARCANO · MONDELLO · GIBUS · KIRKISTOWN · LINNELL · ELAPSE · GRASP · CATEGORY · KNAPWEED · DACRON · GERONTIC · REMEDY · SOLAS · APOLLO · FEA · SMW3“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Where we want to be [pdf]
This GCHQ document outlines the agency's aspirational expansion plans for undersea cable surveillance, showing desired access to 24 cables (compared to 13 in the "Where we are" document) with a dramatic increase in surveillance capacity to 1,693 10-gigabit connections and 390 egress points—nearly triple the existing infrastructure. The document includes eight cables with generic names (Cable X, Y, Z and A to E), five of them with blank relationship fields, suggesting GCHQ was actively pursuing partnerships with additional telecommunications companies beyond GERONTIC (Cable & Wireless), REMEDY, DACRON, and newly mentioned partners STELLABLUE, PINNAGE, and LITTLE to achieve comprehensive global communications interception.
Programs: NUMDAH · SCEPTRE · HIASCO · NIGELLA · LATUS · PRESCOTT · ARCANO · MONDELLO · KIRKISTOWN · LINNELL · ELAPSE · CATEGORY · KNAPWEED · STELLABLUE · GRASP · VISAGE · REMEDY · GERONTIC · DACRON · PINNAGE · LITTLE“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
WINDSTOP - Last 30 Days [pdf]
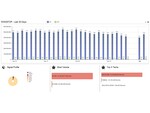
The WINDSTOP report shows massive NSA collection activity over a 30-day period, with daily DNI (Digital Network Intelligence) and DNR (Dialed Number Recognition) records reaching up to 600 million per day. Most data volume came from DS-300 and DS-200B collection points, processed primarily through XKEYSCORE and TURMOIL, and included a mix of signal types such as PCS, INMAR, MCIP, VSAT, and PSTN. The chart follows the same structure as BOUNDLESSINFORMANT, the NSA’s global SIGINT visualization tool, using bar and pie charts to track and categorize collection volume by signal type, SIGAD, and processing system.
-
WOLFRAMITE Encryption Attack [pdf]
The "WOLFRAMITE Encryption Attack" is a GCHQ strategic annex from March 2011 detailing a joint effort with the NSA to compromise the A5/3 encryption standard. The document outlines a specialized research and development program aimed at scaling up handset exploitation and securing funding—estimated at approximately £4 million—to prototype a functional decryption attack against modern mobile broadband security.
-
XKeyscore rules [pdf]
XKeyscore fingerprint and plug-in source code targeting Tor and other anonymity tools — the rules NSA used to flag anyone connecting to Tor directory servers, requesting Tor bridges, visiting the Tor Project or Tails websites, or researching the Tails operating system — including code that specifically excludes Five Eyes users while fingerprinting everyone else, and a note describing Tails as "a comsec mechanism advocated by extremists on extremist forums."
“NSA targets the privacy-conscious” - ARD ↗ (2014-07-03) · Appelbaum, Jacob · Gibson, Aaron · Goetz, John · Kabisch, Volkmar · Kampf, Lena · Ryge, Leif -
XKeyscore shared with Germany [pdf]
Document excerpt on the sharing of the NSA spy tool XKeyscore with the Federal Office for the Protection of the Constitution (BfV), Germany's domestic intelligence agency
Programs: XKEYSCORE -
ZAIN INTRANET NETWORK ENGINEERING [pdf]
2009 GCHQ report documents the sampling and tasking of a satellite data carrier linking Gabon and Belgium that carried the internal corporate intranet of telecom operator Zain (formerly MTC Vodafone), through which engineers exchanged technical data via SMTP email. The intercept surfaced email selectors belonging to staff across multiple telecom operators — including Zain subsidiaries, Orange Mali, Saudi Telecom, MTC Touch (Lebanon), Tunisie Telecom, and Celtel entities in Niger and Nigeria — reflecting the agency’s systematic targeting of telecom employees as a potential entry point into operators’ internal networks.
-
Zoom of a Boundless Informant document, with project names [pdf]
1 p.Programs: CHOCOLATESHIP · SCREAMINGHARPY · WILDCHOCOBO · MURPHYSLAW · WHISTLINGDIXIE · CHAOSOVERLORD · WAXTITAN · SHAREDTAFFY · POTBED · DARKTHUNDER · LUTEUSICARUS · JEEPFLEA · SHARPSHADOW · VALIDATOR