Tag: spoofing 2 documents
Search documents matching “spoofing” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Full-Spectrum Cyber Effects [pdf]
The leaked 2012 GCHQ JTRIG “Full-Spectrum Cyber Effects” presentation outlines the UK’s offensive cyber capabilities, detailing strategies to destroy, deny, degrade, disrupt, deceive, and influence targets across digital and physical domains. It describes a wide range of operations—from network attacks, spoofing, and psychological operations on social media to hotel surveillance (Royal Concierge), mobile tracking, and advanced vulnerability exploitation—demonstrating how GCHQ integrates cyber operations, intelligence, and information warfare on a global scale.
Programs: JTRIG · SALAMANCA · RADIUS · ROYAL CONCIERGE · BLACKHOLE · GUILTY SPARK · MIDDLESEX GREEN · PPF · HOTWIRE -
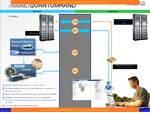
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.